
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Website of gunmaker Smith & Wesson hit by a Magecart attack

The US gunmaker Smith & Wesson was hacked late last month in a Magecart attack, attackers injected a malicious software skimmer. A new Magecart attack made the headlines, the victim is the American gunmaker Smith & Wesson. The hack took place last month, the attackers planted a malicious software skimmer on its website to steal […]

smith & wesson Magecart

The US gunmaker Smith & Wesson was hacked late last month in a Magecart attack, attackers injected a malicious software skimmer.

A new Magecart attack made the headlines, the victim is the American gunmaker Smith & Wesson. The hack took place last month, the attackers planted a malicious software skimmer on its website to steal customers’ payment card data.

The hack was discovered by the researcher Willem de Groot from security firm Sanguine Security, the attackers planted the software skimmer on the Smith & Wesson e-commerce on November 27.

The expert discovered that the software skimmer and the infrastructure identical to the campaign that impersonates Sanguine Security. Hacker registered skimming domains using de Groot name and disguises as Sanguine protection.

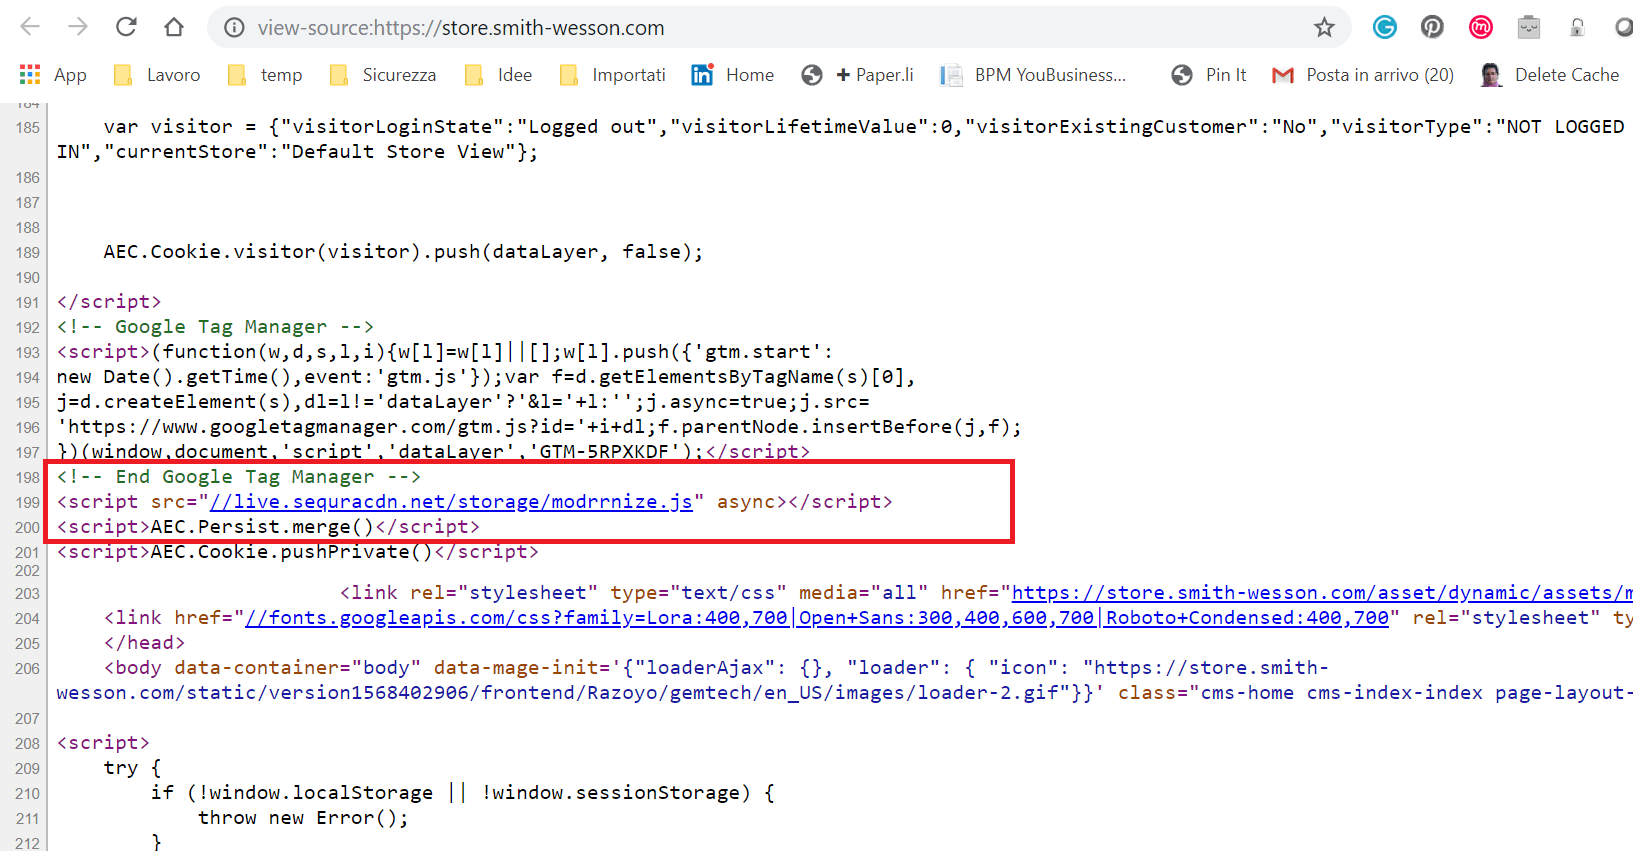
The compromised Smith & Wesson online store loads malicious code from a domain set up by the attackers, the malicious code was designed to capture personal and financial information provided by the users on the checkout page.

At the time of writing the software skimmer is still present on the online store:

live.sequracdn[.]net/storage/modrrnize.js  

smith & wesson Magecart

the script changes depending on the section of the site visited by the users.

“This script is not easy to spot as it will load a non-malicious or malicious script depending on the visitor and section of the site being visited.” reported BleepingComputer.

“For most of the site, the loaded JavaScript file looks like a normal 11KB and non-malicious script. However if you are using a US-based IP address, non-Linux browsers, not on the AWS platform, and at the checkout page, the script being delivered changes from 11KB to 20KB, with the Magecart portion appended to the bottom as shown below.”

The Smith & Wesson online store runs on Magento, attackers likely exploited a known vulnerability to compromise the system and inject the malicious code.

Earlier in November, Magento addressed a remote code execution vulnerability, tracked as CVE-2019-8144, that could allow unauthenticated attackers to deliver malicious payloads.

Users that have recently made purchases at smith-wesson.com are recommended to contact their credit card company and monitor your statements for suspicious activities.

In November, Macy’s started notifying some of its customers that crooks used a software skimmer to steal their personal and financial information.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, Magecart)

[adrotate banner=”5″]

[adrotate banner=”13″]


