
Researchers observed a SmokeLoader campaign that is distributing a new clipper malware dubbed Laplas Clipper that targets cryptocurrency users.
Cyble researchers uncovered a SmokeLoader campaign that is distributing community malware, such as SystemBC and Raccoon Stealer 2.0, along with a new clipper malware tracked as Laplas.
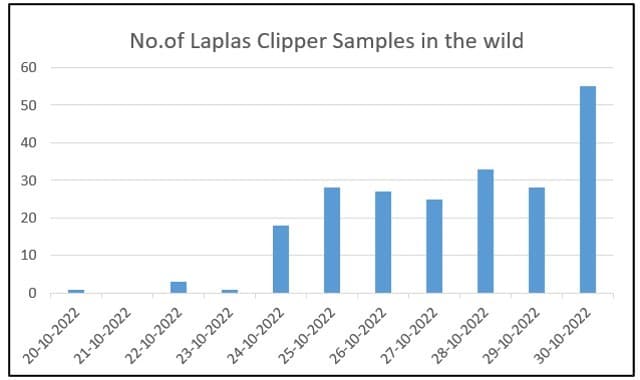
The experts detected more than 180 different samples of the clipper malware in the last two weeks, a circumstance that confirms that the threat has been widely deployed in recent weeks.

Clipper is a family of malware designed to hijack cryptocurrency transactions by swapping the victim’s wallet address with the wallet address owned by attackers.
Clipper malware monitors the clipboard of the victim’s system, then whenever the user copies data, it verifies if it is a valid cryptocurrency wallet address and replaces it with the attackers’ wallet address.
Laplas is new clipper malware that generates a wallet address similar to the victim’s wallet address. The victim will not notice the difference in the address, which significantly increases the chances of successful clipper activity.
Laplas uses a trick to avoid detection, it generates a wallet address similar to the victim’s wallet address.
“Laplas is new clipper malware that generates a wallet address similar to the victim’s wallet address. The victim will not notice the difference in the address, which significantly increases the chances of successful clipper activity.” reads the post published by Cyble.
This clipper can target multiple wallets, including Bitcoin, Ethereum, Bitcoin Cash, Litecoin, Dogecoin, Monero, Ripple, ZCash, Dash, Ronin, Tron, and Steam Trade URL.
Below are the pricing options for the Laplas Clipper:
- $29 / 1 Sunday
- $59 / 1 month
- $159 / 3 months
- $299 / 6 months
- $549 / 1 year
The clipper provides an easy to use dashboard that allows operators to check the status of infected computers and active TAs wallet address details.
“Smoke Loader is a well-known, highly configurable, effective malware that TAs are actively renovating. It is a modular malware, indicating it can get new execution instructions from C&C servers and download additional malware for expanded functionality. In this case, the TAs use three different malware families for financial gain and other malicious purposes.” concludes the report. “The RecordBreaker, a revived version of Raccoon Stealer, is used to steal sensitive information, the SystemBC is a multifunctional threat combining proxy and remote access trojan features, and the new Laplas clipper performs clipboard hijacking to steal cryptocurrency from victims.”
Follow me on Twitter: @securityaffairs and Facebook
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, Laplas clipper)
[adrotate banner=”5″]
[adrotate banner=”13″]


