
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

SNAKE Ransomware is targeting business networks

A new piece of ransomware called SNAKE appeared in threat landscape, the malware is now targeting company networks. The SNAKE is a new ransomware that is threatening enterprises worldwide along with most popular ransomware families such as Ryuk, Maze, Sodinokibi, LockerGoga, BitPaymer, DoppelPaymer, MegaCortex, LockerGoga. The scary trend sees criminal organizations targeting enterprises, instead of […]

SNAKE ransomware encrypted-folder

A new piece of ransomware called SNAKE appeared in threat landscape, the malware is now targeting company networks.

The SNAKE is a new ransomware that is threatening enterprises worldwide along with most popular ransomware families such as Ryuk, Maze, Sodinokibi, LockerGoga, BitPaymer, DoppelPaymer, MegaCortex, LockerGoga.

The scary trend sees criminal organizations targeting enterprises, instead of single users, using the above malware to maximize their profits.

Snake Ransomware was first detected by researchers from MalwareHunterTeam last week and analyzed it with the support of the popular malware analysts Vitali Kremez.

The ransomware is written in Golang and is heavily obfuscated, it is designed to target the entire network rather than individual computers or servers.

“The ransomware contains a level of routine obfuscation not previously and typically seen coupled with the targeted approach,” Kremez, Head of SentinelLabs, told BleepingComputer.

Like other ransomware, upon execution Snake will remove the computer’s Shadow Volume Copies, it also kills numerous processes related to SCADA systems, virtual machines, industrial control systems, remote management tools, network management software, and more.

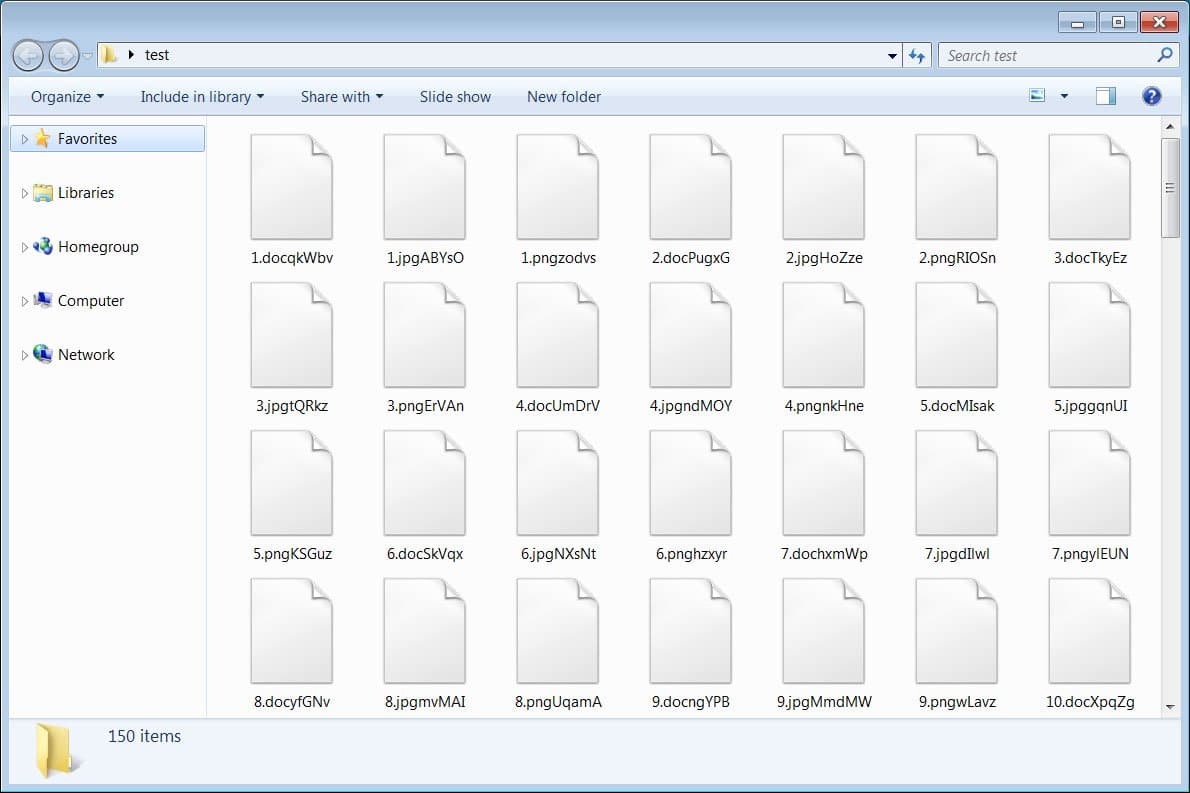
Then the malware encrypts the files on the system, skipping Windows system files and folders. The SNAKE ransomware appends a ransom 5 character string to the files extension (i.e. a file named invoice.doc is encrypted and renamed like invoice.docIksrt.

The experts noticed that the malware appends the ‘EKANS‘ file marker to each encrypted file.

SNAKE ransomware encrypted-folder

“BleepingComputer has tested many ransomware infections since 2013 and for some reason, it took Snake particularly long time to encrypt our small test box compared to many other ransomware infections.” reads the analysis published by BleepingComputer.

“As this is targeted ransomware that is executed at the time of the attacker’s choosing, this may not be that much of a problem as the encryption will most likely occur after hours.”

Once the encryption process is completed the ransomware will create a ransom note (named ‘Fix-Your-Files.txt’) in the C:\Users\Public\Desktop folder that contains the email address (bapcocrypt@ctemplar.com) to contact to receive the payment instructions.

According to BleepingComputer, the gang is offering the decryptor for the entire network and not individual machines.

Technical details, including IoCs, are reported in the analysis published by BleepingComputer.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – SNAKE ransomware, malware)

[adrotate banner=”5″]

[adrotate banner=”13″]


