
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Snooping Samsung S6 calls with bogus base stations

A duo of security researchers, Daniel Komaromy of San Francisco and Nico Golde of Berlin, demonstrated how to intercept calls using bogus base stations. PacSec Modern Samsung devices, including the last generation Samsung S6, S6 Edge and Note 4, are vulnerable to phone eavesdropping. A duo of experts, Daniel Komaromy of San Francisco and Nico […]

Snooping Samsung S6 calls with bogus base stations

A duo of security researchers, Daniel Komaromy of San Francisco and Nico Golde of Berlin, demonstrated how to intercept calls using bogus base stations.

PacSec Modern Samsung devices, including the last generation Samsung S6, S6 Edge and Note 4, are vulnerable to phone eavesdropping. A duo of experts, Daniel Komaromy of San Francisco and Nico Golde of Berlin, demonstrated that is possible to intercept calls using malicious base stations.

The duo demonstrated the attacks on Samsung’s ‘Shannon’ line of baseband chips at the Mobile Pwn2Own competition at PacSec held in Toyko. Obviously the researchers haven’t publicly disclosed the details of their attack, they reported it to Samsung instead.
base stations MITM hack Samsung S6

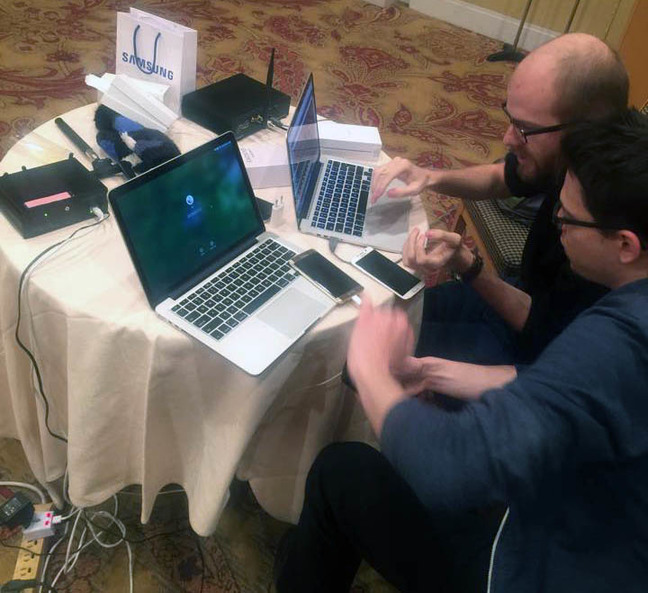
Nico Golde and Daniel Komaromy at Pwn2Own today. (Drago Ruiu)

The experts targeted Samsung devices, including the Samsung S6, with a man-in-the-middle attack relying on an OpenBTS base station, tricking the handsets and forcing it to connect to the bogus station. Once connected to the bogus base station, the handset receives the baseband processor firmware, the module which is responsible handling voice calls.

“Our example of modifying the baseband to hijack calls is just an example,” Komaromy told Vulture South. “The idea with hijacking would be that you can redirect calls to a proxy (like a SIP proxy) and that way you can man-in-the-middle the call.” “So that means the caller sees her original call connected – but it can be recorded in the proxy [which is how] it’s like a wiretap implant.”

The attack works on Samsung S6 Edge running up updated software.

“I turned it on next to their radio and then dialled myself,” said PacSec organiser Dragos Ruiu. “And instead of ringing on my phone it rang on theirs.”

Stay tuned.

Pierluigi Paganini

Security Affairs –  (Samsung S6, hacking)


