
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Sodinokibi gang hacked law firm of the celebrities and threatens to release the docs

The Sodinokibi ransomware gang stolen gigabytes of legal documents from the law firm of the stars, Grubman Shire Meiselas & Sacks (GSMLaw). The Sodinokibi ransomware group claims to have stolen gigabytes of legal documents from the entertainment and law firm Grubman Shire Meiselas & Sacks (GSMLaw) that has dozens of international stars and celebrities among […]

Sodinokibi ransomware Grubman Shire Meiselas & Sacks (GSMLaw)

The Sodinokibi ransomware gang stolen gigabytes of legal documents from the law firm of the stars, Grubman Shire Meiselas & Sacks (GSMLaw).

The Sodinokibi ransomware group claims to have stolen gigabytes of legal documents from the entertainment and law firm Grubman Shire Meiselas & Sacks (GSMLaw) that has dozens of international stars and celebrities among its clients.

The list of clients of the law firm includes famous artists like Chris Brown, Madonna, Lady Gaga, Nicki Minaj, Elton John, Timbaland, Robert de Niro, Usher, U2, and Timbaland.

The group threatens to release the stolen documents if the law firm will not pay the ransom.

The entertainment claims to have the “ability to advise and service clients in all aspects of their careers and businesses is unparalleled.”

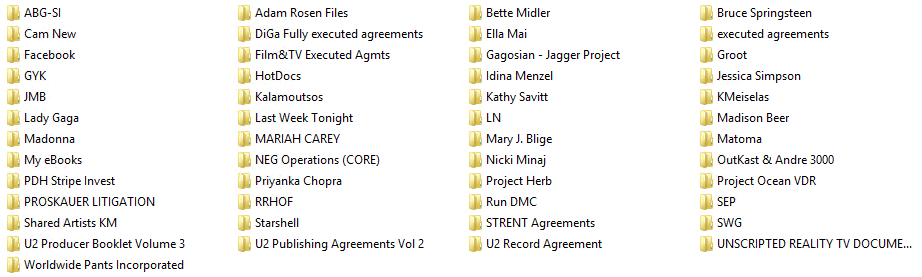
The Sodinokibi ransomware gang has published a screenshot of the folders they have stolen from the law firm.

The hackers also provided excerpts from legal agreements signed by artists, including Christina Aguilera.

The huge trove of documents, a 756 GB dump, includes contracts, phone numbers, email addresses, personal correspondence, non-disclosure agreements, and social security numbers.

The Sodinokibi ransomware operators are considered a dangerous threat that already targeted several organizations worldwide, including the SeaChange video platform, the Kenneth Cole fashion firm, and the UK-based currency exchange Travelex currency exchange.

Since April, the gang has started accepting the Monero cryptocurrency instead of Bitcoin to make it harder investigation by law enforcement agencies.

Please vote Security Affairs for European Cybersecurity Blogger Awards – VOTE FOR YOUR WINNERS
https://docs.google.com/forms/d/e/1FAIpQLSe8AkYMfAAwJ4JZzYRm8GfsJCDON8q83C9_wu5u10sNAt_CcA/viewform

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – Sodinokibi ransomware, hacking)

[adrotate banner=”5″]

[adrotate banner=”13″]


