
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

APT

Kaspersky – Sofacy ‘s campaigns overlap with other APT groups’ operations

According to Kaspersky, the Sofacy APT is particularly interested in military, defense and diplomatic entities in the far east, but overlap with other APT’s operations makes hard the attribution. Last week, during the Kaspersky Security Analyst Summit (SAS) held in Cancun, researchers from Kaspersky illustrated the results of their investigation on the recent activities conducted by the […]

Kaspersky – Sofacy ‘s campaigns overlap with other APT groups’ operations

According to Kaspersky, the Sofacy APT is particularly interested in military, defense and diplomatic entities in the far east, but overlap with other APT’s operations makes hard the attribution.

Last week, during the Kaspersky Security Analyst Summit (SAS) held in Cancun, researchers from Kaspersky illustrated the results of their investigation on the recent activities conducted by the dreaded Sofacy APT group.

The experts confirmed the news reported by Kaspersky three weeks ago, the Russia-linked APT28 group (aka Pawn Storm, Fancy Bear, Sofacy, Sednit, Tsar Team and Strontium.) have shifted focus in their interest, from NATO member countries and Ukraine to towards the Middle East and Central Asia.

According to Kaspersky researcher Kurt Baumgartner, the Sofacy APT is particularly interested in military, defense and diplomatic entities in the far east.

The researchers explained that the Russian APT group’s activity overlaps with cyber espionage campaigns conducted by other threat actors.

Baumgartner pointed out that the Zerbrocy malware used by Sofacy APT was discovered on machines that had also been infected with the Mosquito backdoor associated with Russian Turla APT. Baumgartner also explained that Sofacy SPLM malware has infected the same systems that were compromised by Danti China-linked APT.

In similar circumstances, the Kaspersky researchers found that the systems infected by the SPLM malware (aka CHOPSTICK and X-Agent) had been previously infected with other Turla malware.

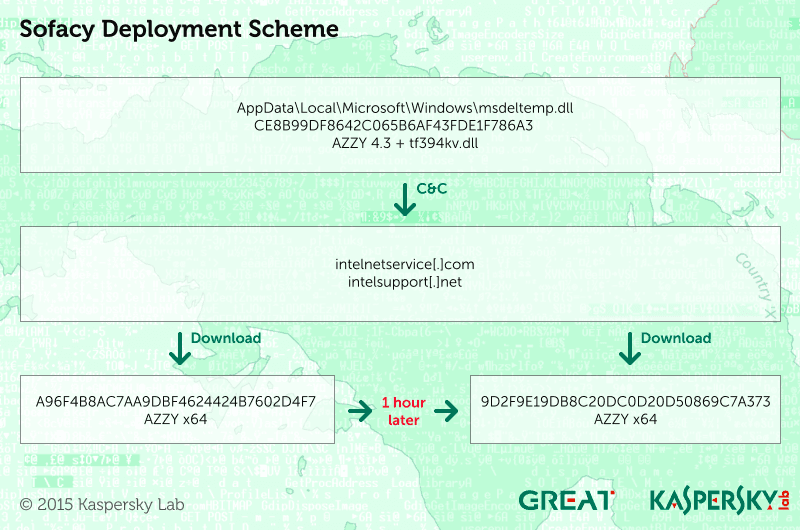
Sofacy backdoor

Kaspersky noticed that the overlaps were frequent on systems belonging to government, technology, and military organizations in Central Asia.

Another case of evident overlap was between Sofacy and the Longhorn threat actor, a group that researchers at Symantec reportedly linked to the CIA due to the use of Vault 7 tools. At least a server belonging to a military and aerospace conglomerate in China was infected by Sofacy backdoors and Longhorn malware.

Of course, even in presence of overlap, it is difficult to attribute the infection to a specific actor because APT groups use to plant false flags.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(Security Affairs – APT, cyber espionage)

[adrotate banner=”5″]

[adrotate banner=”13″]


