
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

VMware and Cisco also impacted by the SolarWinds hack

The IT giants VMware and Cisco revealed they were impacted by the recently disclosed SolarWinds supply chain attack. VMware and Cisco confirmed to have been both impacted by the recent SolarWinds hack. A recent advisory published by the NSA is warning that Russian state-sponsored hackers are exploiting the recently patched CVE-2020-4006 VMware flaw to steal sensitive information from […]

SolarWinds NNSA

The IT giants VMware and Cisco revealed they were impacted by the recently disclosed SolarWinds supply chain attack.

VMware and Cisco confirmed to have been both impacted by the recent SolarWinds hack.

A recent advisory published by the NSA is warning that Russian state-sponsored hackers are exploiting the recently patched CVE-2020-4006 VMware flaw to steal sensitive information from their targets.

The CVE-2020-4006 flaw affects Workspace One Access, Access Connector, Identity Manager, and Identity Manager Connector.

The popular investigator Brian Krebs learned from sources that the threat actors behind the SolarWinds hack also exploited the VMware flaw.

Last week, VMware published a statement to confirm that it is not aware of attacks exploiting the CVE 2020-4006 flaw “in conjunction with the SolarWinds supply chain compromise.”

The company also added that it has not found any evidence of exploitation in its network.

“To date, VMware has received no notification that the CVE 2020-4006 was used in conjunction with the SolarWinds supply chain compromise.” reads the security advisory.

“In addition, while we have identified limited instances of the vulnerable Orion software in our own internal environment, our own internal investigation has not revealed any indication of exploitation. This has also been confirmed by SolarWinds own investigations to date.”

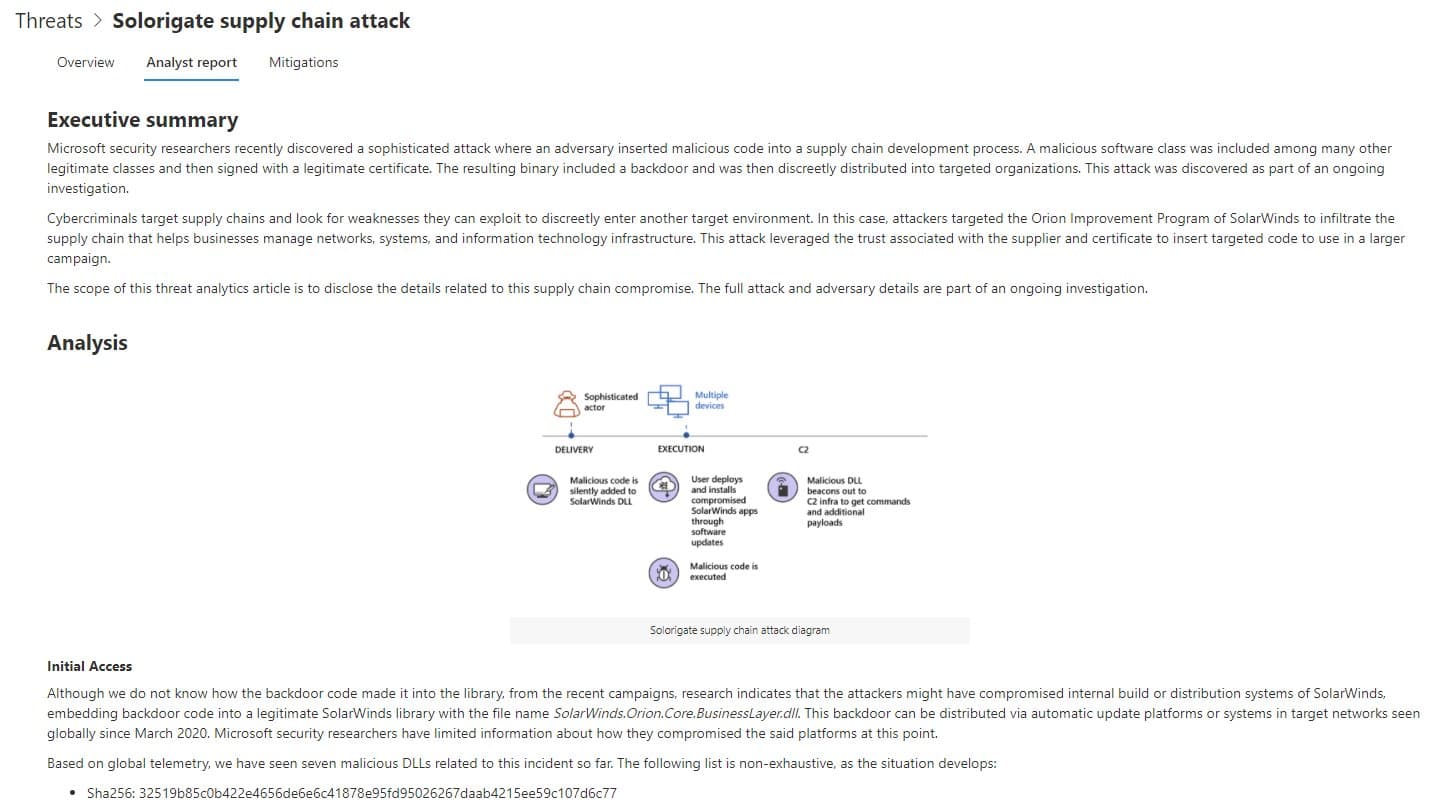
Cisco also confirmed to have found instances of the Solarwinds backdoor in a small number of lab environments and a limited number of employee endpoints.

“While Cisco does not use SolarWinds for its enterprise network management or monitoring, we have identified and mitigated affected software in a small number of lab environments and a limited number of employee endpoints.” reads the Cisco’s advisory. “we have identified and mitigated affected software in a small number of lab environments and a limited number of employee endpoints.”

Last week, Microsoft has confirmed that it was one of the companies breached in the recent SolarWinds supply chain attack, but the IT giant denied that the nation-state actors compromised its software supply-chain to infect its customers.

Unfortunately, the list of impacted organizations is long, SolarWinds revealed at least 18,000 of its customers may be impacted.

If you want to receive the weekly Security Affairs Newsletter for free subscribe here.

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, VMware)

[adrotate banner=”5″]

[adrotate banner=”13″]


