
Security Affairs
CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|FBI Blames North Korea for $6 Billion Binance Crypto Theft|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|FBI Blames North Korea for $6 Billion Binance Crypto Theft|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

CVE-2018-7783 flaw in Schneider SoMachine Basic can be exploited to read arbitrary files on the targeted system

Schneider Electric issued a security update for its EcoStruxure Machine Expert (aka SoMachine Basic) product that addresses a high severity vulnerability, tracked CVE-2018-7783, that could be exploited by a remote and unauthenticated attacker to obtain sensitive data. “SoMachine Basic suffers from an XML External Entity (XXE) vulnerability using the DTD parameter entities technique resulting in disclosure and […]

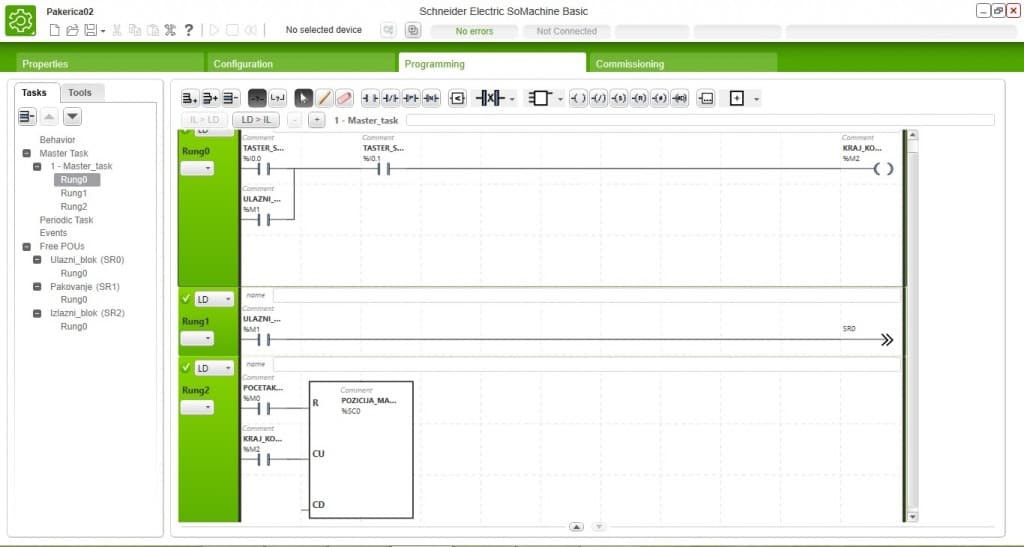
Schneider Electric SoMachine Basic

Schneider Electric issued a security update for its EcoStruxure Machine Expert (aka SoMachine Basic) product that addresses a high severity vulnerability, tracked CVE-2018-7783, that could be exploited by a remote and unauthenticated attacker to obtain sensitive data.

“SoMachine Basic suffers from an XML External Entity (XXE) vulnerability using the DTD parameter entities technique resulting in disclosure and retrieval of arbitrary data on the affected node via out-of-band (OOB) attack.” reads the security advisory published by Schneider Electric.

“The vulnerability is triggered when input passed to the xml parser is not sanitized while parsing the xml project/template file”

The EcoStruxure Machine Expert is a tool to program Schneider Modicon M221 programmable logic controller (PLC).

The ML external entity (XXE) vulnerability was discovered by the Gjoko Krstic, a researcher at industrial cybersecurity firm Applied Risk.

According to the expert, the flaw affects SoMachine Basic 1.6.0 build 61653, 1.5.5 SP1 build 60148, and likely earlier versions, it could be exploited by an attacker to launch an out-of-band (OOB) attack.

In order to exploit the flaw, the attacker has to trick victims to open a specially crafted SoMachine Basic project or template file.

Krstic also discovered that in certain circumstances the attackers can trigger the vulnerability for arbitrary code execution and to cause a denial-of-service (DoS) condition.

Schneider Electric addressed the vulnerability with the release of SoMachine Basic v1.6 SP1.

SoMachine Basic Schneider Electric

Early May, researchers at Tenable have disclosed technical details and a PoC code for a critical remote code execution vulnerability affecting Schneider Electric InduSoft Web Studio and InTouch Machine Edition products.

A few days ago, Schneider Electric published a security advisory to warn customers of multiple vulnerabilities in the Flexera FlexNet Publisher component used in the Schneider Electric Floating License Manager software in PlantStruxure PES.

One week ago, Schneider published another advisory to inform customers that these flaws also impact PlantStruxure PES.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(Security Affairs – SoMachine Basic, Schneider Electric)

[adrotate banner=”5″]

[adrotate banner=”13″]


