
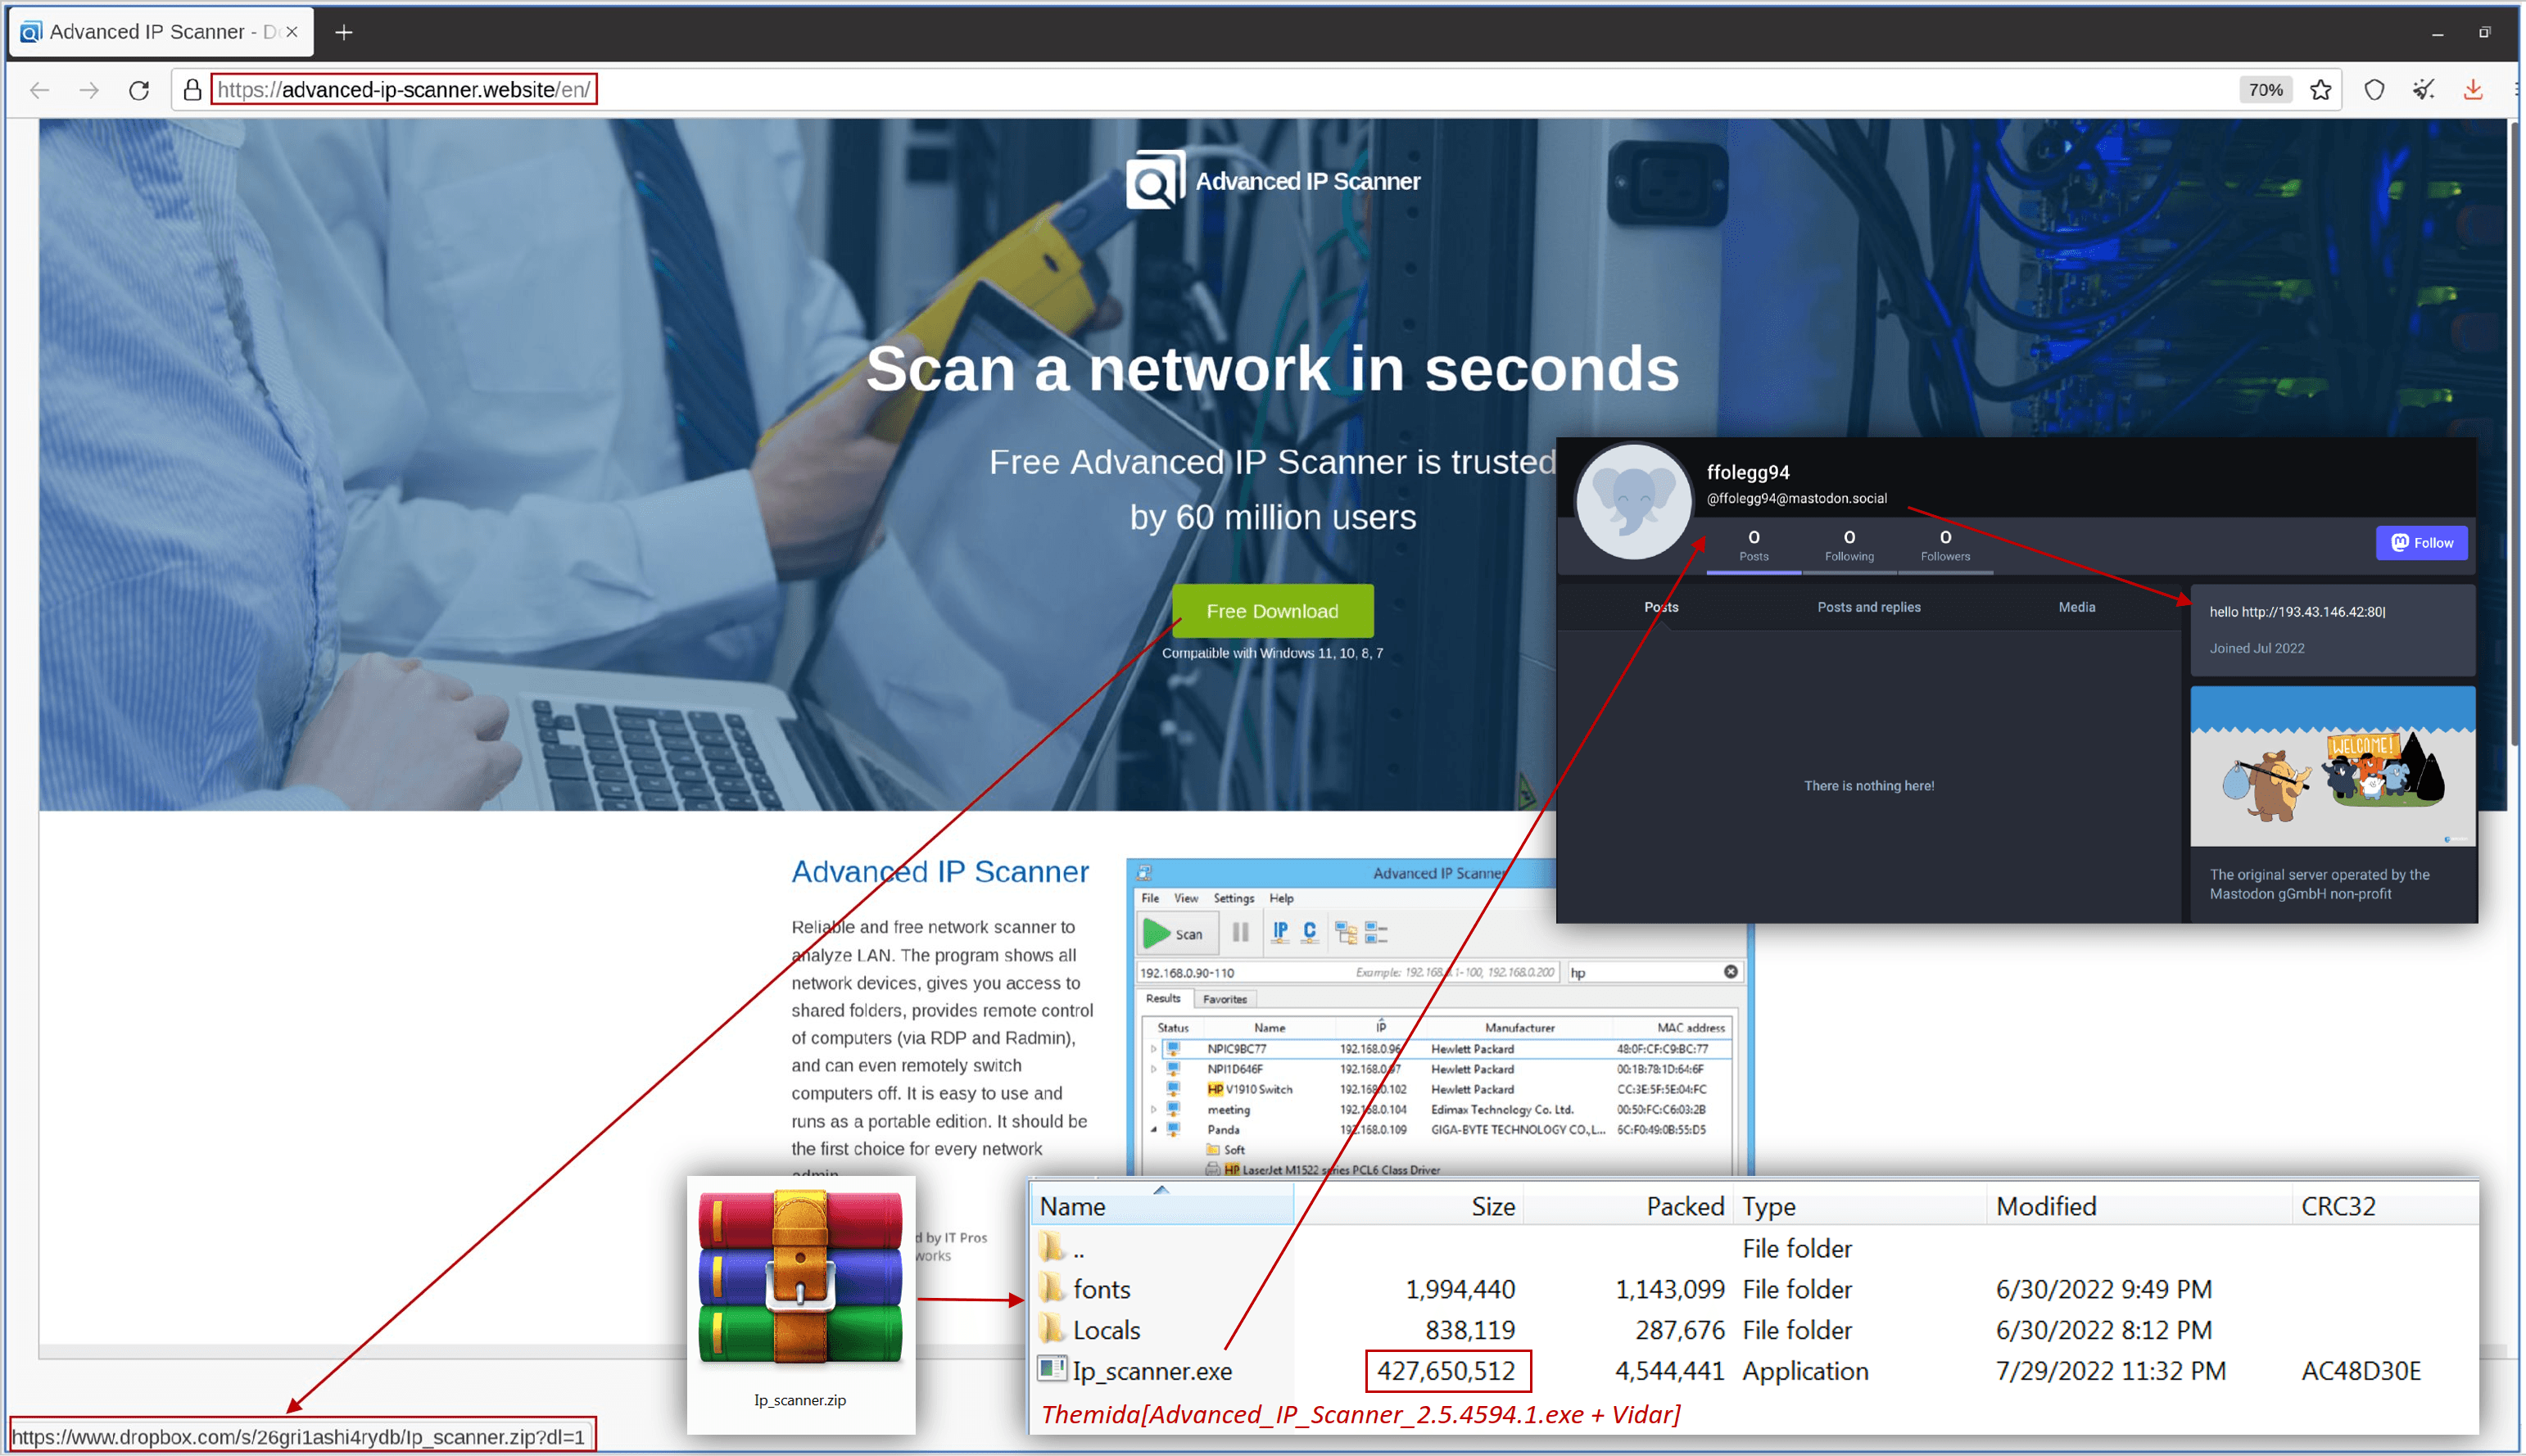
Russian threat actors employed a new ransomware family called Somnia in attacks against multiple organizations in Ukraine.
The Government Computer Emergency Response Team of Ukraine CERT-UA is investigating multiple attacks against organizations in Ukraine that involved a new piece of ransomware called Somnia.
Government experts attribute the attacks to the group ‘From Russia with Love’ (FRwL) (aka Z-Team, UAC-0118), which is believed to be a group of Pro-Russia hacktivists.
“FRwL (aka Z-Team), whose activity is monitored by CERT-UA under the identifier UAC-0118, took responsibility for the unauthorized intervention in the operation of automated systems and electronic computing machines of the target of the attack.” reads the advisory published by CERT-UA.
“The investigation found that the initial compromise occurred as a result of downloading and running a file that mimicked the “Advanced IP Scanner” software, but actually contained the Vidar malware.”
According to the alert, the Ukrainian organization was initially breached by a relevant access broker that then transferred the compromised data to the FRwL group that used it to carry out a cyber attack.
The “Advanced IP Scanner” software used as bait actually contained the Vidar malware, which is a data-stealing malware that is also able to capture Telegram session data and take over the victim’s account.

Then the threat actors abused the victim’s Telegram account to steal VPN configuration data (authentication and certificates). If the VPN accounts aren’t protected with two-factor authentication, threat actors can use a VPN connection to gain an unauthorized connection to the corporate network.
Once obtained access to the target network, the attackers conducted reconnaissance using tools like Netscan and deployed Cobalt Strike Beacons before exfiltrate data.
It is important to highlight that the threat actors behind Somnia attacks do not request the ransom payment, their operations aimed that disrupt the target’s networks.
CERT-UA also reported that the Somnia malware is evolving. The first version of the malware used the symmetric 3DES algorithm, while the second one used the AES algorithm.
“Note that the Somnia malware has also undergone changes. The first version of the program used the symmetric 3DES algorithm. In the second version, the AES algorithm is implemented; at the same time, taking into account the dynamics of the key and the initialization vector, this version of Somnia, according to the attackers’ theoretical plan, does not provide for the possibility of data decryption.” concludes the report.
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, Somnia)
[adrotate banner=”5″]
[adrotate banner=”13″]


