
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Experts uncovered a malspam campaign using Boeing 737 Max crashes

Experts at the 360 Threat Intelligence Center uncovered a new malspam campaign that leverages the tragic Boeing 737 Max crash to spread malware. Crooks always attempt to exploit the attention of the people on the events that made the headlines. In the last days, two events captured the attention of the media, the New Zealand […]

spam boeing 737 max-

Experts at the 360 Threat Intelligence Center uncovered a new malspam campaign that leverages the tragic Boeing 737 Max crash to spread malware.

Crooks always attempt to exploit the attention of the people on the events that made the headlines. In the last days, two events captured the attention of the media, the New Zealand mosque shooting and the tragic crash of the Boeing 737 Max in Ethiopia,

In the wake of the New Zealand mosque shooting, US CISA is recommending users to remain vigilant on possible scams and malware attacks.

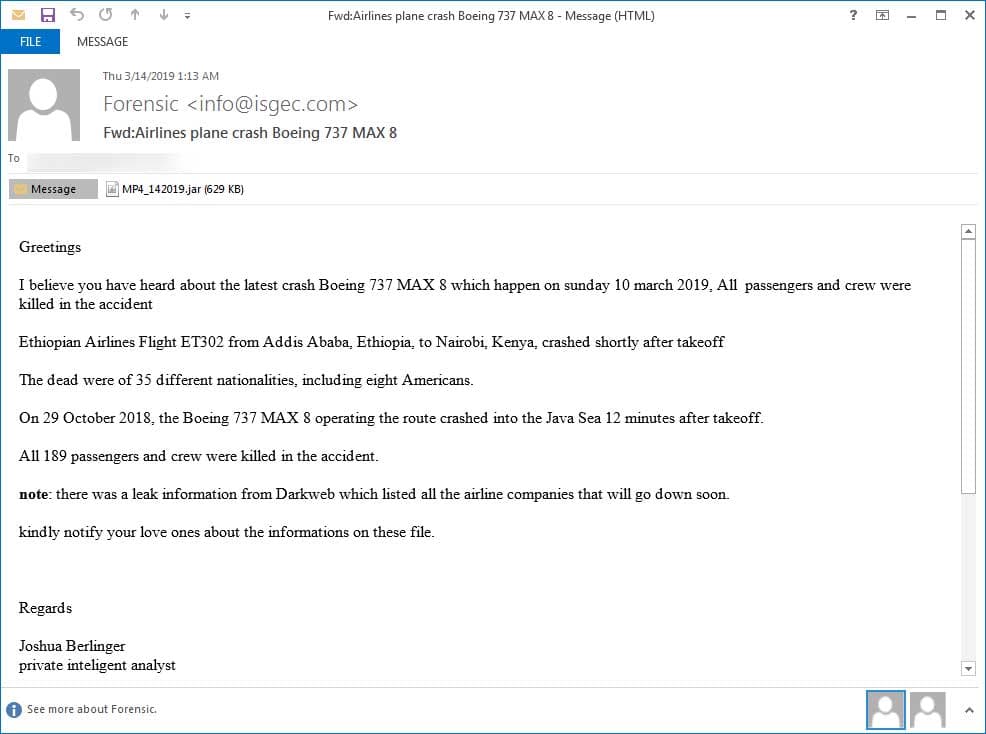
Now experts at the 360 Threat Intelligence Center have uncovered a new malspam campaign that leverages the tragic Boeing 737 Max crash to spread malware. Crooks used spam messages that pretend to be leaked documents about possible crashes of the Boeing 737 Max.

Crooks are using #Boeing hashtag in their campaign, spam messages were sent by the allegedly compromised email account at @IsgecPresses (info@isgec.com).

Threat actors are using a JAR file as an attachment (i.e. MP4_142019.jar) that acts as a dropper for the Houdini H-WORM RAT, spam emails have subject lines similar to “Fwd: Airlines plane crash Boeing 737 Max 8“.

spam boeing 737 max-

These emails pretend to be from a private intelligence analyst who found a leaked document on the dark web. This document pretends to contain information about other airline companies will be affected by similar crashes soon. 

Below the text used by crooks that was shared by BleepingComputer.

Greetings 

I believe you have heard about the latest crash Boeing 737 MAX 8 which happen on sunday 10 march 2019, All  passengers and crew were killed in the accident

Ethiopian Airlines Flight ET302 from Addis Ababa, Ethiopia, to Nairobi, Kenya, crashed shortly after takeoff 

The dead were of 35 different nationalities, including eight Americans.

On 29 October 2018, the Boeing 737 MAX 8 operating the route crashed into the Java Sea 12 minutes after takeoff.

All 189 passengers and crew were killed in the accident.

note: there was a leak information from Darkweb which listed all the airline companies that will go down soon.

kindly notify your love ones about the informations on these file.
 
Regards

Joshua Berlinger 
private inteligent analyst

If a user attempts to open the JAR file, it will be executed by JAVA on the computer. This attachment was originally thought to only install the Houdini H-worm Remote Access Trojan, but security

Security researcher Racco42 analyzed the JAR file after noticing its anomalous size and discovered running it through Any.Run that the malware was also installing the Adwind data-stealer Trojan.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – Boeing 737 Max, malspam)

[adrotate banner=”5″]

[adrotate banner=”13″]


