
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Miscreants hijacked the defunct SpamCannibal blacklist service

The SpamCannibal blacklist service was hijacked since Wednesday morning, attackers changed the DNS name server settings for the website overnight. The SpamCannibal was born to blacklist IP address of malicious servers involved in spam campaigns and DoS attacks. SpamCannibal was using a continually updated database containing the IP addresses of spam or DoS servers and blocks their […]

SpamCannibal

The SpamCannibal blacklist service was hijacked since Wednesday morning, attackers changed the DNS name server settings for the website overnight.

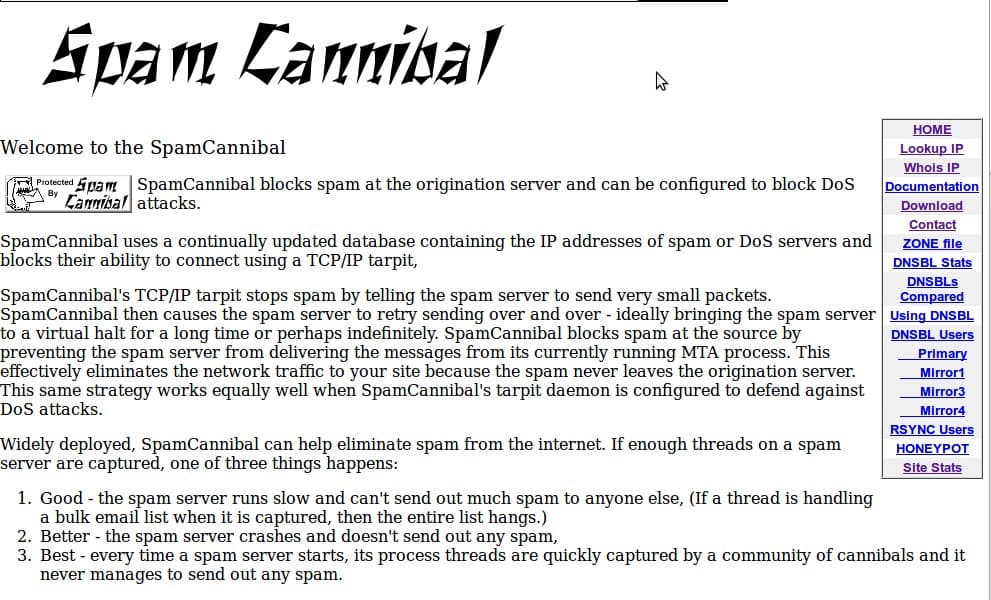
The SpamCannibal was born to blacklist IP address of malicious servers involved in spam campaigns and DoS attacks.

SpamCannibal was using a continually updated database containing the IP addresses of spam or DoS servers and blocks their ability to connect using services on a computer system that purposely delays incoming connections (aka TCP/IP tarpit).

The blacklist service was offline since last summer, but someone hijacked it on Wednesday morning, attackers changed the DNS name server settings for the website overnight.

SpamCannibal

The news was first reported by El Reg that was informed of the strange resurrection by a reader who told them that SpamCannibal was “pumping out Blacklist notifications for some of our servers and then when you go to spamcannibal.org, you get spam.”

“Visiting the site earlier today flung fake Adobe Flash updates at our sandboxed browser, downloads no doubt riddled with malware, so beware.” reads a blog post published by El Reg.

The DNS record for the blacklist service was changed to point at a rogue server controlled by attackers that likely used it to deliver malware and to alter the results of queries to the blacklist service.

https://twitter.com/GossiTheDog/status/1001778042400854016

All the users that queried the service to check an IP address to see if it is blacklisted as a spam source received always a positive result with serious consequences.

The attackers set a wildcard domain so that any subdomain of spamcannibal.org returns an IP address, with this trick the domain was interpreted as blacklisted.

Researcher Martijn Grooten believes the attack wasn’t targeted.

“This really looks like a standard domain takeover by some dodgy parking service. Doesn’t appear particularly targeted to Spamcannibal,” Grooten concluded.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(Security Affairs – hacking, DNS hijacking)

[adrotate banner=”5″]

[adrotate banner=”13″]


