
Ukraine CERT-UA warned of cyber attacks targeting defense forces with SPECTR malware as part of a cyber espionage campaign dubbed SickSync.
The Computer Emergency Response Team of Ukraine (CERT-UA) warned of cyber espionage campaign targeting defense forces in the country. The Ukrainian CERT attributes the attack to the threat actor UAC-0020 which employed a malware called SPECTR as part of the campaign tracked as SickSync.
The threat actor UAC-0020, aka Vermin, operates under the control of the law enforcement agencies of the temporarily occupied Luhansk.
The SPECTR malware has been active since at least 2019, it allows operators to steal sensitive data and files from the infected computer, it relies on the standard synchronization functionality of the legitimate SyncThing software.
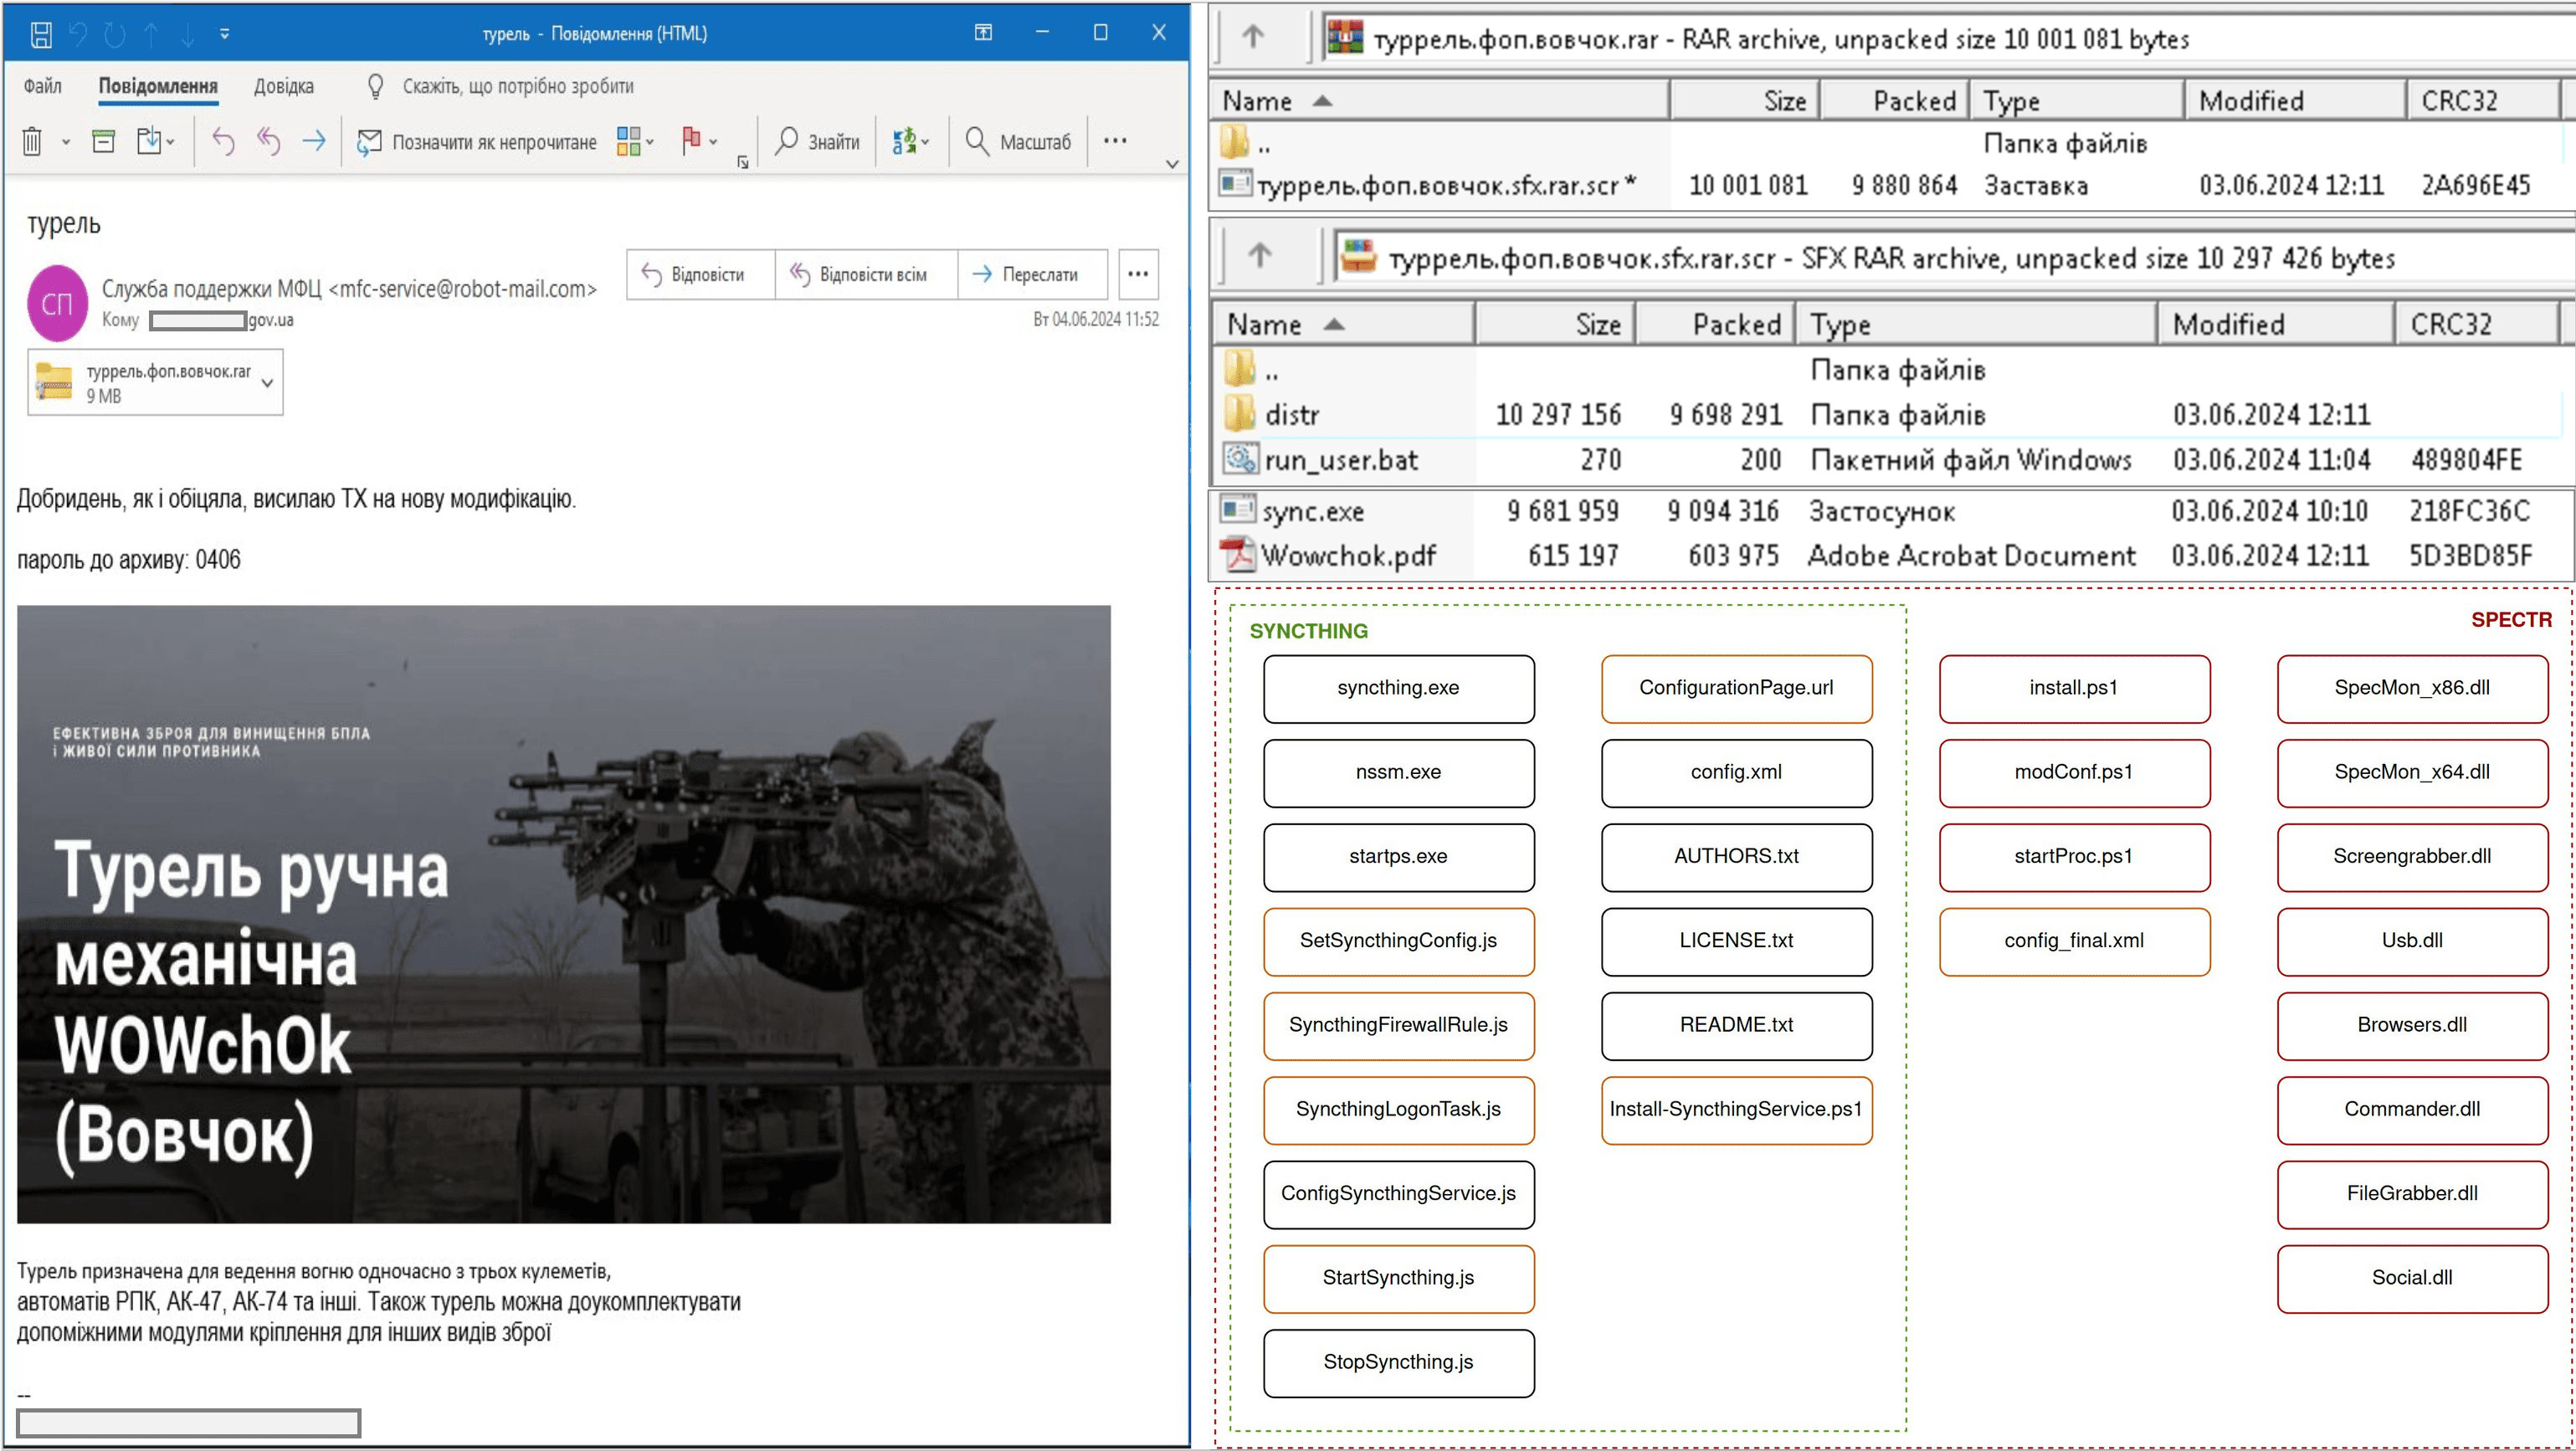
Threat actors sent out spear-phishing messages with an attachment in the form of a password-protected archive named “turrel.fop.vovchok.rar”.

The archive contains another archive, named RARSFX archive (“turrel.fop.ovchok.sfx.rar.scr”) that contains the “Wowchok.pdf” decoy file, the “sync.exe” EXE installer created using InnoSetup, and the BAT file ” run_user.bat” used for initial startup.
The UA-CERT states that the “sync.exe” file contains the legitimate SyncThing components and SPECTR malware files, including additional libraries and scripts. Attackers modified the standard files of the SyncThing software to change the names of directories, scheduled tasks, disable the functionality of displaying messages to the user, etc.
The SPECTR information stealer can capture screenshots every 10 seconds, collect files, extract data from removable USB drives, and steal credentials from web browsers and applications like Element, Signal, Skype, and Telegram.
“It should be noted that the stolen information is copied to subfolders in the directory %APPDATA%\sync\Slave_Sync\, after which, using the standard synchronization functionality of the legitimate program SyncThing , the contents of these directories get to the attacker’s computer, which ensures data exfiltration.” reads the report from the CERT-UA. “From the point of view of network indicators (in case of confidence in not using the mentioned technology is authorized), taking into account the establishment of a peer-to-peer connection, among other things, we recommend paying attention to signs of interaction with the SyncThing infrastructure: *.syncthing.net.”
The report also includes indicators of cyber threats.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, ThinkPHP)


