
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Hundreds of Spotify credentials leaked online

Security experts reported that hundreds of Spotify credentials appeared online and some users claim their accounts were hacked. Hundreds of Spotify account credentials appeared online on the website Pastebin, the information includes emails, usernames, passwords, account type and other details. The popular Swedish streaming service denied any data breach and confirmed that its systems weren’t […]

Hundreds of Spotify credentials leaked online

Security experts reported that hundreds of Spotify credentials appeared online and some users claim their accounts were hacked.

Hundreds of Spotify account credentials appeared online on the website Pastebin, the information includes emails, usernames, passwords, account type and other details.

The popular Swedish streaming service denied any data breach and confirmed that its systems weren’t compromised by hackers. Spotify confirmed that it “has not been hacked” and its “user records are secure.”

“Spotify has not been hacked and our user records are secure. We monitor Pastebin and other sites regularly. When we find Spotify credentials, we first verify that they are authentic, and if they are, we immediately notify affected users to change their passwords.” states Spotify.

According to the Techcrunch media agency, the Spotify security team proactively resets hacked passwords, a number of users are also reporting problems with their accounts.

Techcrunch reached out random users in the list confirming we’ve confirmed that these users’ Spotify accounts were compromised.

It is not clear if the account details were stolen by Spotify or result from other breaches.

The Pastebin post also includes other information on the uses (e.g. account type [family, premium], subscription auto-renews, country).
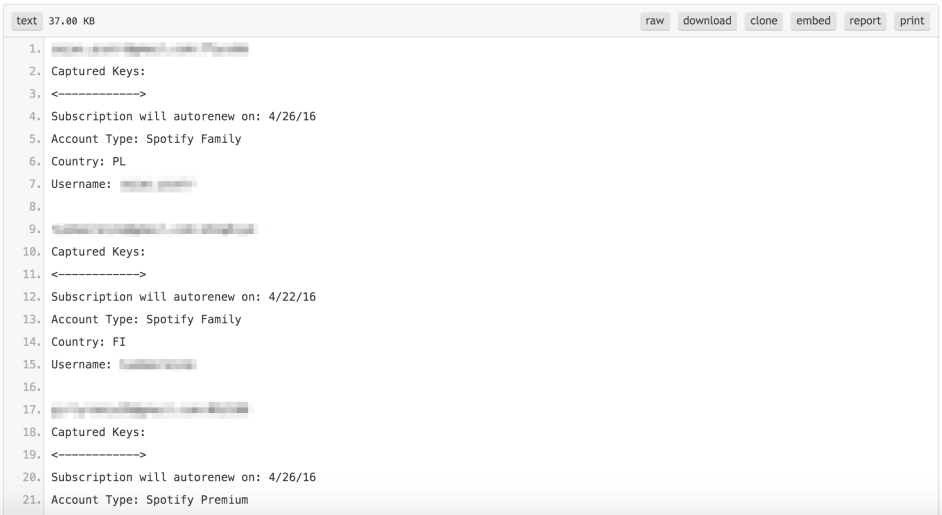
spotify credentials

This isn’t the first time that Spotify suffers a security incident, in May 2014 it investigated unauthorized access to its systems and internal company data.

We cannot exclude that data comes from previous incidents, but victims reached by Techcrunch told it otherwise.

“So far, over a half-dozen have responded, confirming that they did experience a Spotify account breach recently. They became aware of the breach in a number of ways – for example, one said he found songs added to his saved songs list that he hadn’t added. Another also found his account had been used by an unknown third party.” continues Techcrunch.

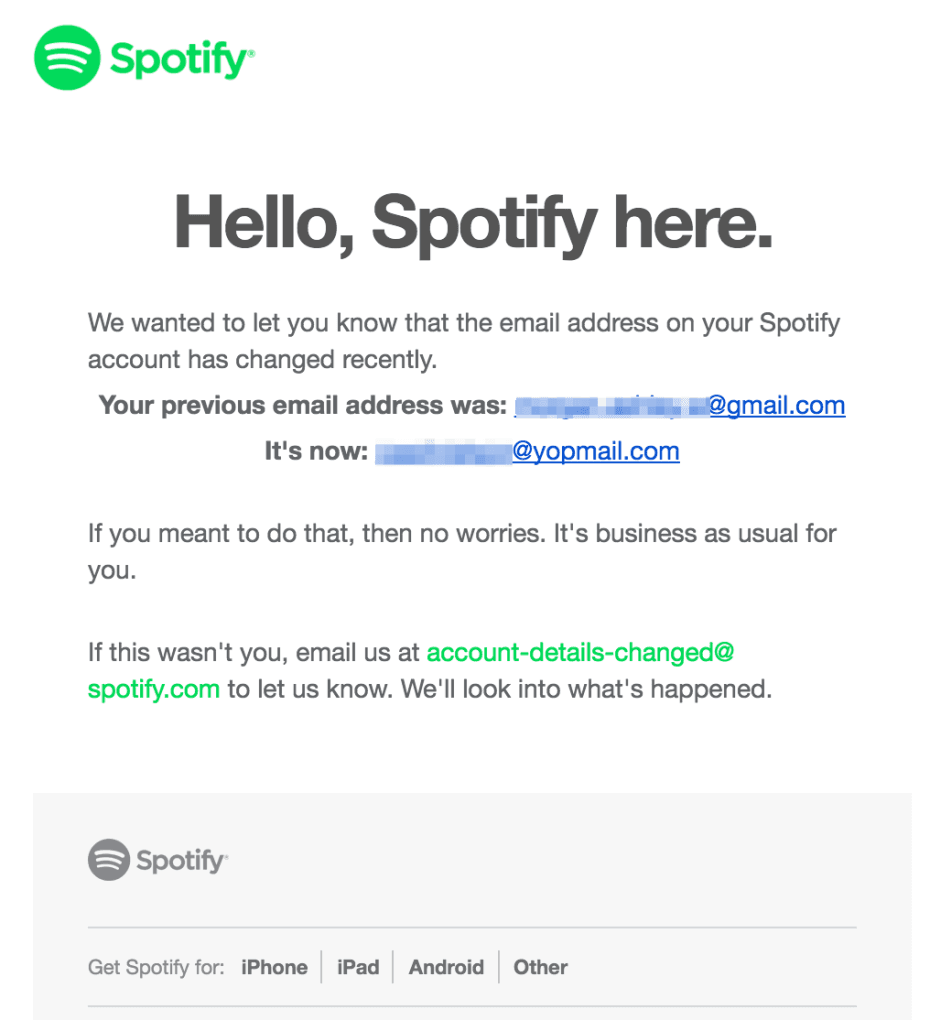
Some users reported problems while accessing the platform, other have found that their account email had been changed to a new email address not belonging to them.

Spotify email changed

As usually happens in these cases, it is strongly suggested to change passwords.

Stay tuned.

[adrotate banner=”9″]

Pierluigi Paganini

(Security Affairs – Spotify, data breach)


