
Threat actors in the wild are mass-scanning websites for directories containing SSH private keys to hack them.
The SSH allows a secure way to connect to servers hosting the websites, it allows administrators to get a terminal on them and enter commands.
The SSH authentication could rely on login credentials (username and password), or on a “key-based” approach.
When using key-based authentication, users generate an encryption key pair, a public and private key. The public key is placed on the server users want to sign in to. The private key is saved by the users in a local SSH configuration directory.
“Wordfence is seeing a significant spike in SSH private key scanning activity.” warned the WordPress security firm. “If your private SSH key ever gets out, anyone can use it to sign in to a server where you have set up key-based authentication. It is very important to keep your private key safe.”
Threat actors are mass-scanning the web searching for web directories containing the terms, or combinations of terms, such as “root,” “ssh,” or “id_rsa.”
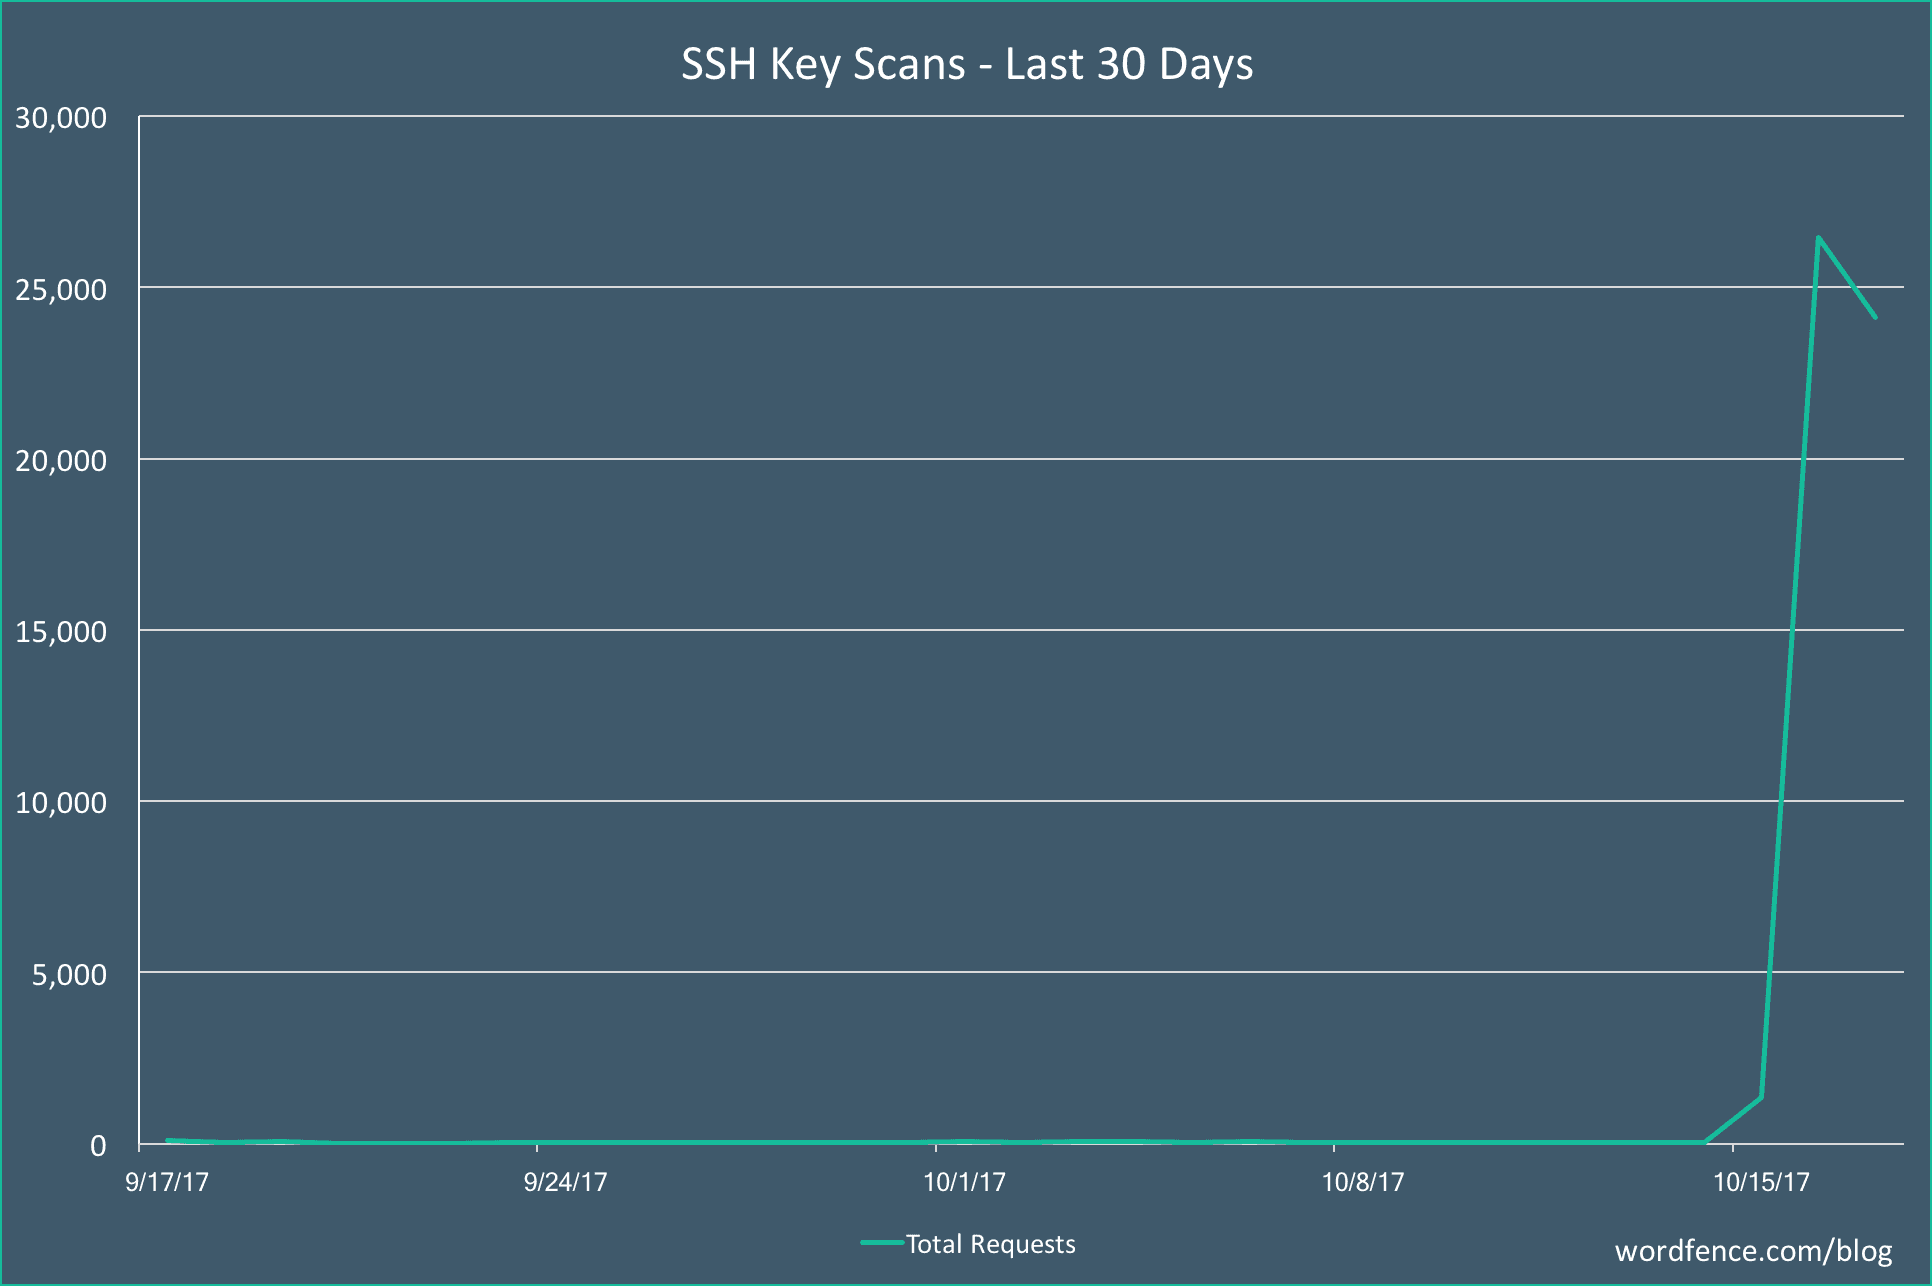
Researchers observed a spike in SSH Private Key scans in the past 48 hours.
“The graph shows a massive spike in scanning activity in the past 48 hours,” said Wordfence CEO Mark Maunder. “We think this increase of activity may indicate that an attacker is having some success scanning for private keys and has decided to increase their efforts. This may indicate a common bug or operational mistake that is being made by WordPress site owners, by which private keys are being accidentally made public.”

Recently the provider of identity protection services Venafi published a report that revealed that 61% of organizations have minimal control of SSH privileged access.
The company conducted a study among 410 IT security professionals and found “a widespread lack of SSH security controls.”
“Cybercriminals can abuse SSH keys to secure and automate administrator-to-machine and machine-to-machine access to critical business functions. According to Venafi’s research, even though SSH keys provide the highest levels of administrative access they are routinely untracked, unmanaged and poorly secured.” states the report.
Website administrators are advised to check if they haven’t accidentally uploaded their SSH private key on servers, or committed the SSH private key to Git or SVN repositories.
“Your SSH keys are usually kept in a private directory on your workstation. On Apple workstations, the keys are kept in the following directory:
/Users/<yourname>/.ssh/<key-filename>
On Windows workstations, the location where SSH keys are stored depends on which software you are using, so check your vendor documentation.” concluded Wordfence.
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(Security Affairs – SSH keys, hacking)
[adrotate banner=”5″]
[adrotate banner=”13″]


