
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Uncategorized

The Stuxnet vulnerability is still one of the most exploited flaws in the wild by hackers

A new report published by Kaspersky confirms that Stuxnet exploits targeting a Windows Shell Vulnerability is still widely adopted by threat actors. The case that I’m going to present to you demonstrates the importance of patch management and shows the effects of the militarization of cyberspace. Unpatched software is an easy target for hackers that can exploit […]

Stuxnet attack

A new report published by Kaspersky confirms that Stuxnet exploits targeting a Windows Shell Vulnerability is still widely adopted by threat actors.

The case that I’m going to present to you demonstrates the importance of patch management and shows the effects of the militarization of cyberspace.

Unpatched software is an easy target for hackers that can exploit old vulnerabilities to compromise the systems running them. Let’s consider, for example, the exploit code used in the notorious Stuxnet cyber weapon that hit the centrifuges at the Iranian nuclear plant at Natanz.

The flaw exploited by the Stuxnet worm was first patched by Microsoft in 2010, but threat actors in the wild continue to exploit it in a huge number of cyber attack.

According to Kaspersky Lab, the flaw used by Stuxnet to target Windows machines, tracked as CVE-2010-2568 has been weaponized to remotely execute code on unpatched Windows computers.

The dangerous trend continues, in August 2014 experts from Kaspersky revealed that in the period between November 2013 and June 2014, the Windows Shell vulnerability (CVE-2010-2568) exploited by Stuxnet was detected 50 million times targeting nearly 19 million machines all over the world.

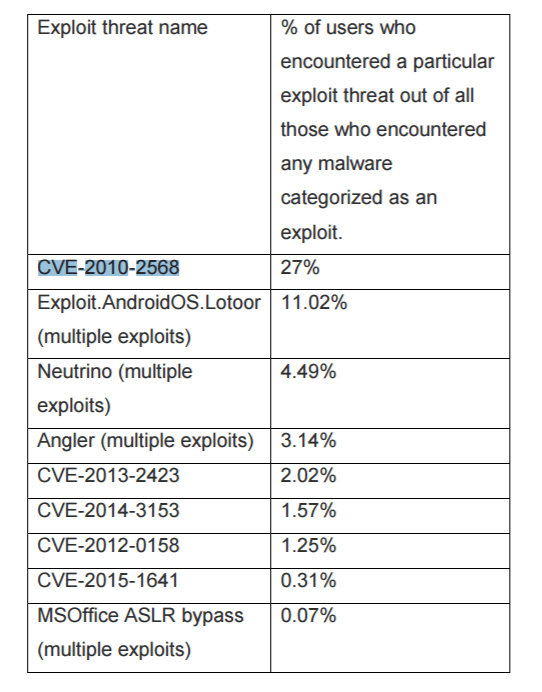
In 2015, and in 2016, roughly one in four Kaspersky users was targeted by an exploit code leveraging the CVE-2010-2568.

“To take just one example, when we looked at our most recent threat statistics we found that exploits to CVE-2010-2568 (used in the notorious Stuxnet campaign) still rank first in terms of the number of users attacked. Almost a quarter of all users who encountered any exploit threat in 2016 were attacked with exploits to this vulnerability.” states a report published by Kaspersky.

Stuxnet attack

Of course, the CVE-2010-2568 vulnerability only affects very old OS, including Windows XP and Windows Server 2008, and unpatched versions of Windows 7.

Attackers most used the Stuxnet exploit code to create malicious codes that can “self-replicate” over a targeted network.

Concluding, the militarization of cyberspace has serious consequences for Internet users, even if the malware was spread many years ago.

I suggest reading of the research published by Kaspersky that provides interesting data on the most exploited vulnerabilities and threat actors leveraging on them.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(Security Affairs – Stuxnet exploits, hacking)

[adrotate banner=”5″]

[adrotate banner=”13″]


