
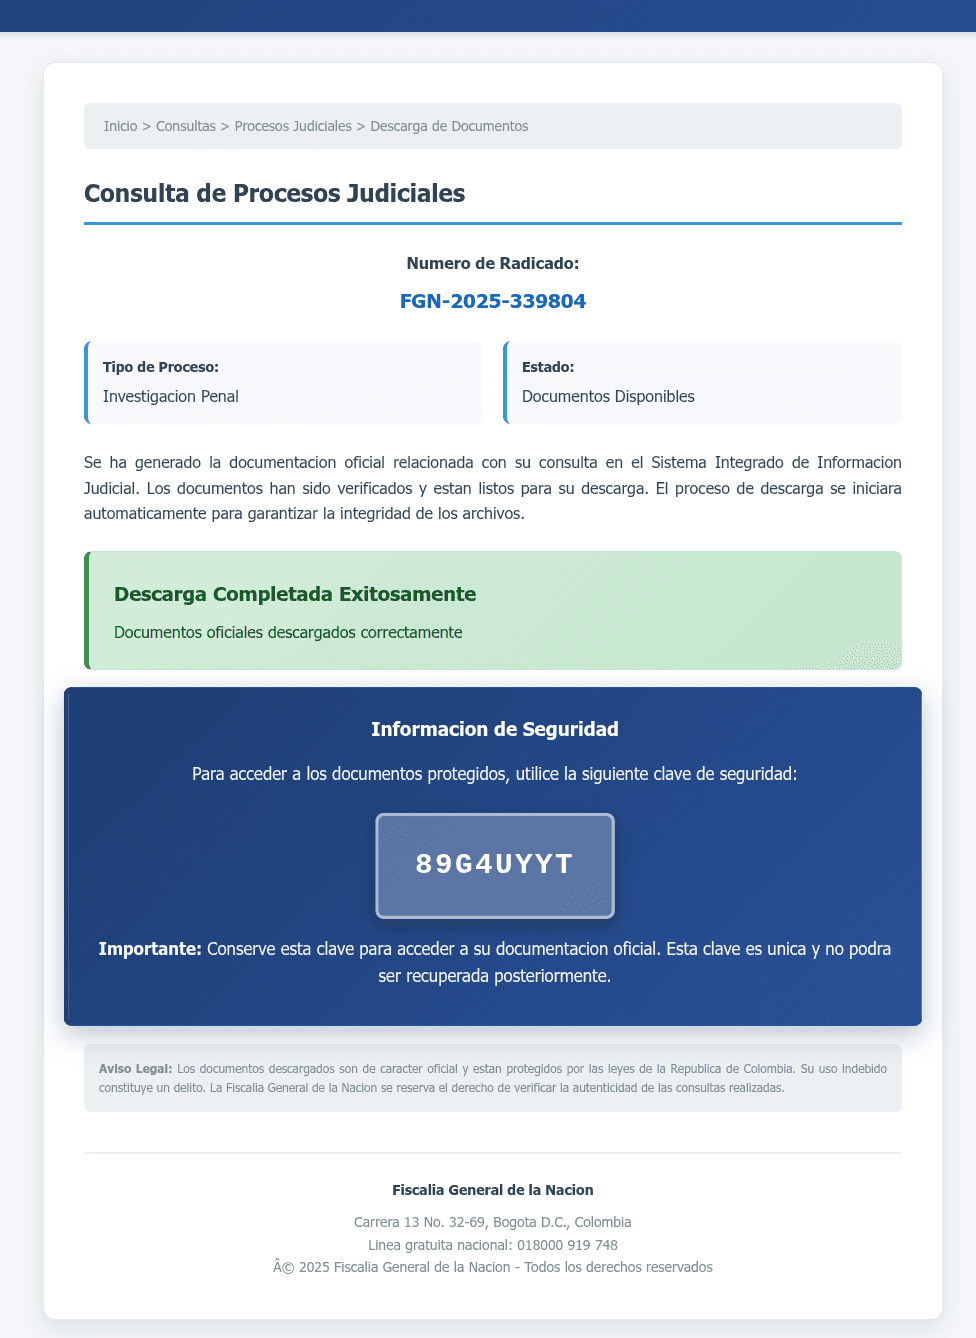
VirusTotal uncovered an undetected malware campaign using SVG files that impersonated the Colombian justice system.
VirusTotal researchers uncovered a phishing campaign using SVG files with hidden JavaScript to deploy fake Fiscalía General de la Nación login pages in Colombia and spread malware.
VirusTotal noticed that, despite being outdated, SWF files are still abused in attacks. In 30 days, VirusTotal logged 47,812 unique SWFs, 466 flagged as malicious. SWFs require unpacking, parsing, and script extraction before analysis. The researchers also highlighted that SVGs remain widely abused by threat actors. VirusTotal saw 140,803 unique SVGs, 1,442 (~1%) flagged as malicious by at least one antivirus engine. Attackers hide malicious JavaScript, redirects, or obfuscation in these XML-based files.
A recent case shows how attackers can slip past antivirus tools but get caught by deeper analysis. One malicious SVG looked harmless and had zero detections on VirusTotal. But Code Insight revealed the truth: it ran hidden JavaScript that built a fake Colombian judicial portal to phish victims. While showing a “file download” progress bar, it secretly decoded and delivered a malicious ZIP file. In short, this single SVG pulled double duty as both a phishing lure and a malware dropper — a perfect example of why traditional AV alone isn’t enough.
A recent case analyzed by VirusTotal shows how attackers can avoid antivirus detection but get caught by deeper analysis. One malicious SVG looked harmless and had zero detections on VirusTotal.
“a malicious SVG file that evaded all antivirus engines, going completely undetected on VirusTotal. On the surface, it looks clean, but a quick look with Code Insight tells a very different story.” reads the report published by VirusTotal.

But Code Insight revealed that it ran hidden JavaScript that built a fake Colombian judicial portal to phish victims. While showing a “file download” progress bar, it secretly decoded and delivered a malicious ZIP file. In short, this single SVG pulled double duty as both a phishing lure and a malware dropper — a perfect example of why traditional AV alone isn’t enough.

The undetected SVG includes two threats, a phishing lure via inline JavaScript and a hidden ZIP malware dropper.
Right after Code Insight added SVG support, one of the first uploads revealed a phishing and malware campaign. A search uncovered 44 malicious SVGs, all invisible to AV but flagged by Code Insight. Attackers used obfuscation, polymorphism, and dummy code, yet left Spanish comments like “POLIFORMISMO_MASIVO_SEGURO.” The experts used a simple YARA rule to catch 523 samples dating back to August 2025. The first payloads were large and heavy, but later versions became lighter and were mostly delivered through email.
“SWF and SVG are very different formats from very different eras, but both can still cause headaches for analysts.” concludes the report. “In the first case, Code Insight helped explain why a SWF file looked suspicious without actually being malicious. In the second, it uncovered malicious behavior in an SVG that had gone completely undetected.”
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, malware)


