
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Marine services provider Swire Pacific Offshore (SPO) hit by Clop ransomware

Marine services provider Swire Pacific Offshore (SPO) has suffered a Clop ransomware attack that resulted in the theft of company data. Clop ransomware hit Marine services provider Swire Pacific Offshore (SPO) and stole company data, but did not affected global operations. “Swire Pacific Offshore (SPO) has discovered that it was the target of a cyberattack […]

Swire Pacific Offshore

Marine services provider Swire Pacific Offshore (SPO) has suffered a Clop ransomware attack that resulted in the theft of company data.

Clop ransomware hit Marine services provider Swire Pacific Offshore (SPO) and stole company data, but did not affected global operations.

“Swire Pacific Offshore (SPO) has discovered that it was the target of a cyberattack which involved unauthorised access to its IT systems. The unauthorised access has resulted in the loss of some confidential proprietary commercial information and has resulted in the loss of some personal data.” reads the media statement published by SPO. “The cyberattack has not materially affected SPO’s global operations.”

The company announced to have taken immediate actions to reinforce existing security measures and to mitigate the potential impact of the security breach.

SPO reported the security breach incident to the relevant authorities, it is also notifying potentially affected parties.

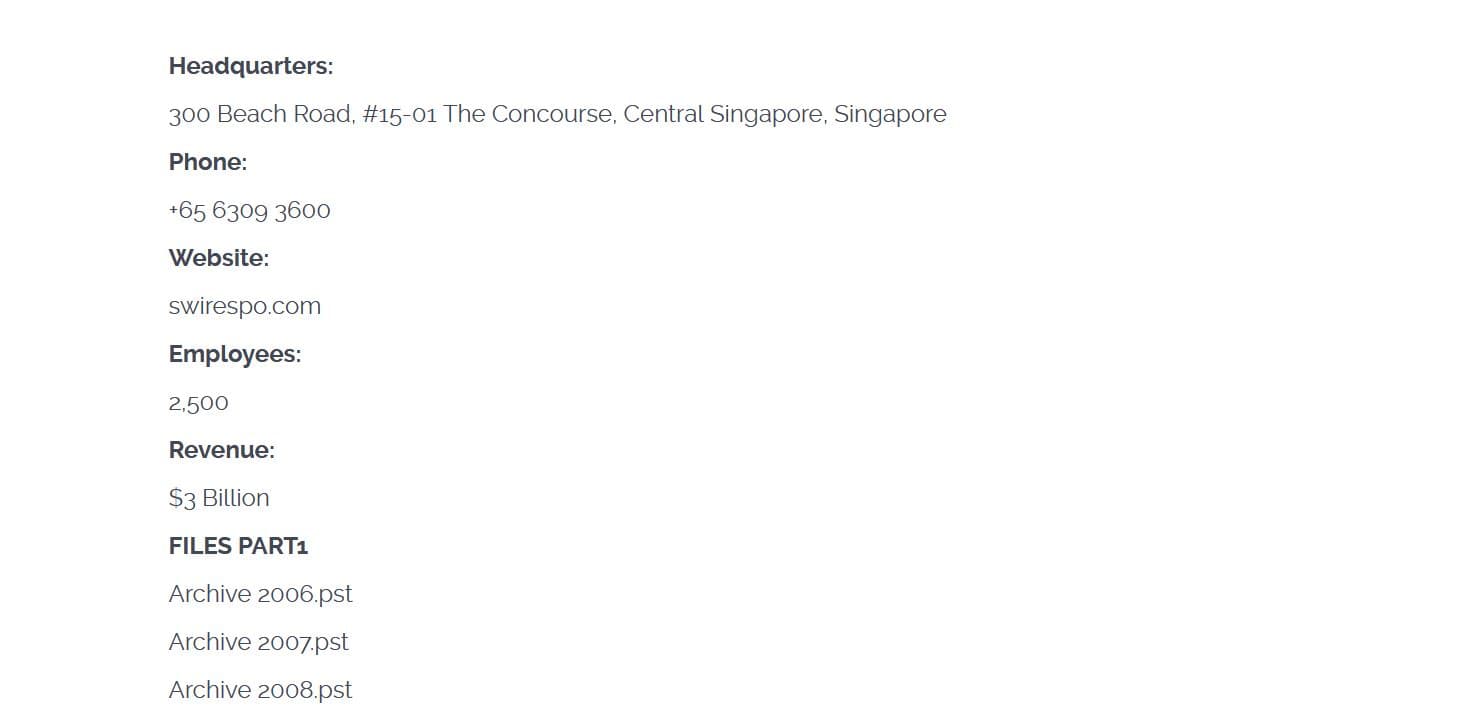
Clop ransomware published on its dark web leak site sample of the stolen data, that includes passports, payroll information, bank account details, email addresses, and more.

Swire Pacific Offshore

In the past, other major organizations in the shipping industry were hit by ransomware attacks, including Maersk, COSCO, International Maritime Organization (IMO), MSC, Pitney Bowes, and CMA CGM.

Follow me on Twitter: @securityaffairs and Facebook

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, SPO)

[adrotate banner=”5″]

[adrotate banner=”13″]


