
Wireless carrier T-Mobile suffered a major outage in the United States, that impacted service at other carriers, due to a “massive” DDoS attack.
Wireless carrier T-Mobile suffered a massive DDoS attack that caused a major outage in the United States that impacted service at other carriers due to a “massive” DDoS attack.
The attack started around noon, millions of T-Mobile were without voice and text service, in some cases customers were not able to access to the Internet.
The company confirmed that data services remained operational throughout the outage.
“Starting just after 12 pm ET and continuing throughout the day, T-Mobile has been experiencing a voice and text issue that has intermittently impacted customers in markets across the U.S. We are recovering from this now but it may still take several more hours before customer calling and texting is fully recovered.” reads the post published by T-Mobile.
T-Mobile President of Technology Neville Ray provided updates on the incident via Twitter.
The incident also affected other carriers including Verizon, and AT&T, their customers have been complaining of errors and outages.
“Verizon’s network is performing well. We’re aware that another carrier is having network issues. Calls to and from that carrier may receive an error message,” said a Verizon spokesperson. “We understand Downdetector is falsely reporting Verizon network issues.”
The other carriers blamed T-Mobile for the outage experienced by its customers.
“This is an IP traffic related issue that has created significant capacity issues in the network core throughout the day,” continues the statement published by T-Mobile.
What has happened?
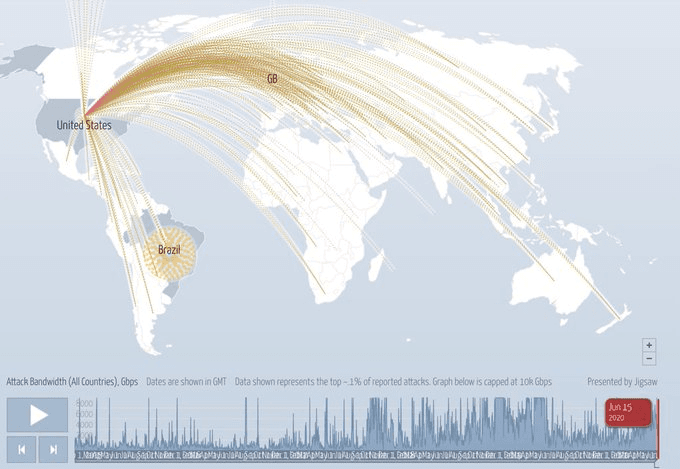
A massive DDoS attack targeted major services in the United States, the attack was confirmed by the Digital Attack Map published by the security firm Arbor Networks.
Matthew Prince, co-founder and CEO of Cloudflare, has a different opinion and pointed out that that the news of a massive DDoS attack is not accurate.
Prince noted that only T-Mobile suffered connectivity problems.
“Except T-Mobile, which is having a bad day almost certainly entirely of their own team’s making. So, please, #hugops. And don’t worry, this is one thing that does not need to get added to the list of craziness that has been 2020,” he added.
The US Federal Communications Commission described the outage as “unacceptable” and launched an investigation into the incident.
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – T-Mobile, DDoS)
[adrotate banner=”5″]
[adrotate banner=”13″]


