
TA558 cybercrime group is behind a malware campaign targeting hospitality, hotel, and travel organizations in Latin America
Researchers from Proofpoint are monitoring a malware campaign conducted by a cybercrime group, tracked as TA558, that is targeting hospitality, hotel, and travel organizations in Latin America.
The group is a small crime threat actor, that has been active since at least April 2018, that employed multiple malware in its attacks, including Loda RAT, Vjw0rm, and Revenge RAT.
The malware a reused to steal personal and financial data of hotel customers, including credit card data, perform lateral movement, and deliver additional payloads.
The group is mainly targeting Portuguese and Spanish speakers, but experts also observed attacks aimed at entities in Western Europe and North America.
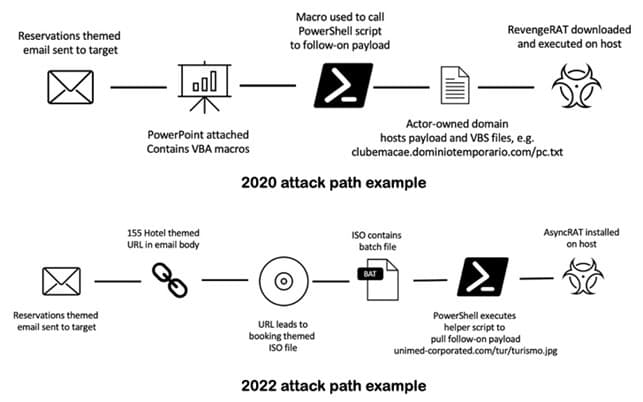
The activity of the gang increased in 2022, the attack chain starts phishing campaigns with reservation-themed lures such as hotel bookings.
“In 2022, Proofpoint observed an increase in activity compared to previous years. Additionally, TA558 shifted tactics and began using URLs and container files to distribute malware, likely in response to Microsoft announcing it would begin blocking VBA macros downloaded from the internet by default.” reads the analysis published by Proofpoint.
The attacks carried out between 2018 and 2021 leveraged emails with weaponized Word documents containing exploits or malicious macros. Upon opening the files, the infection process started.

In recent attacks, the cybercrime group started using malicious URLs, RAR attachments, ISO attachments, and Office documents to deliver the malware. The move is the response to Microsoft’s decision to disable macros by default in Office products
Proofpoint reported that of the 51 campaigns carried out by the threat actors in 2022, 27 of them leveraged URLs pointing to ISO files and ZIP archives, while from 2018 through 2021 only five campaigns leveraged this technique.

Proofpoint reported that since 2018, TA558 has used at least 15 different malware families, is some cases using the same C2 infrastructure. The gang leverage compromised hotel websites to host the malicious payloads.
The threat actor often switches languages in the same week in the attempt to avoid detection and make it attribution of the attacks.
TA558 is also using multiple notable patterns in campaign data, including the use of certain strings, naming conventions and keywords, domains, etc. For example, the attackers often used the term CDT in email and malware attributes, which is related to the CDT Travel organization and related travel reservation lure themes.
“TA558 is an active threat actor targeting hospitality, travel, and related industries since 2018. Activity conducted by this actor could lead to data theft of both corporate and customer data, as well as potential financial losses.” concludes the report.
“Organizations, especially those operating in targeted sectors in Latin America, North America, and Western Europe should be aware of this actor’s tactics, techniques, and procedures.”
Follow me on Twitter: @securityaffairs and Facebook
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, TA558)
[adrotate banner=”5″]
[adrotate banner=”13″]


