
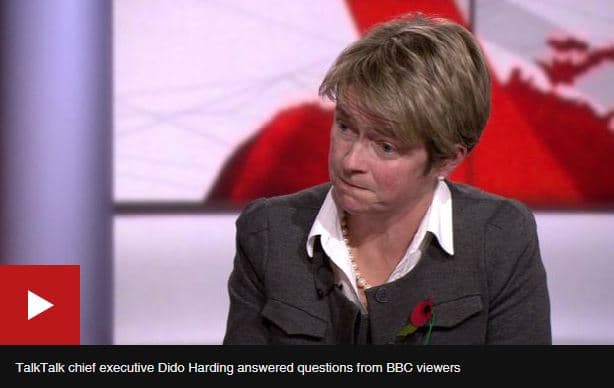
The CEO of TalkTalk confirmed personally receiving a ransom from the alleged attackers, a Russian Islamist group claimed the responsibility of the attack.
TalkTalk Telecom Group plc has publicly disclosed that four million subscribers have been impacted by a “sustained cyberattack” that hit its servers.
The TalkTalk CEO Dido Harding has now confirmed personally receiving a ransom demand following the data breach.
“We have been contacted by, I don’t know whether it is an individual or a group purporting to be the hacker,” Dido Harding said to the BBC. “It is a live criminal investigation. All I can say is I have personally received a contact from someone purporting as I say…to be the hacker looking for money.”
According to the company personal and financial information, including bank details, have been exfiltrated by the threat actors. This means that four million subscriber’s records containing names, home addresses, dates of birth, phone numbers, email addresses, bank account info, and credit card numbers have been compromised by the hackers. The bad news is that TalkTalk also admitted that not all of the data potentially compromised was encrypted.
The CEO in an interview released to the BBC Friday explained that has received an email requesting money to the TalkTalk company.

Harding did not provide further information on the ransom due to an ongoing investigation that is law enforcement is conducting.
Cyber security consultant and former Scotland Yard detective Adrian Culley revealed that a Russian Islamist group claimed the responsibility of the attack. On Friday, the group leaked online a set of data, but it is still not clear yet if the dump includes all the stolen data.
In the note the attackers disclosed online they explained that have used TOR, encrypted chat messages, private key emails and compromised servers to launch the attack remaining anonymous.
Completely unverifiable but here’s the statement from the Russian group claiming to be behind the TalkTalk hack pic.twitter.com/kfbc4lZjns
— Rory Cellan-Jones (@ruskin147) 23 Ottobre 2015
The request for a ransom leads investigators to believe that a bulk of the data has not yet been released, or that the attackers have compromised much more than initially declared 4 million records.
This is the third time in the last 12 months that cyber criminals hit the TalkTalk company, in August the mobile sales site suffered a data breach, meanwhile in February TalkTalk customers were targeted by scammers.
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(Security Affairs – TalkTalk, data breach)
[adrotate banner=”5″]
[adrotate banner=”13″]


