
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

TeamViewer hacked? The company officially denies it

Many TeamViewer users reported that their systems were accessed by hackers via the popular support tool, but the company denies any incident. Many TeamViewer users reported that their systems were accessed by hackers via the popular support tool, but the company denies any security breach. First claims appeared on Reddit, several users reported that unauthorized parties remotely accessed […]

TeamViewer hacked? The company officially denies it

Many TeamViewer users reported that their systems were accessed by hackers via the popular support tool, but the company denies any incident.

Many TeamViewer users reported that their systems were accessed by hackers via the popular support tool, but the company denies any security breach.

First claims appeared on Reddit, several users reported that unauthorized parties remotely accessed their systems through TeamViewer. In same cases, the mysterious attackers attempted to steal money from users’ PayPal accounts in order to purchase items one-commercee platforms, including eBay. This was possible because victims use to configured to remember credentials for commonly used online services.

The mysterious thing is that some users also reported to have been hacked even with a two-factor authentication (2FA) enabled.

Below a couple of messages published on the thread in Reddit.

[–]Eric1084

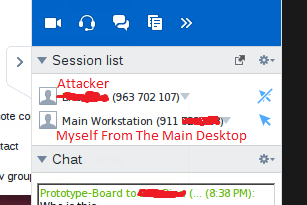
The mouse started moving by itself, attempts to open web browsers. I think that is a definitive proof that someone is trying to gain access to your computer. I took a screenshot of the window just before he disconnected after I asked who it is.

TeamViewer hack

[–]Morblius 9 punti  

I only noticed because at 3:00 am someone transferred $3,000 from my paypal account to theirs. I then saw posts about teamviewer being hacked, so I checked the log file in C:\Program Files (x86)\TeamViewer\TeamViewer11_Logfile.log

Many Internet users speculate that the tool was hacked, another possibility is that hackers have identified a zero-day flaw in the popular application. On the other side, the company downplayed both hypotheses explaining that most likely attackers leveraged leaked passwords that were shared by users on multiple web services.

“As always when we receive alerts about potential security alerts, we look at the issue at hand. This is what we have done in this case: There is no evidence to suggest that TeamViewer has been hacked. Neither do we have any information that would suggest that there is a security hole in TeamViewer. Therefore it it is important to stress there are no TeamViewer hackers, but rather data thieves that will steal information from other sources. It is critical to make sure attention is not diverted from the real issue.” states the official note released by TeamViewer.

I believe that the explanation provided by the company is plausible due to the recent major breaches, including the one suffered by MySpace and LinkedIn

The company also reaffirmed that its systems are totally secure due to the adoption of adequate security measures.

“TeamViewer is safe to use, because TeamViewer has proper security measures in place including end-to-end encryption to prevent man-in-the-middle attacks, anti-brute-force means, and more.” continues TeamViewer,

TeamViewer urges its users to adopt a strong, unique passwords and enable the two-factor authentication on their accounts. Wait a moment, but I told you before that users reported alleged hack even when the 2FA was enabled.

Another mysterious circumstance is a service outage suffered by TeamViewer on Wednesday, an incident that someone linked to an alleged cyber attack.

Stay Tuned …

If you appreciate my effort in spreading cyber security awareness, please vote for Security Affairs as best European Security Blog. Vote SecurityAffairs in every section it is reported. I’m one of the finalists and I want to demonstrate that the Security Affairs community a great reality.

https://www.surveymonkey.com/r/secbloggerwards2016

Thank you

Pierluigi

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – TeamViewer, hacking)

[adrotate banner=”5″]

[adrotate banner=”13″]


