
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Hacking

Experts analyzed attacks against poorly managed Linux SSH servers

Researchers warn of attacks against poorly managed Linux SSH servers that mainly aim at installing DDoS bot and CoinMiner. Researchers at AhnLab Security Emergency Response Center (ASEC) are warning about attacks targeting poorly managed Linux SSH servers, primarily focused on installing DDoS bots and CoinMiners. In the reconnaissance phase, the threat actors perform IP scanning […]

Linux SSH servers

Researchers warn of attacks against poorly managed Linux SSH servers that mainly aim at installing DDoS bot and CoinMiner.

Researchers at AhnLab Security Emergency Response Center (ASEC) are warning about attacks targeting poorly managed Linux SSH servers, primarily focused on installing DDoS bots and CoinMiners.

In the reconnaissance phase, the threat actors perform IP scanning to look for servers with the SSH service, or port 22 activated, then launch a brute force or dictionary attack to obtain the ID and password.

Threat actors can also install malware to scan, perform brute force attacks, and sell breached IP and account credentials on the dark web.

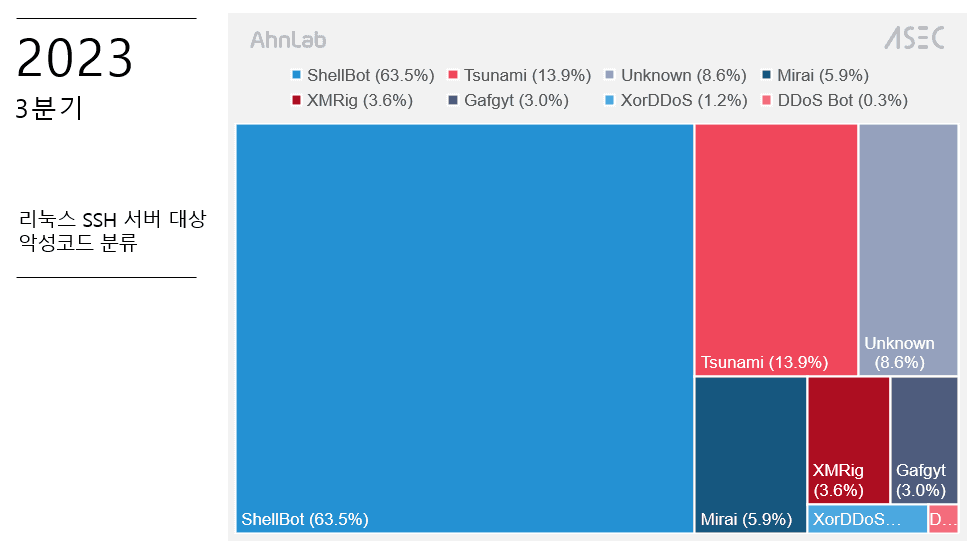
Common malware used in attacks against poorly managed Linux SSH servers include ShellBot [1][2], Tsunami [3], ChinaZ DDoS Bot [4], and XMRig CoinMiner [5]. 

Linux SSH servers

Once successfully logged in, the threat actor first executed the following command to check the total number of CPU cores.

> grep -c ^processor /proc/cpuinfo

“The execution of this command signifies that the threat actor has obtained the account credentials. Afterward, the threat actor logged in again using the same account credentials and downloaded a compressed file.” reads the analysis published by ASEC. “The compressed file contains a port scanner and an SSH dictionary attack tool. Additionally, commands accidentally typed by the threat actor can be seen, such as “cd /ev/network” and “unaem 0a”.”

These researchers believe that the tools employed in the attacks are based on the ones that have been created by the PRG old Team. Each threat actor created its custom version of the tools by modifying them.

Linux SSH servers

The researchers recommend administrators should use strong passwords that are difficult to guess and change them periodically. These measures should protect the Linux SSH servers from brute force attacks and dictionary attacks. The experts also recommend updating to the latest patch to prevent attacks exploiting known vulnerabilities.

“Administrators should also use security programs such as firewalls for servers that are accessible from the outside to restrict access from threat actors. Finally, caution must be practiced by updating V3 to the latest version to block malware infection in advance.” concludes the report.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Linux SSH servers)


