
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Three Mobile cyber data breach, six million customers’ private data at risk

The UK carrier Three Mobile confirmed a major cyber security breach which could have exposed the personal data of millions of customers. Bad news for the UK carrier Three Mobile, cyber criminals have broken into a company database containing customer personal details, details of possibly six million customers exposed. The news was reported by many […]

Three Mobile cyber data breach, six million customers’ private data at risk

The UK carrier Three Mobile confirmed a major cyber security breach which could have exposed the personal data of millions of customers.

Bad news for the UK carrier Three Mobile, cyber criminals have broken into a company database containing customer personal details, details of possibly six million customers exposed.

The news was reported by many media outlets that cited the National Crime Agency (NCA) and the Three Mobile company.

“Three Mobile cyber hack: six million customers’ private information at risk after employee login used to access database ” reports The Telegraph.

According to The Telegraph, Three Mobile admitted that hackers have accessed its customer upgrade database by using an employee login.

“In order to commit this type of upgrade handset fraud, the perpetrators used authorised logins to Three’s upgrade system.” said a company spokesman. 

“This upgrade system does not include any customer payment, card information or bank account information,” the spokesman said.

“Sources familiar with the incident told the Telegraph that the private information of two thirds of the company’s nine million customers could be at risk” continues The Telegraph.

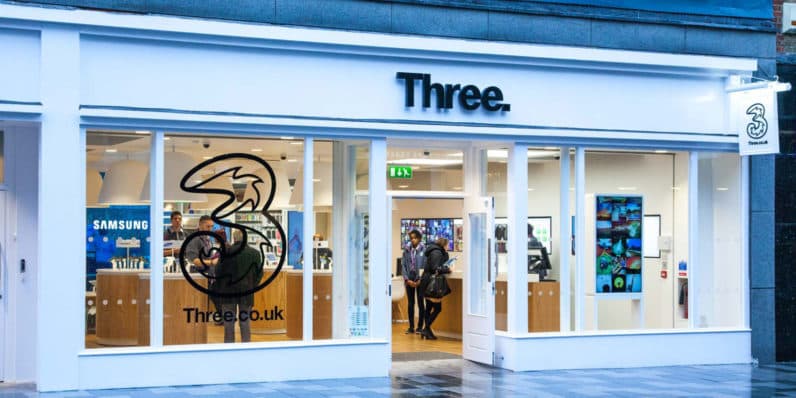
three mobile uk-data-breach

Fortunately, payment data (i.e. Credit card data, bank account data) were not exposed, but the hackers did have access to customer names, addresses, phone numbers, and dates of birth.

Investigators believe the hackers have broken into the Three Mobile database to find customers eligible for handset updates and then place orders on their behalf for the new smartphones that were redirected to them and then resold in a parallel market.

This kind of scam is  increasing, crooks exploit handset upgrades being ordered in order to steal the mobile devices while in transit.

A Three Mobile spokesman confirmed a significant increase in attempted phone fraud over the past four weeks, adding that that increase also includes burglaries of Three retail stores.

The NCA has already arrested three men, two on computer misuse allegations and one on suspicion of attempting to pervert the course of justice.

“The investigation is ongoing and we have taken a number of steps to further strengthen our controls,” added the company spokesman.

The Three Mobile data breach follows the Talk Talk occurred in October 2015 when the details of more than 150,000 customers were stolen including the bank account details of around 15,000.

The company suffered a significant impact, it lost 95,000 subscribers as a result of the attack, which cost it £60million.

[adrotate banner=”9″]

Pierluigi Paganini

(Security Affairs – Three Mobile, data breach)


