
A vulnerability in the video-sharing social networking service TikTok could have allowed hackers to steal users’ private personal information.
Developers at ByteDance, the company that owns TikTok, have fixed a security vulnerability in the popular video-sharing social networking service that could have allowed attackers to steal users’ private personal information.
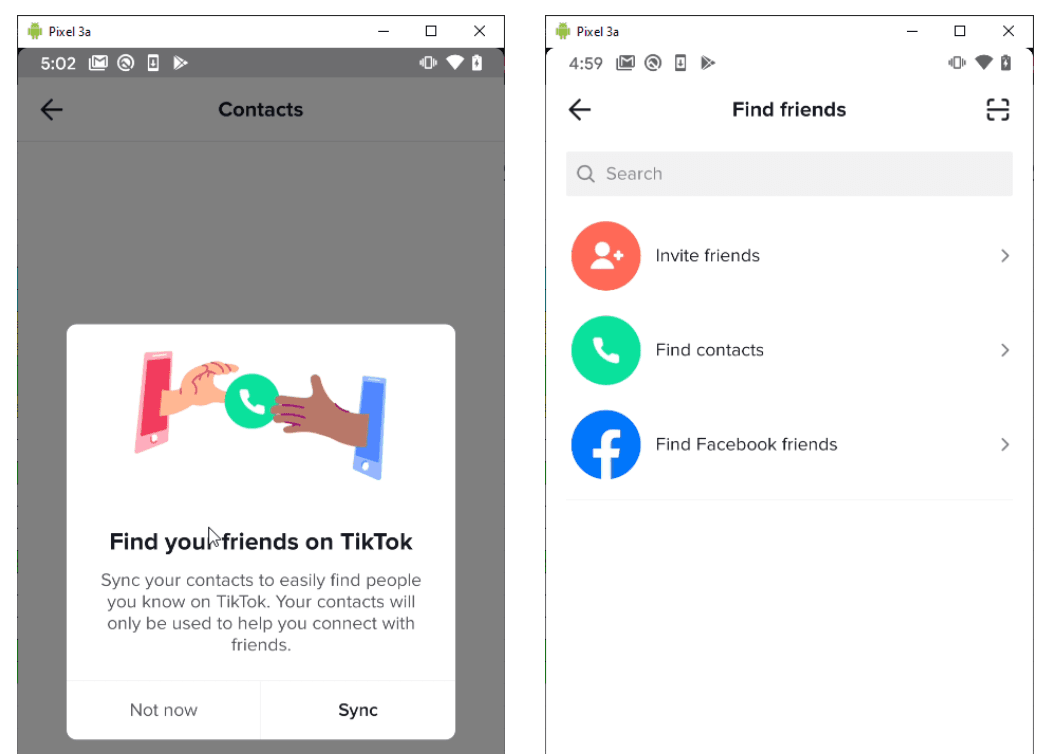
Check Point researchers found a vulnerability in Find Friends feature implemented by TikTok that could have allowed the attackers to bypass the service’s privacy protections allowing them to access users’ private personal data.
Profile data that could be accessible exploiting the vulnerability include a phone number, nickname, profile and avatar pictures, unique user IDs, along with certain profile settings.
“In the recent months, Check Point Research teams discovered a vulnerability within the TikTok mobile application’s friend finder feature. In the vulnerability described in this research an attacker can connect between profile details and phone numbers, while a successful exploitation can enable an attacker to build a database of users and their related phone numbers.” reads the analysis published by CheckPoint researchers. “If exploited, this vulnerability would have only impacted those users who have chosen to associate a phone number with their account (which is not required) or logged in with a phone number.”
Experts focused their activity on all actions related to users’ data and discovered that the mobile app enables contacts syncing. This means that a user can sync his contacts to easily find people he knows on TikTok and this is done by connecting profile details and phone numbers.
The syncing process is composed of 2 requests:
- Upload contacts
- Syncing contacts

The experts provided a step by step exploitation procedure for this privacy issue:
- Step 1 – Creating a List of Devices (Registering Physical Devices)
- Step 2 – Creating a List of Never Expired Session Tokens
- Step 3 – Bypassing TikTok’s HTTP Message Signing
- Step 4 –Chaining It All Together to modify HTTP requests and re-sign them.
The experts were able to automate the process of uploading and syncing contacts on a large scale using a short Frida script that allowed them to build a database of users and their connected phone numbers.
The information exfiltrated by exploiting this privacy flaw could be used by attackers to conduct malicious activities, including scams and phishing campaigns.
Check Point helped ByteDance in identifying and addressing the issue.
If you want to receive the weekly Security Affairs Newsletter for free subscribe here.
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, TikTok)
[adrotate banner=”5″]
[adrotate banner=”13″]


