
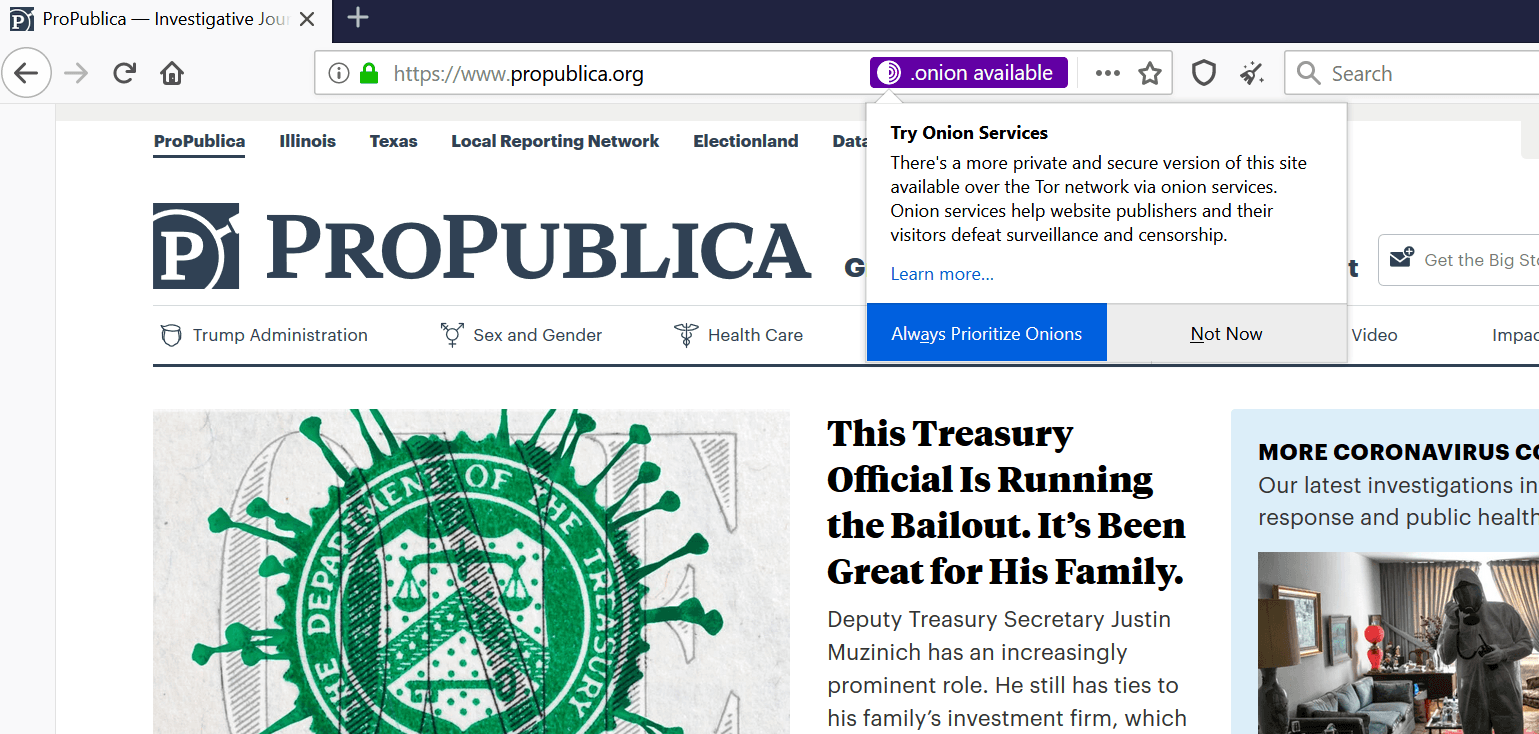
Tor Browser 9.5 includes important security updates to Firefox, users on desktop will be able to opt-in for using onion sites automatically whenever the website makes them available.
Starting with the release of Tor Browser 9.5, new features will make accessing onion addresses easier.
Now, there is also an opt-in mechanism available for websites that want Tor users to know about their onion service that suggest them to upgrade their connection using the .onion address.
This feature will be available to Tor desktop users who have the ‘Onion Location’ option enabled.
“For the first time, Tor Browser users on desktop will be able to opt-in for using onion sites automatically whenever the website makes them available. For years, some websites have invisibly used onion services with alternative services (alt-svc), and this continues to be an excellent choice.” reads the post published by the Tor Project. “Now, there is also an opt-in mechanism available for websites that want their users to know about their onion service that invites them to upgrade their connection via the .onion address.”
Website publishers now can advertise their hidden services to Tor users by adding an HTTP header that can suggest visitors switch to the version of the site that is published using the Onion service.

To promote their onion sites, web site owners need to add an additional ‘Onion-Location’ header that contains the URL to their Tor site.
When a user visits a website that has both an .onion address and Onion Location enabled via Tor Browser, the browser will suggest the onion version of the site.
Tor Browser 9.5 also introduces Onion Authentication to allows admins of Onion services to add an extra layer of security to their website by setting a pair of keys for access control and authentication. Tor Browser users can save keys and manage them via about:preferences#privacy section of the Onion Services Authentication settings.
The latest version of the Tor Browser has improved URL bar security indicators and improved error messages that are displayed when Tor users are not able to reach an onion site.
“In this release, we have improved the way Tor Browser communicates with users about service-, client-, and network-side errors that might happen when they are trying to visit an onion service,” the Tor Project added.
“Tor Browser now displays a simplified diagram of the connection and shows where the error occurred.”
The latest Tor Browser version also addresses several high severity security vulnerabilities, the new release can be downloaded from the Tor Browser download page.
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – Tor, cybersecurity)
[adrotate banner=”5″]
[adrotate banner=”13″]


