
Security Affairs
U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Travelex paid $2.3 Million ransom to restore after a ransomware attack

Travelex reportedly paid a $2.3 million ransom to decrypt its files after being encrypted by the infamous Sodinokibi ransomware. The UK-based currency exchange Travelex currency exchange has been forced offline following a malware attack launched on New Year’s Eve.  The London-based company, which operates more than 1,500 stores globally, suffered the attack on December 31, 2019, […]

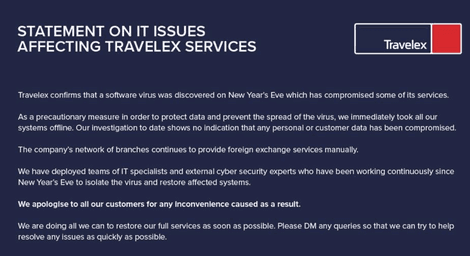
Travelex

Travelex reportedly paid a $2.3 million ransom to decrypt its files after being encrypted by the infamous Sodinokibi ransomware.

The UK-based currency exchange Travelex currency exchange has been forced offline following a malware attack launched on New Year’s Eve. 

The London-based company, which operates more than 1,500 stores globally, suffered the attack on December 31, 2019,

The hackers infected the system at the company with a piece of the Sodinokibi ransomware that shut down operations at 1,500 stores worldwide.

“As part of this attack, the operators behind the Sodinokibi ransomware told BleepingComputer that they had encrypted the company’s entire network, deleted backup files, and copied more than 5GB of personal data. This data allegedly contained “DOB SSN CC and other”.” reported BleepingComputer.

The attackers told BleepingComputer that they demanded a $3 million ransom to decrypt the files and to avoid the publication of the stolen data if the ransom was not paid.

Now a report published by the Wall Street Journal reveals that Travelex paid a 2.3 million ransom to resume the operations after the ransomware attack.

“Less than three months before the owner of the world’s largest chain of money-exchange shops unraveled in an accounting and governance scandal, it faced another challenge: It was at the mercy of hackers. Travelex, known for its ubiquitous foreign-exchange kiosks in airports and tourist sites around the world, was shut down by a computer virus that infiltrated its networks early this year.” reads the report. “It responded by paying the hackers the equivalent of $2.3 million, according to a person familiar with the transaction,”

Travelex resumed operations on January 17th, 2020, at that time, the Sodinokibi gang told BleepingComputer that the company paid the ransomware, but did not specify the exact amount.

The attack on Travelex demonstrates the importance of the prompt notification of a security breach.

Many ransomware gangs like DoppelPaymer and Maze operators are starting threatening victims to publish stolen data before encrypting their systems. In cases like these, it is important that targeted organizations will notify the impacted users immediately after discovered the attack.

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – Travelex, ransomware)

[adrotate banner=”5″]

[adrotate banner=”13″]


