
Trend Micro addressed a DLL hijacking issue in Trend Micro Security actively exploited by a China-linked threat group to deploy malware.
Trend Micro addressed a DLL hijacking flaw in Trend Micro Security that a China-linked threat actor actively exploited to deploy malware.
In early May, SentinelOne researchers observed a China-linked APT group, tracked as Moshen Dragon, targeting the telecommunication sector in Central Asia with ShadowPad and PlugX malware.
Experts observed an overlap between the TTPs of the Moshen Dragon group with the ones of the Chinese Nomad Panda (aka RedFoxtrot).
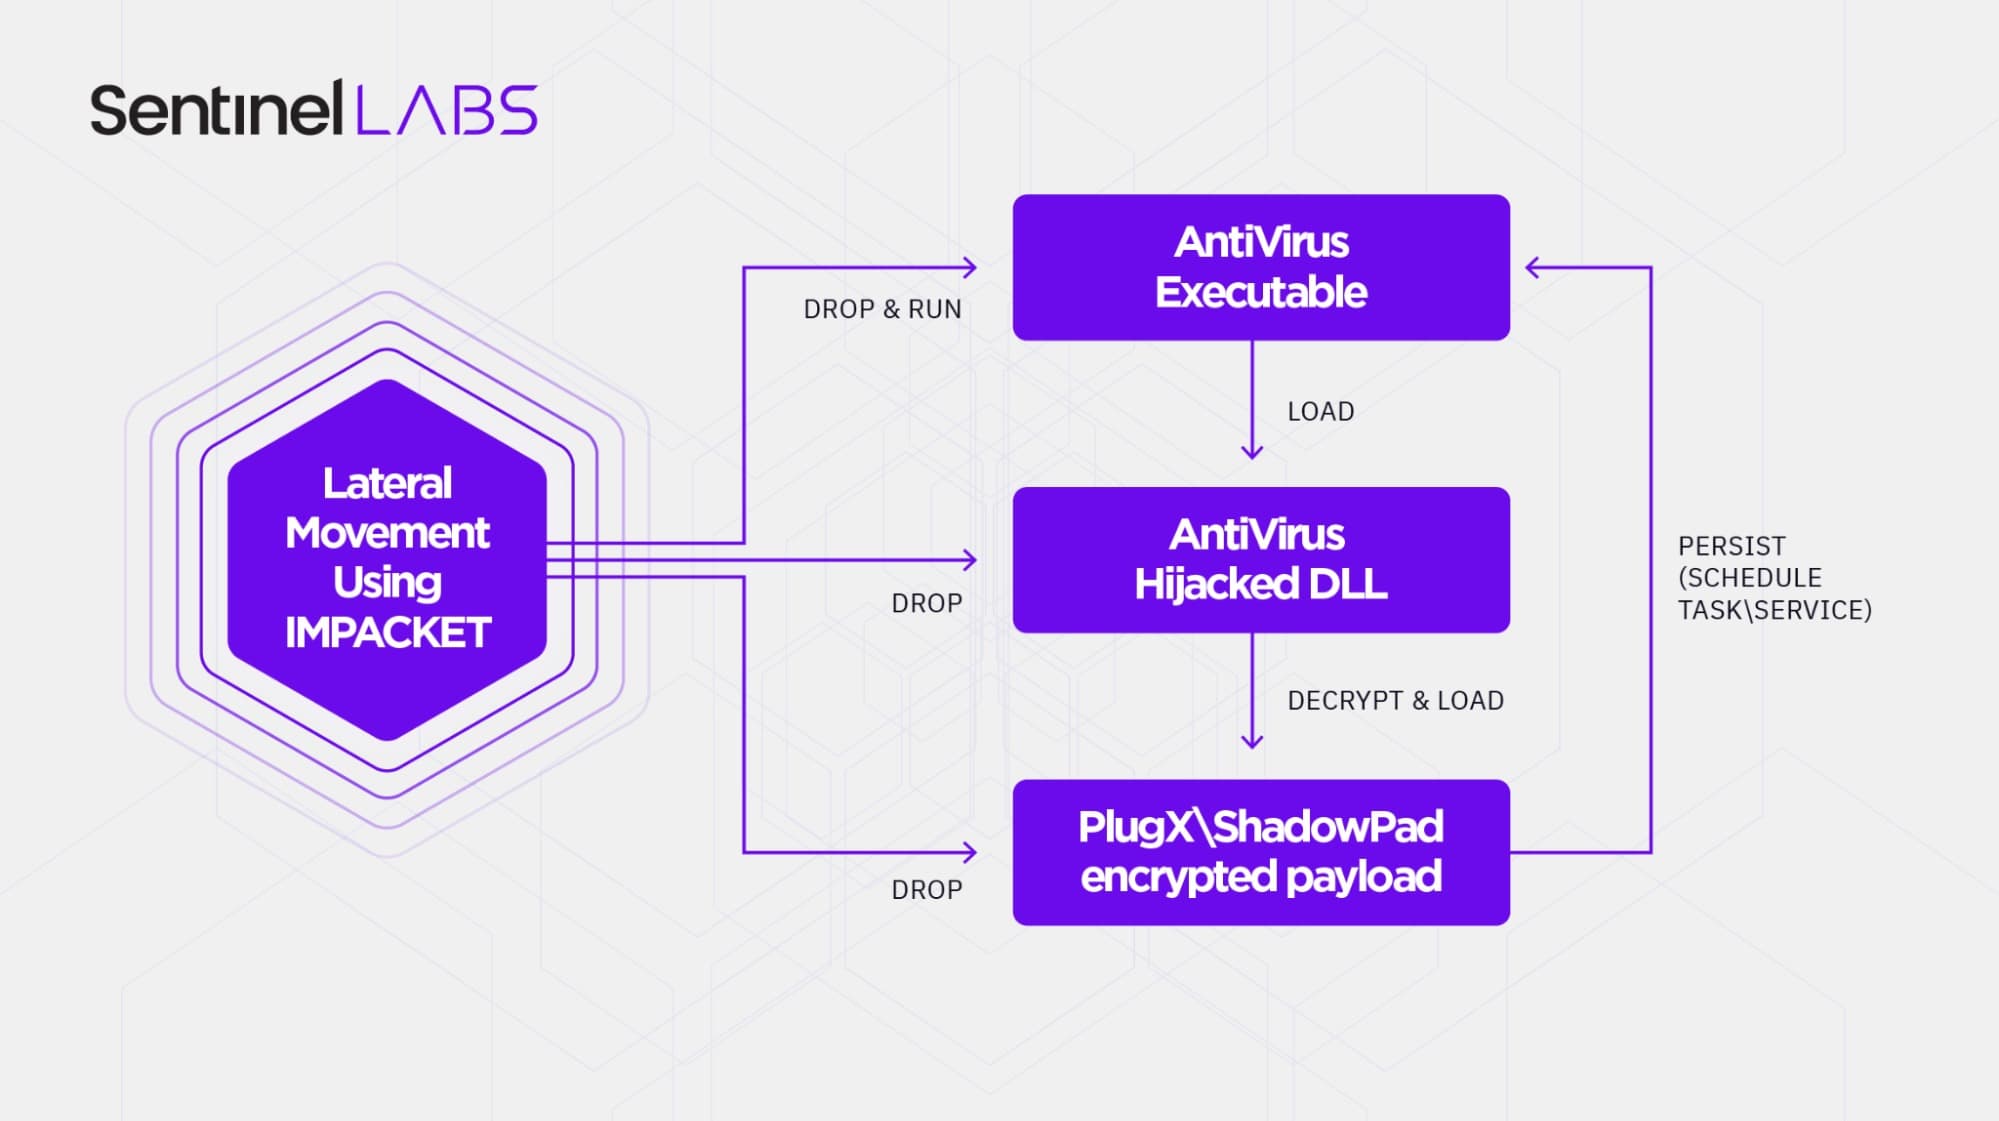
The researchers state that Moshen Dragon deployed five different malware triads to use DLL search order hijacking to sideload ShadowPad and PlugX variants. The cyperespionage group also uses additional tools, including an LSA notification package and the GUNTERS passive backdoor.
SentinelOne experts reported that Moshen Dragon focused on the hijacking of programs belonging to security vendors, including Symantec, TrendMicro, BitDefender, McAfee and Kaspersky.
The hijacked DLL is used to decrypt and load the final payload, stored in a file residing in the same folder.
The Moshen Dragon’s activity analysis led to the discovery of several payloads uploaded to VirusTotal, some of which were the ‘PlugX Talisman variant’.

SentinelOne detailed lateral movements, credential harvesting, and data exfiltration performed by the threat actors by exploiting the flaw in the popular security solutions.
Trend Micro confirmed that it is aware of Moshen Dragon’s activity and its ability to exploit security solutions, including its software, to deploy malware.
“Trend Micro is aware of some research that was published on May 2, 2022, regarding a purported Central-Asian-based threat actor dubbed “Moshen Dragon” that had deployed malware clusters that attempted to hijack various popular security products, including one from Trend Micro.” reads the advisory published by Trend Micro. “For Trend Micro Security (Consumer), a fix was deployed via Trend Micro’s ActiveUpdate (AU) on May 19, 2022, and any user with an active internet connection should receive the update shortly if they have not yet already received it.”
At the time of this writing, it is not clear if other security vendors impacted by the issue have addressed the issue affecting their products.
Security Affairs is one of the finalists for the best European Cybersecurity Blogger Awards 2022 – VOTE FOR YOUR WINNERS. I ask you to vote for me again (even if you have already done it), because this vote is for the final.
Please vote for Security Affairs and Pierluigi Paganini in every category that includes them (e.g. sections “The Underdogs – Best Personal (non-commercial) Security Blog” and “The Tech Whizz – Best Technical Blog”)
To nominate, please visit:
https://docs.google.com/forms/d/e/1FAIpQLSdNDzjvToMSq36YkIHQWwhma90SR0E9rLndflZ3Cu_gVI2Axw/viewform
Follow me on Twitter: @securityaffairs and Facebook
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, Moshen Dragon)
[adrotate banner=”5″]
[adrotate banner=”13″]


