
A hacker with Google Project Zero research team, publicly disclosed critical vulnerabilities in the TrendMicro Antivirus.
Tavis Ormandy, a researcher with Google’s Project Zero vulnerability research team, publicly disclosed critical vulnerabilities in TrendMicro Antivirus that could be exploited to execute malicious code on the targeted system.
Ormandy took only about 30 seconds to find the first code-execution vulnerability affecting the TrendMicro antivirus program.

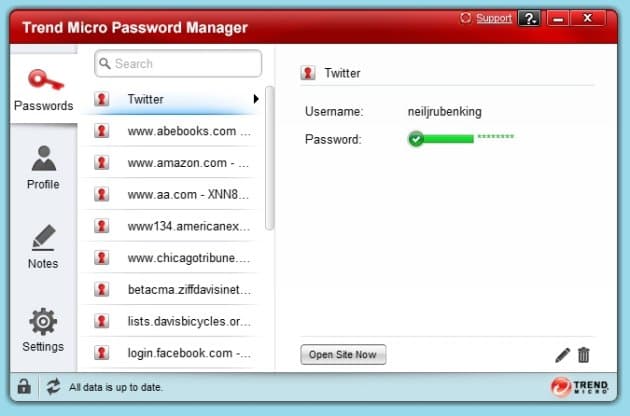
An attacker could exploit the security flaws to access contents of a password manager built into the TrendMicro security solution. The attackers can view hashed passwords and the plaintext Internet domains they are used for.
“[The password manager] product is primarily written in JavaScript with node.js, and opens multiple HTTP RPC ports for handling API requests. It took about 30 seconds to spot one that permits arbitrary command execution, openUrlInDefaultBrowser, which eventually maps to ShellExecute(). This means any website can launch arbitrary commands, like this:”
x = new XMLHttpRequest()
x.open("GET", "https://localhost:49155/api/openUrlInDefaultBrowser?url=c:/windows/system32/calc.exe true); try { x.send(); } catch (e) {};
The expert highlighted that an attacker can exploit the flaws even if users never launch the password manager.
“I don’t even know what to say—how could you enable this thing *by default* on all your customer machines without getting an audit from a competent security consultant?” explained Ormandy “You need to come up with a plan for fixing this right now. Frankly, it also looks like you’re exposing all the stored passwords to the internet, but let’s worry about that screw up after you get the remote code execution under control.”
The Google expert criticized TrendMicro for approaching in the wrong way the threat and fix the issues. Ormandy highlighted the serious risks for end-users inviting the company to disable the feature.
“So this means, anyone on the internet can steal all of your passwords completely silently, as well as execute arbitrary code with zero user interaction. I really hope the gravity of this is clear to you, because I’m astonished about this.” Ormandy added. “In my opinion, you should temporarily disable this feature for users and apologise for the temporary disruption, then hire an external consultancy to audit the code. In my experience dealing with security vendors, users are quite forgiving of mistakes if vendors act quickly to protect them once informed of a problem, I think the worst thing you can do is leave users exposed while you clean this thing up. The choice is yours, of course.”
Despite TrendMicro released an emergency fix, according to Ormandy the password manager still represents an open door for hackers.
“I’m still concerned that this component exposes nearly 70 API’s (!!!!) to the internet, most of which sound pretty scary. I tell them I’m not going to through them, but that they need to hire a professional security consultant to audit it urgently.“
Recently other security software have been found vulnerable to cyber attacks, including FireEye, McAfee, Kaspersky and AVG.
(Security Affairs – Antivirus, TrendMicro)


