
A Russian man accused of being a member of the infamous TrickBot gang was arrested while trying to leave South Korea
A Russian man accused of being a member of the TrickBot gang was arrested last week at the Seoul international airport.
The man has remained stuck in the Asian country since February 2020 due to the COVID-19 lockdown imposed by the local government and the cancelation of international travel.
According to The Record, which first reported the news, after the travel restrictions were lifted, the suspect has an ugly surprise, his passport had expired. Mr. A, this is the pseudonym used to identify the individual, was forced to live in a Seoul waiting for the replacement of his passport from the local Russian embassy.
The Trickbot botnet continues to evolve despite the operations conducted by law enforcement aimed at dismantling it. The authors recently implemented an update for the VNC module used for remote control over infected systems.
In October, Microsoft’s Defender team, FS-ISAC, ESET, Lumen’s Black Lotus Labs, NTT, and Broadcom’s cyber-security division Symantec joined the forces and announced a coordinated effort to take down the command and control infrastructure of the infamous TrickBot botnet.
Even if Microsoft and its partners have brought down the TrickBot infrastructure, its operators attempted to resume the operations by setting up new command and control (C&C) servers online.

Following the takedown, the operators behind the TrickBot malware have implemented several improvements to make it more resilient.
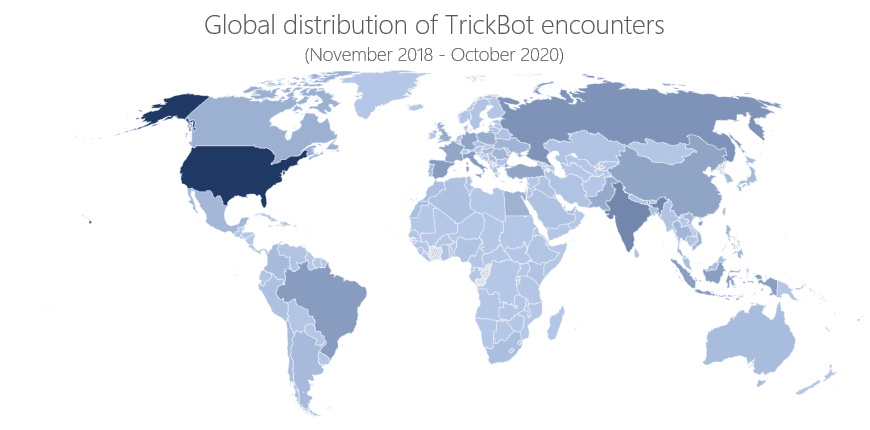
TrickBot is a popular banking Trojan that has been around since October 2016, its authors have continuously upgraded it by implementing new features. Operators continue to offer the botnet through a multi-purpose malware-as-a-service (MaaS) model. Threat actors leverage the botnet to distribute a broad range of malware including info-stealer and ransomware such as Conti and Ryuk. To date, the Trickbot botnet has already infected more than a million computers.
The Seoul High Court Criminal Division 20 (Chief Judge Jeong Seon-jae Baek Suk-jong Lee Jun-hyun) charged Mr. A for being a developer for the TrickBot gang who worked on a web browser-related component. The man was recruited by the criminal organization in 2016.
Prosecutors plan to to extradite Mr. A to the United States, but his attorney is opposed to the decision.
“If you send him to the United States, it will be very difficult to exercise your right of defense and there is a high possibility that you will be subjected to excessive punishment.” Mr. A’s attorney said,
Follow me on Twitter: @securityaffairs and Facebook
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, TrickBot )
[adrotate banner=”5″]
[adrotate banner=”13″]


