
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Tridium Niagara framework affected by 2 flaws in BlackBerry QNX OS

Tridium’s Niagara product is affected by two vulnerabilities in BlackBerry’s QNX operating system for embedded devices. The U.S. Department of Homeland Security’s Cybersecurity and Infrastructure Security Agency (CISA) is warning of two vulnerabilities in Tridium’s Niagara product that reside in the BlackBerry’s QNX operating system for embedded devices. The flaws could be exploited by a […]

Tridium Niagara product

Tridium’s Niagara product is affected by two vulnerabilities in BlackBerry’s QNX operating system for embedded devices.

The U.S. Department of Homeland Security’s Cybersecurity and Infrastructure Security Agency (CISA) is warning of two vulnerabilities in Tridium’s Niagara product that reside in the BlackBerry’s QNX operating system for embedded devices.

The flaws could be exploited by a local user to escalate their privileges.

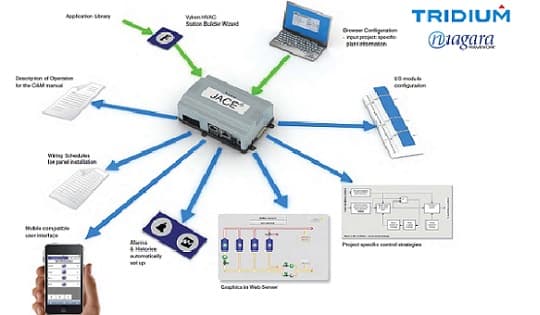
The Niagara Framework is a universal software infrastructure developed by Tridium that allows building controls integrators, HVAC and mechanical contractors to build custom, web-enabled applications for accessing, automating and controlling smart devices real-time via local network or over the Internet.

Tridium Niagara product

The Niagara framework is widely adopted, especially in the commercial facilities, government facilities, critical manufacturing and IT sectors.

The security flaws impact Niagara AX 3.8u4, 4.4u3 and 4.7u1.

The most severe vulnerability, tracked as CVE-2019-8998, is an information disclosure flaw related to the procfs service that can be exploited by a local attacker for privilege escalation.

The flaw was discovered by Johannes Eger and Fabian Ullrich of the Secure Mobile Networking Lab at TU Darmstadt in Germany and received a CVSS score of 7.8.

“This advisory addresses an information disclosure vulnerability leading to a potential local escalation of privilege in the default configuration of the procfs service (the /proc filesystem) on affected versions of the BlackBerry QNX Software Development Platform (QNX SDP) that could potentially allow a successful attacker to gain unauthorized access to a chosen process address space.” reads the advisory.

BlackBerry QNX confirmed that it is not aware of attacks exploiting the flaw in the wild.

The second vulnerability, tracked as CVE-2019-13528, is an improper authorization issue, it could allow a specific utility to gain read access to privileged files.

“A specific utility may allow an attacker to gain read access to privileged files in the Niagara AX 3.8u4 (JACE 3e, JACE 6e, JACE 7, JACE-8000), Niagara 4.4u3 (JACE 3e, JACE 6e, JACE 7, JACE-8000), and Niagara 4.7u1 (JACE-8000, Edge 10).” reads the advisory.

This flaw was reported by Francisco Tacliad and it received a CVSS score of 4.4.

Tridium has released updates that address these vulnerabilities and recommends users update to the versions identified below:

  • Niagara AX 3.8u4: 
    • OS Dist: 2.7.402.2
    • NRE Config Dist: 3.8.401.1
  • Niagara 4.4u3:
    • OS Dist: 4.4.73.38.1 NRE Config
    • Dist: 4.4.94.14.1
  • Niagara 4.7u1:
    • OS Dist: (JACE 8000) 4.7.109.16.1
    • OS Dist (Edge 10): 4.7.109.18.1
    • NRE Config Dist: 4.7.110.32.1
[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – Tridium, IoT)

[adrotate banner=”5″]

[adrotate banner=”13″]


