
Security researchers from Bitdefender have spotted a new Android spyware framework dubbed Triout that could be used to create malware with extensive surveillance capabilities.
Bitdefender researchers have identified a new spyware framework can be used to spy into Android applications, it is tracked as Triout and first appeared in the wild on May 15.
The researcher revealed that the command and control (C&C) server has been running since May 2018 and at the time of the report it was still up and running.
Triout was first submitted on May 15 to VirusTotal, although the first sample was uploaded from Russia, most of the other ones came from Israel.
The malware was likely spread through third-party marketplaces or domains controlled by the attackers that host the malicious code.
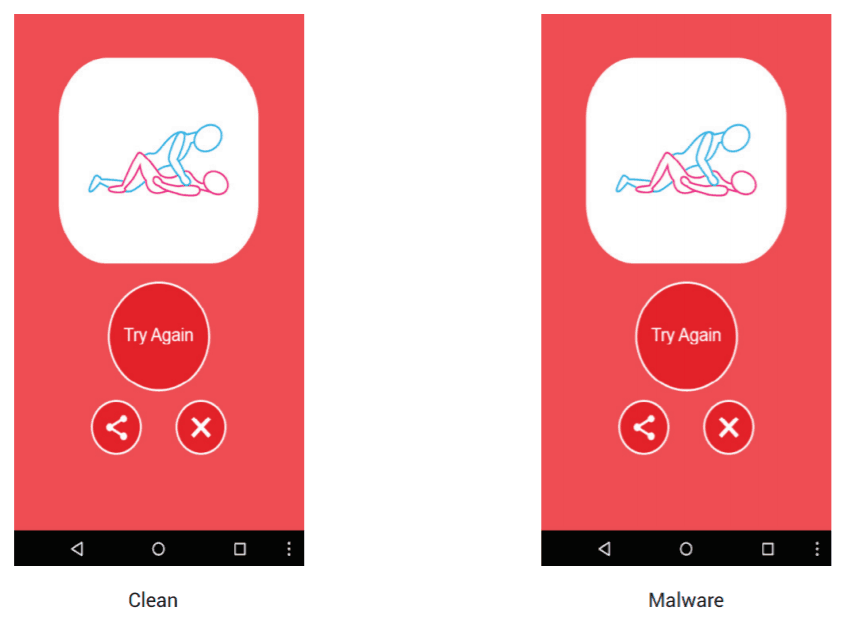
“Discovered by Bitdefender’s machine learning algorithms on 20.07.2018, the sample’s first appearance seems to be 15.05.2018, when it was uploaded to VirusTotal. The application seems to be a repackaged version of “com.xapps.SexGameForAdults” (MD5: 51df2597faa3fce38a4c5ae024f97b1c) and the tainted .apk fi le is named 208822308.apk.” reads the report published by Bitdefender.
“The original app seems to have been available in Google Play in 2016, but it has since been removed. While it’s unclear how the tainted sample is being disseminated, third-party marketplaces or some other attacker-controlled domains are likely used to host the sample.”
Bitdefender pointed out that the analyzed sample was unobfuscated a circumstance that leads the experts into believing the framework may be a work-in-progress.
“This could suggest the framework may be a work-in-progress, with developers testing features and compatibility with devices,” continues the report.
The Triout spyware was discovered analyzing a tainted application that maintained all the original features. The sample analyzed by Bitdefender was a repackaged version of an adult application that was listed in Google Play in 2016, but was since removed. This means that attackers might have made it available through third-party channels.

Triout implements extensive surveillance capabilities, including:
- Records every phone call (literally the conversation as a media fi le), then sends it together with the caller id to the C&C (incall3.php and outcall3.php)
- logs every incoming SMS message (SMS body and SMS sender) to C&C (script3.php)
- Has capability to hide self
- Can send all call logs (“content://call_log/calls”, info: callname, callnum, calldate, calltype, callduration) to C&C (calllog. php)
- Whenever the user snaps a picture, either with the front or rear camera, it gets sent to the C&C (uppc.php, fi npic.php or reqpic.php)
- Can send GPS coordinates to C&C (gps3.php)
Technical details are included in the report published by Bitdefender.
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(Security Affairs – Triout spyware, Android malware)
[adrotate banner=”5″]
[adrotate banner=”13″]


