
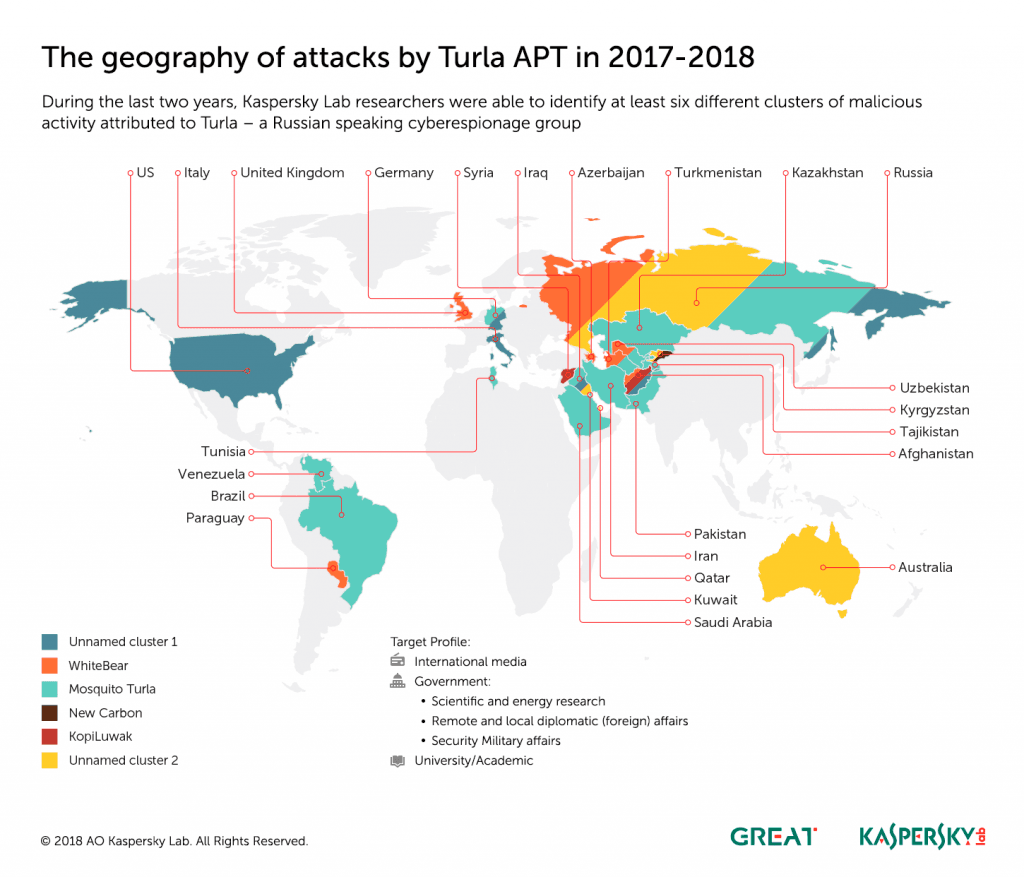
Researchers from Kaspersky Lab collected evidence that demonstrates overlaps between the activity of Russian APT groups Turla and Sofacy.
In March, during the Kaspersky Security Analyst Summit held in Cancun, Kurt Baumgartner, Kaspersky principal security researcher, revealed the activity associated with Sofacy APT group appears to overlap with campaigns conducted by other cyber espionage groups.
Baumgartner explained that the Sofacy’s Zebrocy malware was found on machines in Europe and Asia that were also infected with the Mosquito backdoor associated with the Russia-linked Turla APT.

The researchers discovered that the delivery of the Turla’s KopiLuwak malware is leverage a code identical to that previously observed in campaign distributing the Zebrocy tool.
The delivery vector used in the recent spear-phishing campaigns conducted by Turla uses Windows shortcut (.LNK) that contained PowerShell code almost identical to that used in Zebrocy attacks.
In mid-2018 a very small number of systems in Syria and Afghanistan being targeted with this new delivery vector.
KopiLuwak was first spotted in 2016 while the APT was delivering it to at least one victim leveraging a document containing an official letter from the Qatar Embassy in Cyprus to the Ministry of Foreign Affairs in Cyprus.
The KopiLuwak uses multiple JavaScript layers to avoid detection, the malicious code gain persistence on the targeted machine by creating a registry key. Once infected a system, the malicious code is able executes a series of commands to collect information and exfiltrate data. Stolen data are temporarily stored in a file that is deleted after it’s encrypted and stored in memory.
The KopiLuwak JavaScript malware is controlled through a collection of compromised websites, the IP address of those websites are hardcoded into the malicious code.
The C&C can send arbitrary commands to the infected system using Wscript.shell.run().
Since 2016, the KopiLuwak JavaScript backdoor evolved and Kaspersky shared technical details on its changes.
Experts also detailed the evolution of the Turla’s Carbon backdoor and in the Meterpreter and Mosquito malware delivery techniques.
Experts believe Turla will continue to improve its arsenal, they believe the nation-state actor could target organizations in Central Asia and related remote locations.
“It’s very interesting to see ongoing targeting overlap, or the lack of overlap, with other APT activity. Noting that Turla was absent from the milestone DNC hack event where Sofacy and CozyDuke were both present, but Turla was quietly active around the globe on other projects, provides some insight as to ongoing motivations and ambitions of this group,” Kaspersky concludes.
“From the targeting perspective, we see closer ties between the KopiLuwak and WhiteBear activity, and closer alignments between Mosquito and Carbon activity.”
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(Security Affairs – Turla, Sofacy)
[adrotate banner=”5″]
[adrotate banner=”13″]


