
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Expert warns of Turtle macOS ransomware

The popular cybersecurity researcher Patrick Wardle dissected the new macOS ransomware Turtle used to target Apple devices. The popular cyber security researcher Patrick Wardle published a detailed analysis of the new macOS ransomware Turtle. Wardle pointed out that since Turtle was uploaded on Virus Total, it was labeled as malicious by 24 anti-malware solutions, suggesting […]

TurtleRansom

The popular cybersecurity researcher Patrick Wardle dissected the new macOS ransomware Turtle used to target Apple devices.

The popular cyber security researcher Patrick Wardle published a detailed analysis of the new macOS ransomware Turtle.

Wardle pointed out that since Turtle was uploaded on Virus Total, it was labeled as malicious by 24 anti-malware solutions, suggesting it is not a sophisticated threat. However, the malicious code was generally detected as “Other:Malware-gen”, “Trojan.Generic”, or “Possible Threat”. In some cases, the anti-virus solution flagged the binary as Windows malware (“Win32.Troj.Undef”).

The experts speculate the malware was first developed for Windows, then ported to macOS.

Only one AV engine detects the malicious code as “Ransom.Turtle” due to the internal name of the malware.

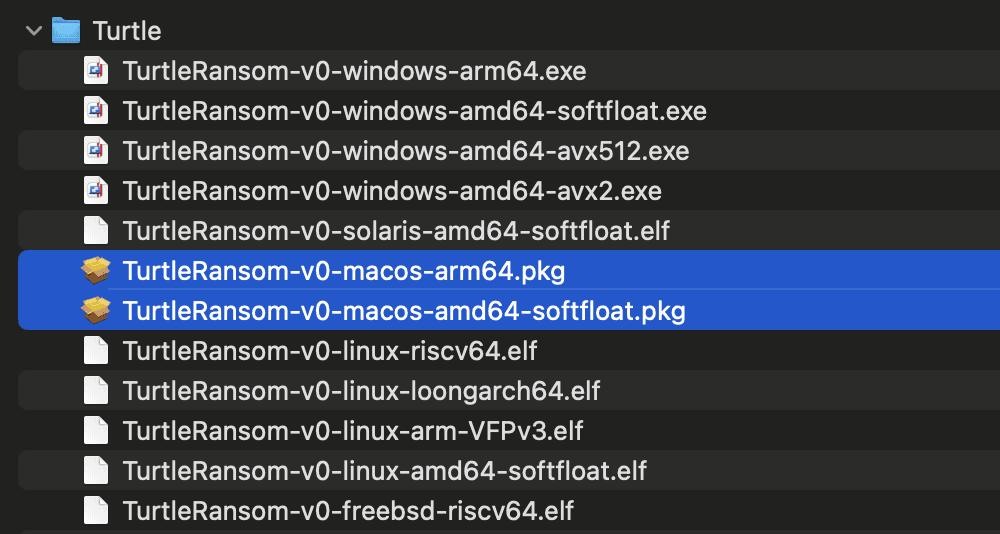
“If we download the archive and unzip it, we find it contains files (prefixed with “TurtleRansom”) that appear to be compiled for common platforms, including, Windows, Linux, and yes, macOS” reads the analysis published by Wardle.

The malicious code is only signed adhoc and Gatekeeper should block it, explains Wardle. The binary also lacks of obfuscation.

The Turtle ransomware reads files into memory, encrypt them with AES (in CTR mode), rename the files, then overwrites the original contents of the files with the encrypted data. The malware adds the extension “TURTLERANSv0” to the filenames of encrypted files.

The malware is not sophisticated, however the discovery of a macOS version for the Turtle ransomware suggests it is becoming popular in the cybercrime underground.

Wardle discovered various strings in Chinese, some of these strings are related to ransomware operations, such as “加密文件” which translate to “Encrypt files”. However the presence of these strings is not enough to attribute the malware to a specific threat actor.

“Today we dove into a new ransomware sample, internally dubbed “Turtle”. And while in its current state it does not post much of a threat to macOS users, it yet again, shows that ransomware authors continue to set their sites on macOS.” concludes the analysis.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, TurtleRansom)


