
Threat actor leaked data of 5.4 million Twitter users that were obtained by exploiting a now patched flaw in the popular platform.
A threat actor has leaked data of 5.4 million Twitter accounts that were obtained by exploiting a now-fixed vulnerability in the popular social media platform.
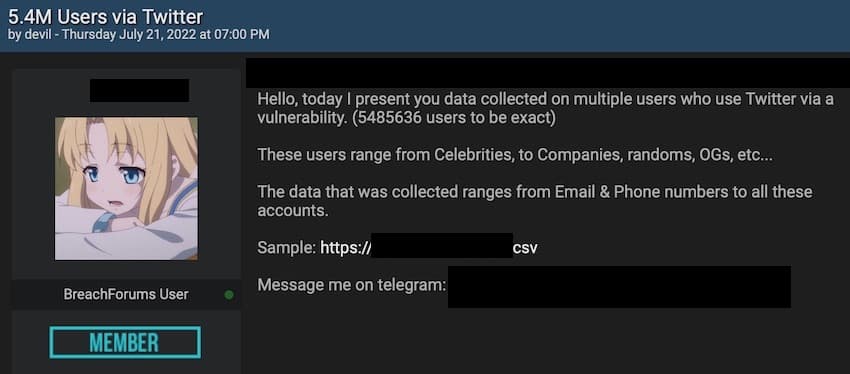
The threat actor is now offering for sale the stolen data on a the popular hacking forum Breached Forums. In January, a report published on Hacker claimed the discovery of a vulnerability that can be exploited by an attacker to find a Twitter account by the associated phone number/email, even if the user has opted to prevent this in the privacy options.
“The vulnerability allows any party without any authentication to obtain a twitter ID(which is almost equal to getting the username of an account) of any user by submitting a phone number/email even though the user has prohibitted this action in the privacy settings. The bug exists due to the proccess of authorization used in the Android Client of Twitter, specifically in the procces of checking the duplication of a Twitter account.” ” reads the description in the report submitted by zhirinovskiy via bug bounty platform HackerOne. “This is a serious threat, as people can not only find users who have restricted the ability to be found by email/phone number, but any attacker with a basic knowledge of scripting/coding can enumerate a big chunk of the Twitter user base unavaliable to enumeration prior (create a database with phone/email to username connections). Such bases can be sold to malicious parties for advertising purposes, or for the purposes of tageting celebrities in different malicious activities”
Twitter confirmed the existence of this vulnerability and awarded zhirinovskiy with a $5,040 bounty.
The website Restore Privacy first discovered the advertisement for the huge trove of data on Breached Forums.
Hacker lists database of 5.4 million Twitter users for sale
The seller claims that the database contains data (i.e. emails, phone numbers) of users ranging from celebrities to companies. The seller also shared a sample of data in the form of a csv file.

“A few hours after the post was made, the owner of Breach Forums verified the authenticity of the leak and also pointed out that it was extracted via the vulnerability from the HackerOne report above.” reads the post published by RestorePrivacy.
“We downloaded the sample database for verification and analysis. It includes people from around the world, with public profile information as well as the Twitter user’s email or phone number used with the account.”
The seller told RestorePrivacy that he is asking for at least $30,000 for the entire database.
Update: 24 July, 2022
The seller has removed the adv
Follow me on Twitter: @securityaffairs and Facebook
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, Twitter)
[adrotate banner=”5″]
[adrotate banner=”13″]


