
Security Affairs
CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|FBI Blames North Korea for $6 Billion Binance Crypto Theft|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|FBI Blames North Korea for $6 Billion Binance Crypto Theft|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Tycoon2FA phishing kit rolled out significant updates

The operators of the Phishing-as-a-Service (PhaaS) platform Tycoon2FA have rolled out significant updates to enhance its evasion capabilities. Tycoon2FA, a phishing kit discovered in 2023 by cybersecurity firm Sekoia, was recently updated to improve its evasion capabilities. The phishing kit now uses advanced evasion tactics such as a custom CAPTCHA via HTML5 canvas, invisible Unicode […]

Tycoon2FA PhaaS

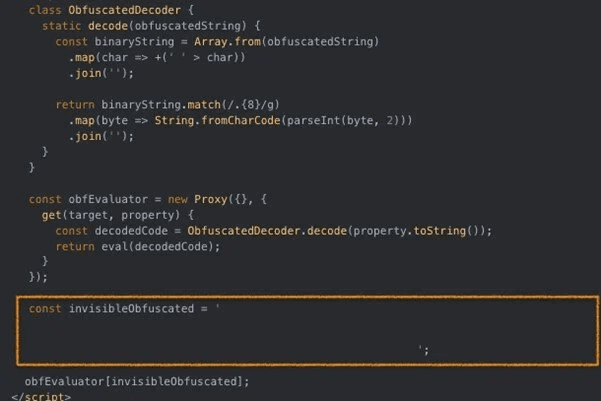
Tycoon 2FA using invisible Unicode characters to encode JavaScript code. The obfuscation is actually quite simple but clever.

The operators of the Phishing-as-a-Service (PhaaS) platform Tycoon2FA have rolled out significant updates to enhance its evasion capabilities.

Tycoon2FA, a phishing kit discovered in 2023 by cybersecurity firm Sekoia, was recently updated to improve its evasion capabilities.

The phishing kit now uses advanced evasion tactics such as a custom CAPTCHA via HTML5 canvas, invisible Unicode in obfuscated JavaScript, and anti-debugging scripts to bypass detection and hinder analysis.

“Lately, the Tycoon 2FA landing pages have incorporated a clever obfuscation technique using invisible Unicode characters. This technique, when paired with JavaScript Proxy objects, is designed to complicate static analysis and defer script execution until runtime.” reported Trustwave. “This behavior is demonstrated in a real-world Tycoon 2FA phishing landing page, as shown in this Urlscan.io session: https://urlscan.io/result/0195c73f-bfd0-7000-8386-94b11ace6088/dom/“

Tycoon2FA PhaaS
Source: Trustwave – Tycoon 2FA using invisible Unicode characters to encode JavaScript code. The obfuscation is actually quite simple but clever.

Tycoon 2FA replaced third-party CAPTCHAs like Cloudflare Turnstile with a custom HTML5 canvas-based solution. This improvement allows for evading detection, reduces fingerprinting, and hinders automated analysis using randomized text, noise, and distortions.

The Phishing-as-a-Service platform uses anti-debugging scripts to block dev tools, detect automation, prevent right-click, and spot paused execution. If analysis is suspected, it redirects to rakuten.com boosting evasion and extending phishing campaign lifespans.

“The recent updates to the Tycoon 2FA kit show a clear move toward stealth and evasion. While none of these techniques are groundbreaking individually, their combined use can complicate detection and response.” concludes the report that includes Yara rule for detection. “Security teams should consider behavior-based monitoring, browser sandboxing, and a deeper inspection of JavaScript patterns to stay ahead of these tactics.”

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, phishing)


