
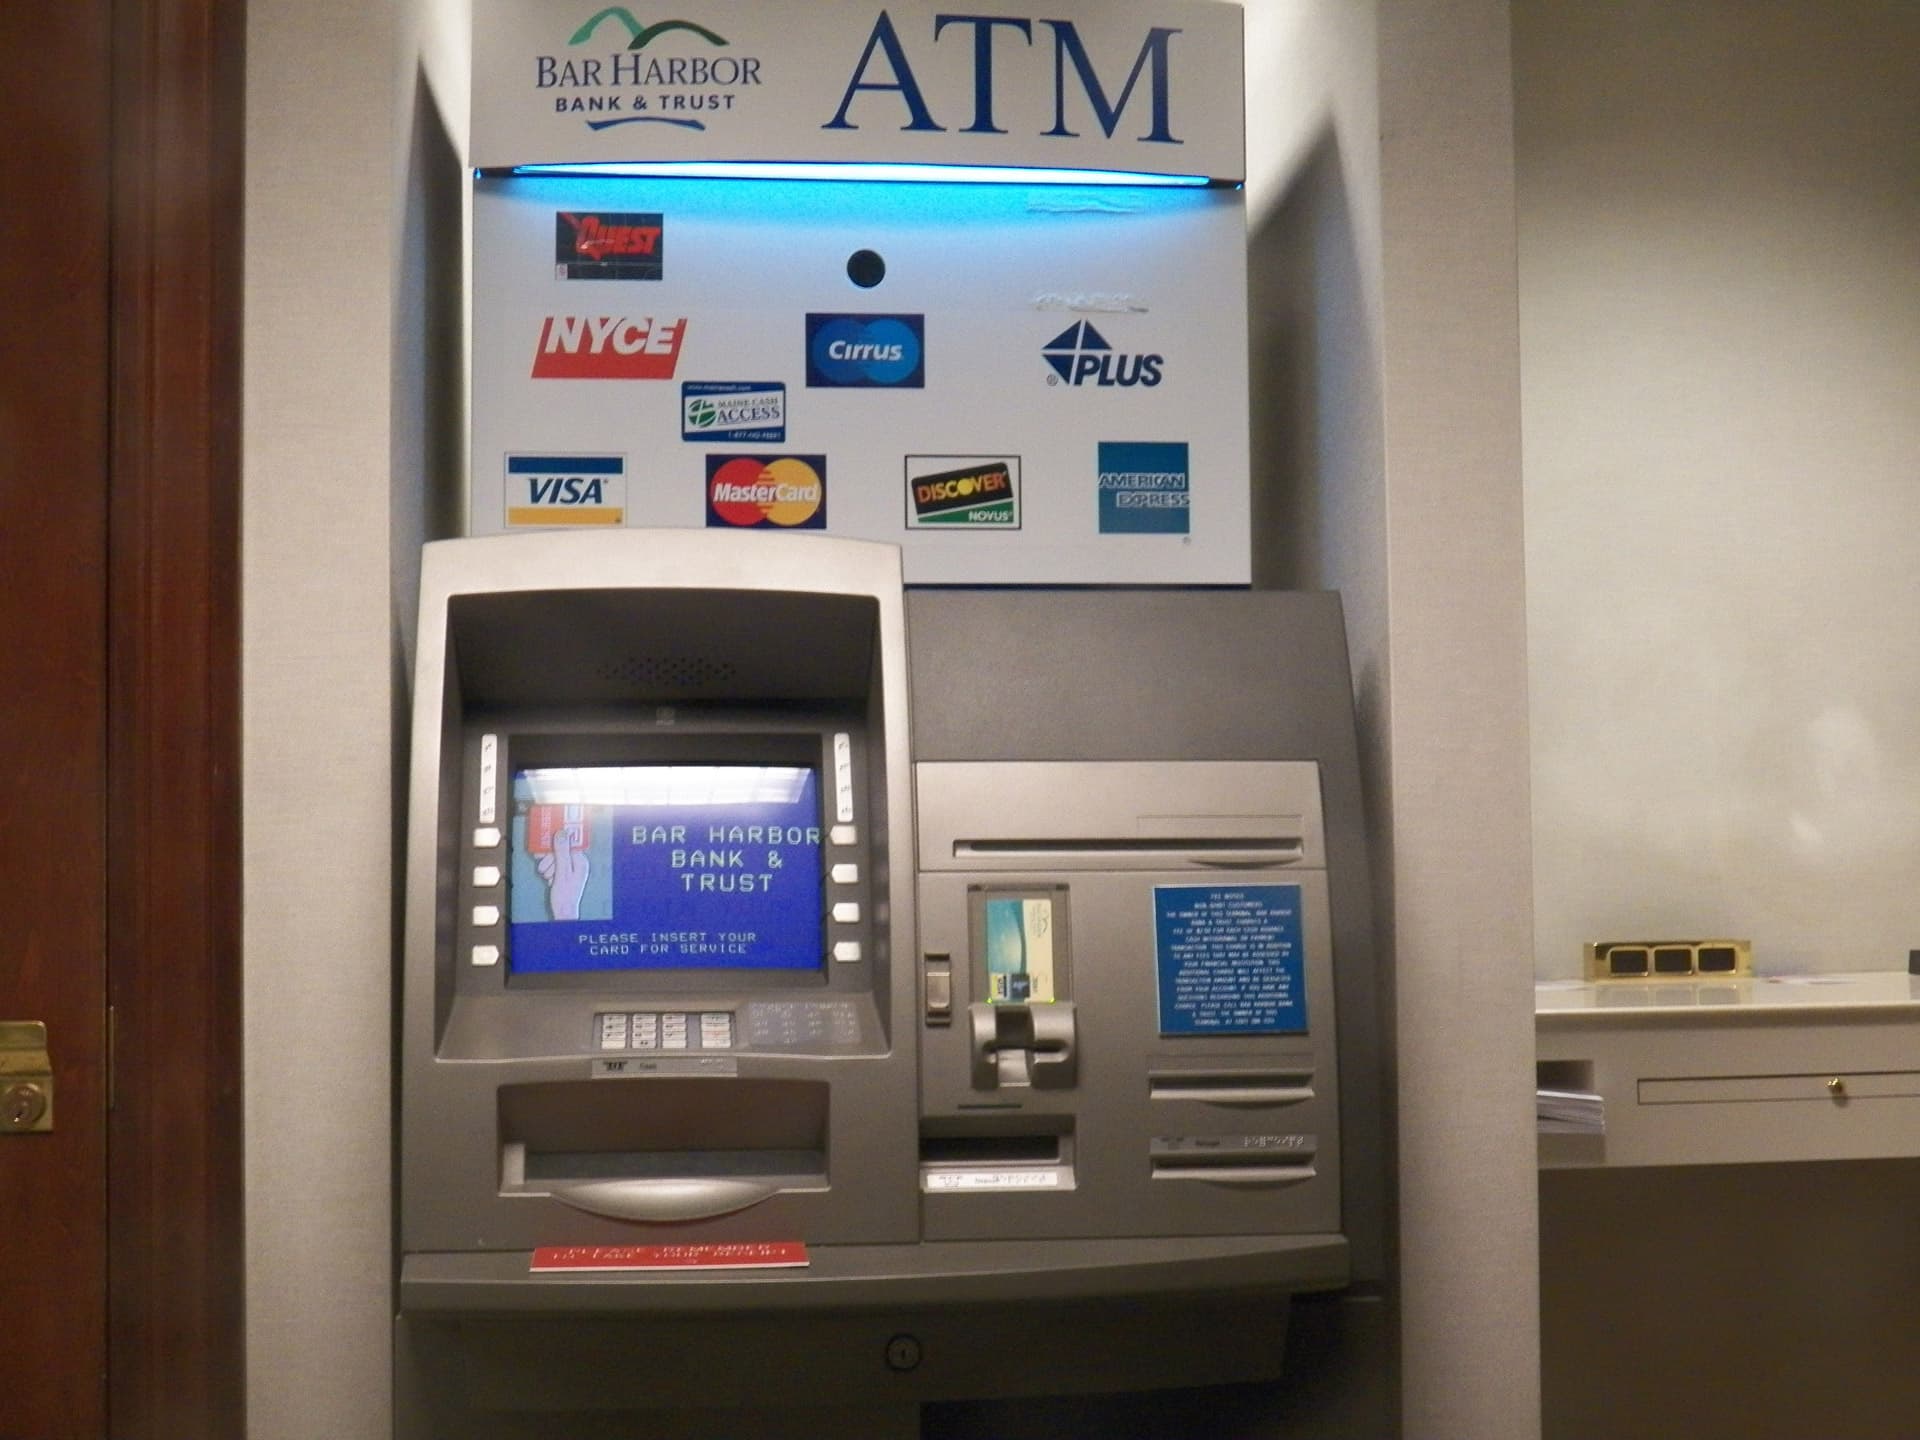
Criminal gangs have stolen millions of dollars from ATMs worldwide using the Tyupkin malware which forces machines to dispense cash.
Criminal gangs in Eastern Europe are increasing the number of attacks against automated teller machines (ATMs), not only tampering the machine with card skimmers which steal debit card data, but also using malware.
The malicious code used by cyber criminals allow hackers to steal cash from the ATM without using cloned credit cards. The Interpol conducted a joint operation with experts at Kaspersky Lab, which allowed them to detect the Tyupkin malware on nearly 50 machines.
The infected machines are ATMs from a particular manufacturer running a 32-bit version of Windows as explained by the experts involved in the investigations.
As explained in a blog post on SecureList, Tyupkin submissions to Virus Total are mainly from Russia (20), but other samples (4) were reported also from the United States, India and China.

Malware researchers at Kaspersky have detected several variants of Tyupkin malware, they had the opportunity to evaluate various improvements over the time, the latest variant coded as. d, includes anti-debug and anti-emulation features and is also able to neutralize application security software from a particular vendor.
The attackers use to compromise ATMs without a sufficient physical security and running on outdated or not updated OS vulnerable to the malware-based attacks. The criminals targeted the ATMs installing the malware by uploading it from a bootable CD, two files are then copied to the ATM system, an executable and a debugging file which is removed after a registry key is created to ensure persistence. Once infected the ATM, the malicious code waits for user input, which it accepts only on Sunday and Monday nights.

The hackers configured the malware to run only at specific times, typically in the night, and they protected the access to the infected ATM through a challenge-response mechanism. The technique was implemented to allow a unique access to the ATM as explained by researchers:
“When the key is entered correctly, the malware displays information on how much money is available in every cassette and allows an attacker with physical access to the ATM to withdraw 40 notes from the selected cassette,” the researchers wrote.
The malware also disables the local area network, the measure allows attackers to avoid any remote diagnostics, which c0uld detect malware and run countermeasures to neutralize it.
The experts have no doubts, criminals will explore new technologies to steal money from banking systems.
“Offenders are constantly identifying new ways to evolve their methodologies to commit crimes, and it is essential that we keep law enforcement in our member countries involved and informed about current trends and modus operandi,” said Sanjay Virmani, Director of the INTERPOL Digital Crime Centre.
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(Security Affairs – ATM, Tyupkin malware)
[adrotate banner=”5″]
[adrotate banner=”13″]


