
The threat actor UAC-0099 is exploiting a flaw in the WinRAR to deliver LONEPAGE malware in attacks against Ukraine.
A threat actor, tracked as UAC-0099, continues to target Ukraine. In some attacks, the APT group exploited a high-severity WinRAR flaw CVE-2023-38831 to deliver the LONEPAGE malware.
UAC-0099 threat actor has targeted Ukraine since mid-2022, it was spotted targeting Ukrainian employees working for companies outside of Ukraine.
In May 2023, CERT-UA warned of cyberespionage attacks carried out by UAC-0099 against state organizations and media representatives of Ukraine
Since the CERT-UA publication in May, Deep Instinct has identified new attacks carried out by “UAC-0099” against Ukrainian targets.
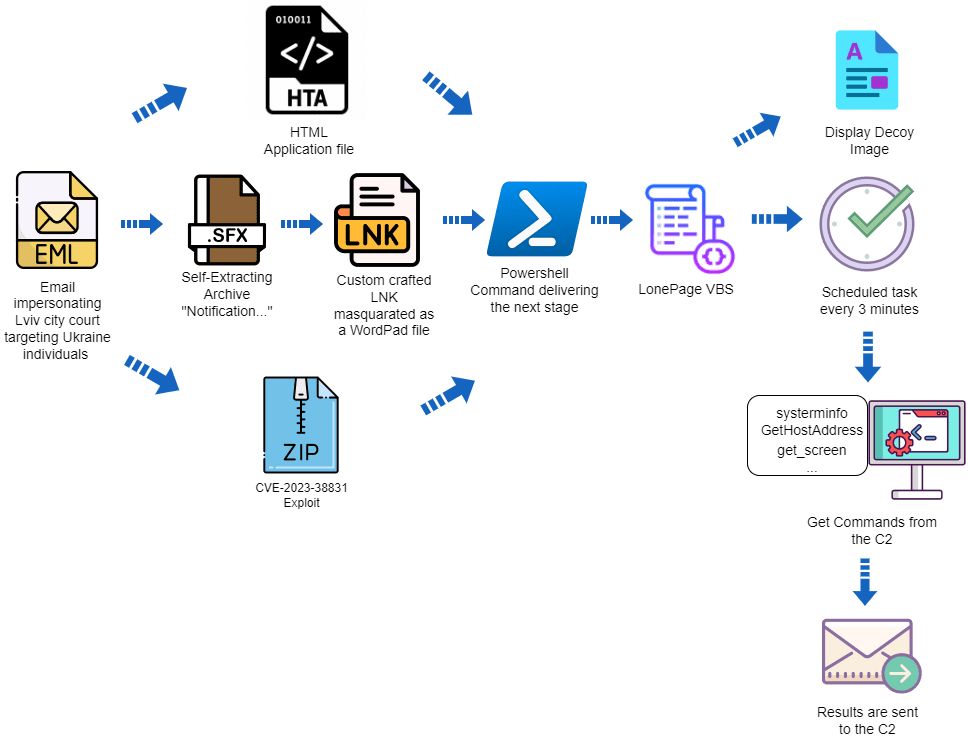
In early August, the group UAC-0099 sent an email impersonating the Lviv city court using the ukr.net email service.
The group used different different infection vectors, the researchers detailed phishing attacks using HTA, RAR, and LNK file attachments. The last-stage malware is the Visual Basic Script (VBS) malware LONEPAGE.
The attack chains leveraged phishing messages containing HTA, RAR, and LNK file attachments that led to the deployment of the Visual Basic Script (VBS) malware LONEPAGE. The malicious code can retrieve additional payloads, including keyloggers and info-stealers.

Deep Instinct reported that the group UAC-0099 exploited the WinRAR flaw CVE-2023-38831, a POC for the issue is available on GitHub. The WinRAR version 6.23 which was released on August 2, 2023, addressed the vulnerability.
“the attacker creates an archive with a benign filename with a space after the file extension — for example, “poc.pdf .” The archive includes a folder with the same name, including the space (something that is not possible under normal conditions, since the operating system does not allow the creation of a file with the same name). The folder includes an additional file with the same name as the benign file, including a space, followed by a “.cmd” extension.” reads the report published by Deep Instinct. “When a user opens a ZIP file containing these files in an unpatched version of WinRAR and double-clicks on the benign file, the file with the “cmd” extension is executed instead.”
The researchers pointed out that this attack technique can also deceive security-savvy victims.
You can find a POC for the vulnerability in GitHub. A patched WinRAR (version 6.23) was released on August 2, 2023.
“The tactics used by “UAC-0099” are simple, yet effective. Despite the different initial infection vectors, the core infection is the same — they rely on PowerShell and the creation of a scheduled task that executes a VBS file.” concludes the report. “The WinRAR exploitation is an interesting choice. Some people don’t update their software in a timely fashion, even with automatic updates. WinRAR requires a manual update, meaning that even if a patch is available, many people will likely still have a vulnerable version of WinRAR installed.”
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, WinRAR)


