
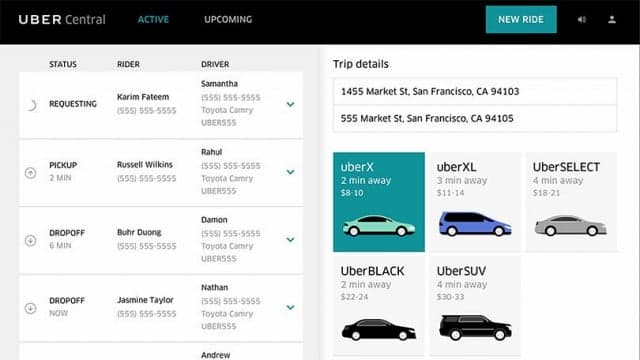
Bounty hunter Kevin Roh has discovered several security vulnerabilities in the Uber UberCENTRAL Tool that exposed user data.
Security expert and bounty hunter Kevin Roh has discovered several security vulnerabilities in Uber’s UberCENTRAL Tool that exposed user data.
The UberCENTRAL service was launched in July, according to the company it is a dashboard that enables any business to request, manage, and pay for multiple Uber rides on behalf of their customers.
The UberCENTRAL console could be used by operators (i.e. employees) who can request rides for their customers. Administrators can easily add operators using only their email address.
Roh described in a blog post the flaws he discovered during his tests.
The first flaw allows enumerating userUUID via emails, an attacker can send requests with possible email addresses and if the address is associated with an account the server will include the user’s UUID in the response.
If the email address is not valid, the response sent by the server will contain an error.
Below an example of request sent to the server:
POST /admin/api/organizations/[organizationUUID]/operators HTTP/1.1 Host: central.uber.com Connection: close Content-Length: 40 Accept: application/json Origin: https://central.uber.com x-csrf-token: XXXX x-uber-origin: web-central-admin User-Agent: Mozilla/5.0 (Macintosh; Intel Mac OS X 10_11_6) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/52.0.2743.116 Safari/537.36 Content-Type: application/json Referer: https://central.uber.com/admin/locations Accept-Encoding: gzip, deflate, br Accept-Language: en-US,en;q=0.8 Cookie: _ua=XXXX {"operatorEmail":"r****@unlv.nevada.edu"}
The attacker could write a simple script that tries all possible values for the ‘operationEmail‘ parameter and analyze all the responses received by the server for each of them.

The second flaw is similar to the first one, it allows enumerating userUUID via GET request instead email addresses.
Roh found a third flaw that could have been exploited to obtain much more data, including full name, phone numbers, emails and userUUID.
The vulnerabilities were reported to the company between September and October, and the company promptly patched them in October.
Uber awarded the expert Roh under the company bounty program. The hacker received hundreds of dollars for each of the vulnerabilities, the exact amounts have not been revealed.
[adrotate banner=”9″]
(Security Affairs – UberCentral, hacking)


