
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Malicious package containing Bytecoin cryptocurrency miner found on the Ubuntu Snap Store

An Ubuntu user has spotted a Bytecoin cryptocurrency miner hidden in the source code of an Ubuntu Snap Pack in the Official Ubuntu Snap Store. An Ubuntu user that goes online with the GitHub moniker “Tarwirdur” has discovered a malware in the source code of an Ubuntu snap package hosted on the official Ubuntu Snap Store, a […]

2048buntu-game ubuntu snap store

An Ubuntu user has spotted a Bytecoin cryptocurrency miner hidden in the source code of an Ubuntu Snap Pack in the Official Ubuntu Snap Store.

An Ubuntu user that goes online with the GitHub moniker “Tarwirdur” has discovered a malware in the source code of an Ubuntu snap package hosted on the official Ubuntu Snap Store, a first analysis revealed that it is a cryptocurrency miner.

The malicious code was able to mine the Bytecoin (BCN) cryptocurrency, the account hardcoded in the malware is  “myfirstferrari@protonmail.com.”

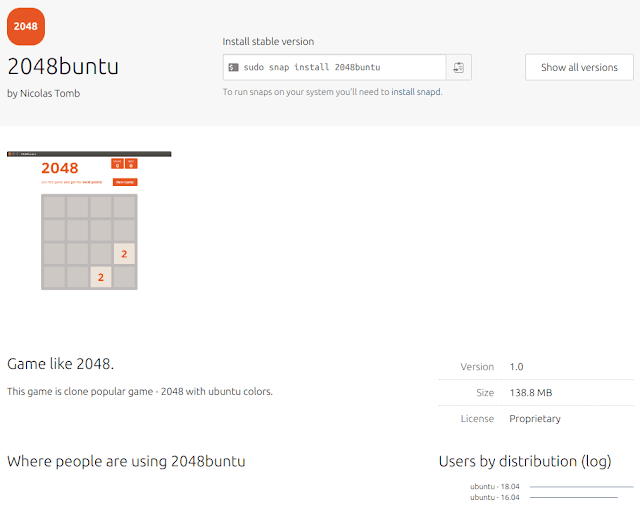
The malicious app is 2048buntu, it is a copycat of the legitimate of the 2024 game included as an Ubuntu snap.

2048buntu-game ubuntu snap store

Tarwirdur discovered the app contained a cryptocurrency mining application disguised as the “systemd” daemon, the package also includes an init script that allows gaining boot persistence on the target.

Tarwirdur reported his discovery to the maintainers at the Ubuntu Snap Store team that promptly removed the app. The user also noticed another app uploaded by the same developers and after a check, he discovered it also contained a malicious code and for this reason, it was removed too.

“At least two of the snap packages, 2048buntu and Hextris, uploaded to the Ubuntu Snaps Store by user Nicolas Tomb, contained malware. All packages by Nicolas have since been removed from the Ubuntu Snaps Store, “pending further investigations“.” states a post published on the website linuxuprising.com.

Currently, it is impossible to establish the number of affected users because the Ubuntu Snap Store does not provide an install count.

The problem is that submitted snaps do not go through a security check, this means that ill-intentioned can upload malicious snap packages to the Ubuntu Snap Store.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(Security Affairs – Ubuntu Snap Store, cryptocurrency miner)

[adrotate banner=”5″]

[adrotate banner=”13″]


