
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

UK politicians’ login credentials up for sale in the dark web

Russians hackers are offering for sale on the dark web login credentials of thousands of top UK politicians, top officials, and diplomats. According to The Times, Russians hackers are selling on the dark web login credentials of thousands of top UK politicians, top officials, and diplomats. Journalists at the British newspaper have found two huge […]

UK politicians’ login credentials up for sale in the dark web

Russians hackers are offering for sale on the dark web login credentials of thousands of top UK politicians, top officials, and diplomats.

According to The Times, Russians hackers are selling on the dark web login credentials of thousands of top UK politicians, top officials, and diplomats.

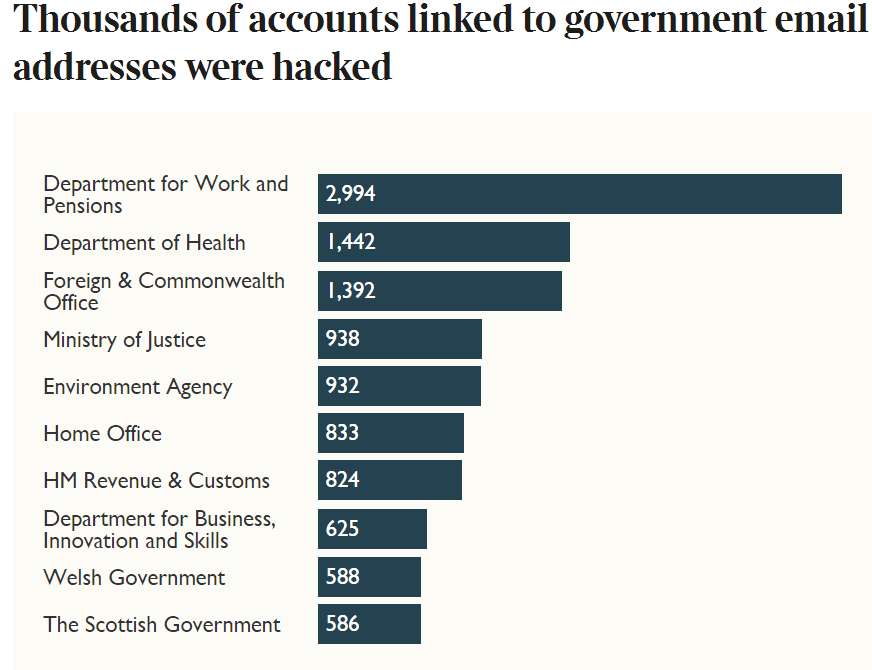
Journalists at the British newspaper have found two huge lists of stolen credentials that were available for sale on Russian-speaking hacking sites. The huge trove of credentials included the log-in details of 1,000 British MPs and parliamentary staff, 7,000 police employees and over 1,000 Foreign Office officials.

“Passwords belonging to British cabinet ministers, ambassadors, and senior police officers have been traded online by Russian hackers, an investigation by The Times has found.” reads The Times. “Two huge lists of stolen data reveal private log-in details of 1,000 British MPs and parliamentary staff, 7,000 police employees and more than 1,000 Foreign Office officials, an analysis shows — including the department’s own head of IT.”

uk politicians data leak

According to experts that analyzed the lists speculate they are composed of old credentials. The list appears as composed starting from data coming from old data breaches such as LinkedIn and MySpace.

“They include passwords used by the former ambassador to Israel and the director-general of the Department for Exiting the European Union.” continues The Times.

The main risk is related to the possibility that victim used the same credentials to access other sensitive systems and networks.

It is interesting to note that despite official guidance advising the use of strong passwords, the data leak shows that many politicians were using easy to guess passwords.

“Peter Jones, the Foreign Office’s chief operating officer, who has overall responsibility for IT, appears to have used a highly insecure password which occurred more than 3,700 times in one of the lists.” continues the newspaper.

Many victims re-used insecure passwords on multiple websites. such as the former Cabinet Office minister Brooks Newmark,

[adrotate banner=”9″]

Pierluigi Paganini

(Security Affairs – UK politicians,  data breach)

[adrotate banner=”13″]


