
New Underminer exploit kit delivers a bootkit that infects the system’s boot sectors as well as a cryptocurrency miner dubbed Hidden Mellifera.
Malware researchers from Trend Micro have spotted a new exploit kit, tracked as Underminer exploit kit, delivering a bootkit that infects the system’s boot sectors as well as a cryptocurrency miner dubbed Hidden Mellifera.
“We discovered a new exploit kit we named Underminer that employs capabilities used by other exploit kits to deter researchers from tracking its activity or reverse engineering the payloads.” reads the analysis published by TrendMicro.
“Underminer delivers a bootkit that infects the system’s boot sectors as well as a cryptocurrency-mining malware named Hidden Mellifera.”
Researchers first noticed the Underminer Exploit activity on July 17 while it was distributing the payloads mainly to Asian countries, mostly in Japan (69,75%) and Taiwan (10,52%).
Underminer transfers the malicious payloads via an encrypted transmission control protocol (TCP) tunnel and packages malicious files with a customized format similar to ROM file system format (romfs). According to the experts, this makes it difficult to analyze the malicious code.
The Underminer exploit kit appears to have been created in November 2017 when it only included the code for the exploitation of Flash vulnerabilities and delivered fileless payloads to deliver and execute the malware.
The Underminer EK includes functionalities also employed by other exploit kits, including:
- browser profiling and filtering;
- preventing of client revisits;
- URL randomization;
- asymmetric encryption of payloads;
The EK redirect visitors to a landing page that profile and detect the user’s Adobe Flash Player version and browser type via user-agent.
In case the visitor’s profile does not match the one associated with a target of interest, the exploit kit will not deliver malicious content and redirect the visitor to a clean website.
The Underminer exploit kit also sets a token to the browser cookie, with this trick if the victim already accessed the landing page, it only delivers an HTTP 404 error message instead of payloads.
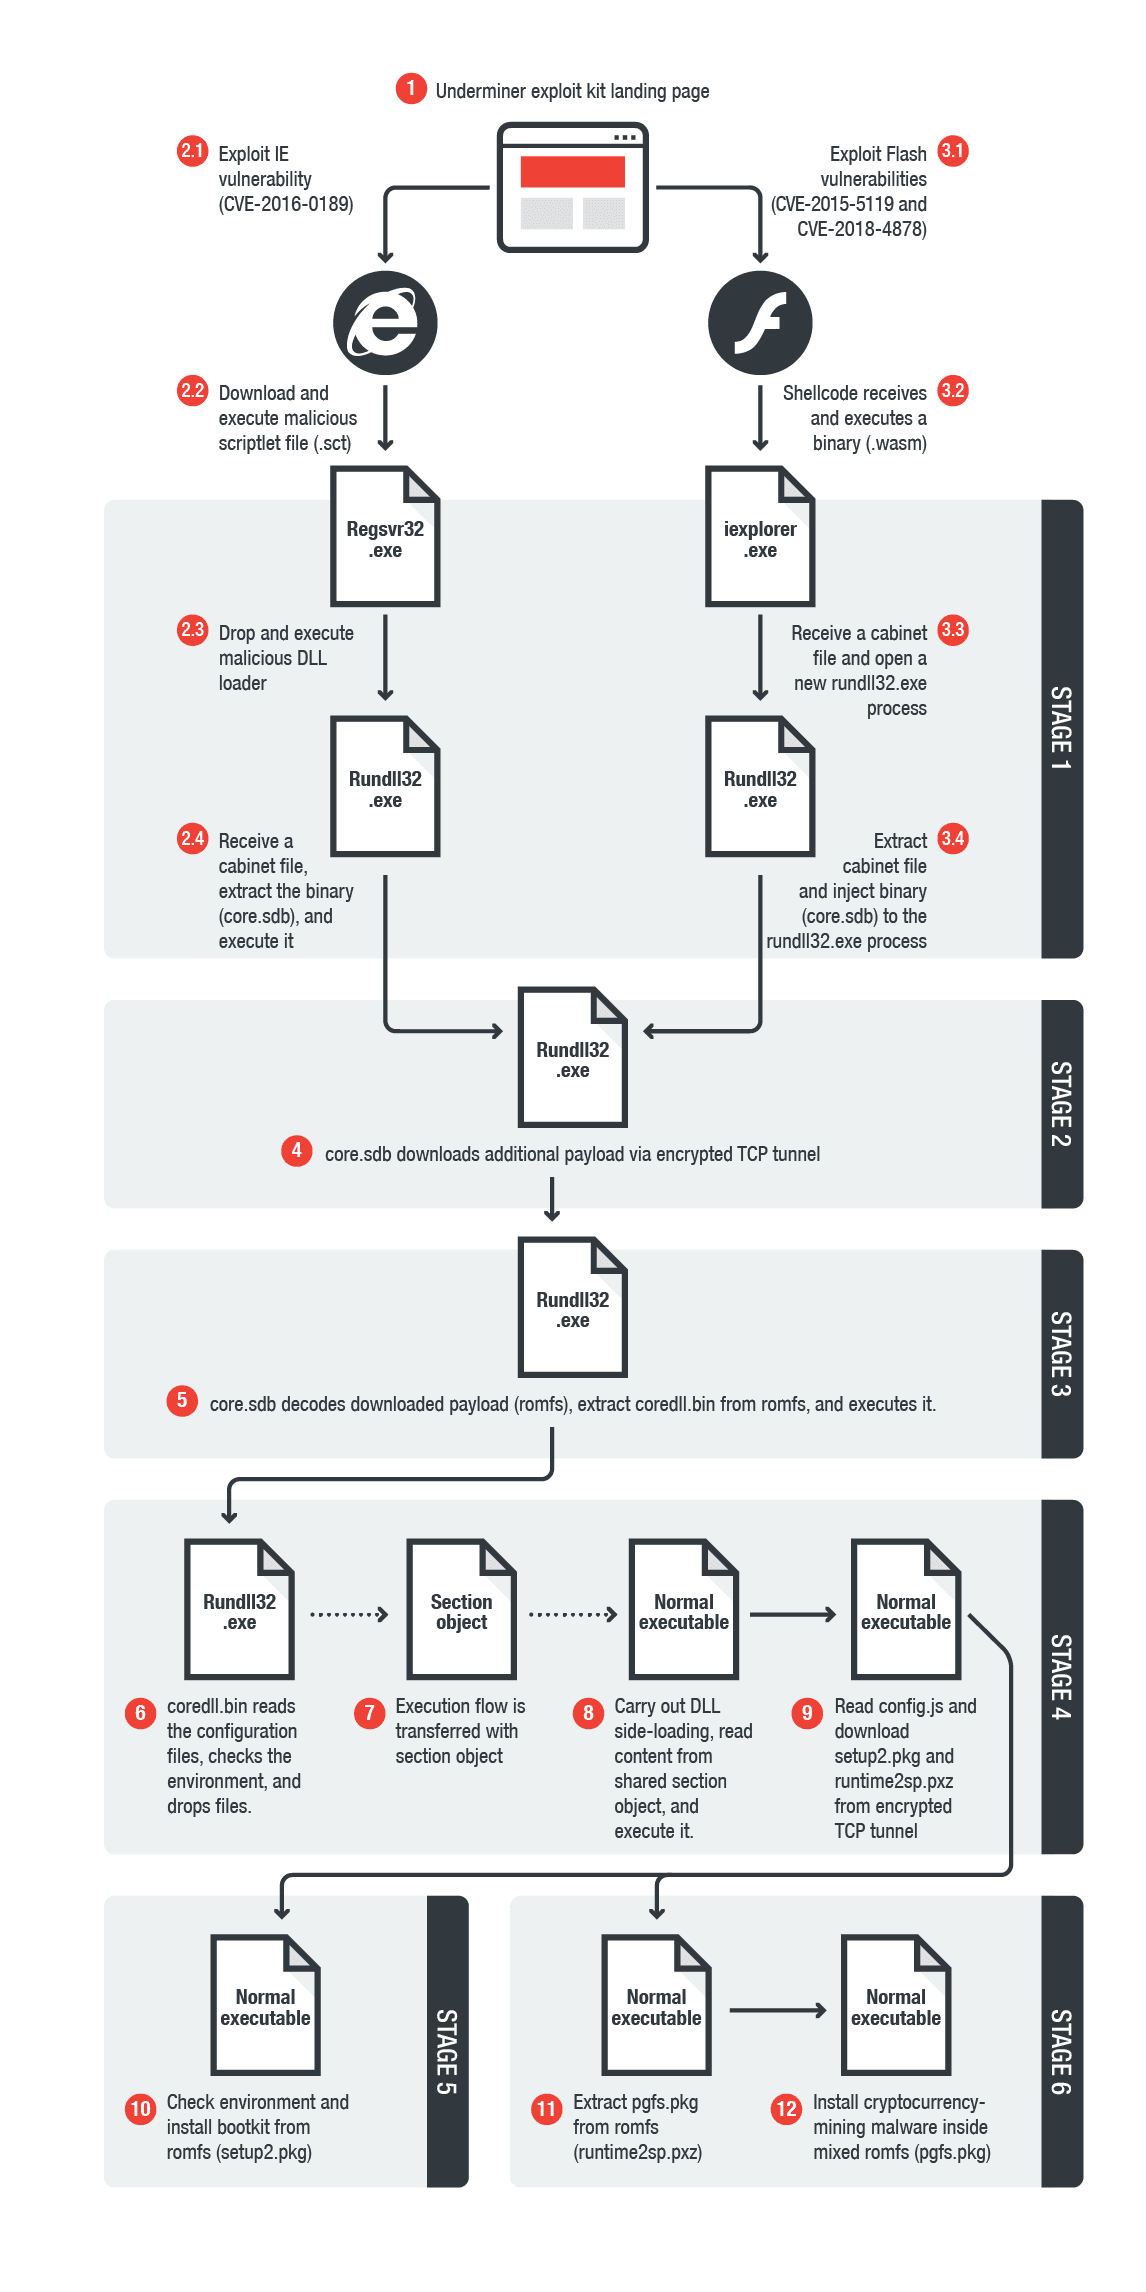
Researchers discovered that the Underminer exploit kit still includes a small number of exploits. The experts have spotted the code to trigger the following vulnerabilities:
- CVE-2015-5119, a use-after-free vulnerability in Adobe Flash Player patched in July 2015.
- CVE-2016-0189, a memory corruption vulnerability in Internet Explorer (IE) patched in May 2016.
- CVE-2018-4878, a use-after-free vulnerability in Adobe Flash Player patched in February 2018.
All the above flaws have been exploited by other EKs in the past.
Below the infection flow of Underminer’s exploits described by Trend Micro.
“Like other exploits before it, we expect Underminer to hone their techniques to further obfuscate the ways they deliver their malicious content and exploit more vulnerabilities while deterring security researchers from looking into their activities. And given the nature of their operations, we also expect them to diversify their payloads.” concludes Trend Micro.


