
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

United Airlines accounts could be easily locked-out

A security expert discovered that United Airlines accounts could be locked-out by running a brute-force attack. The effects on a large scale could be serious. According to WorldMate security officer Yosi Dahan, a threat actor could easily lock-out United Airlines users from their accounts. Dahan explained that reported the security issue in March under the United Airlines bug bounty […]

United Airlines accounts could be easily locked-out

A security expert discovered that United Airlines accounts could be locked-out by running a brute-force attack. The effects on a large scale could be serious.

According to WorldMate security officer Yosi Dahan, a threat actor could easily lock-out United Airlines users from their accounts. Dahan explained that reported the security issue in March under the United Airlines bug bounty program, but he hasn’t received the reply from the company.

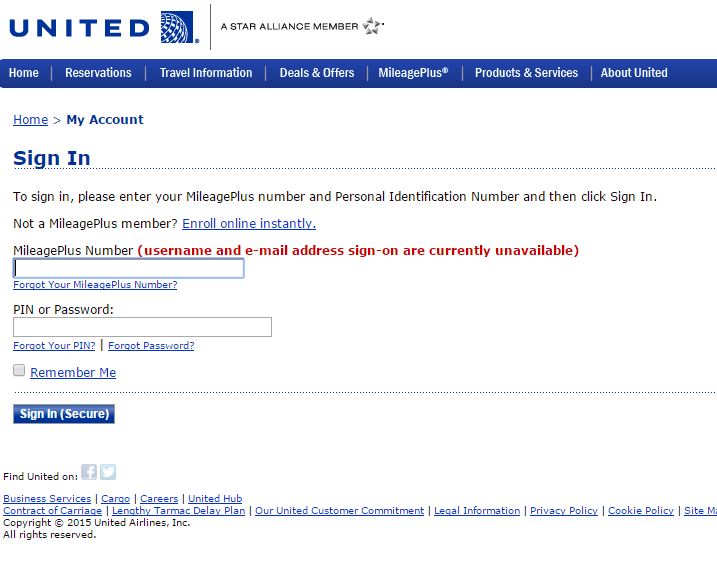
Dahan reported in The Register that someone could run a brute-force attack by enumerating MileagePlus account numbers and force a significant number of United Airlines customers to contact the company customer care service due to unclock their blocked accounts.
united airlines 2

Four incorrect attempts cause the block of the account that could be unlocked after a phone call to an operator of the United Airlines.

“An attacker can generate a targeted attack against UA in which he will be able to lock all the accounts related to the MileagePlus program by generating a user ID and random pin codes combined of four numbers, or some random passwords,” Dahan says. “In order to unlock and reset the password of the locked account, a user would have to call the support center.”

As usually happens in these cases, in order to run a bruteforce attack it is sufficient to write a few lines of code as confirmed by Dahan.

“With a simple script, an attacker can generate any account ID in the form of AA000000, for example: AA000001, AA000002 until he reaches ZZ999999.” he said.

Another element of concern related to the MileagePlus system is that the service will inform users when they are using a wrong identification number distinguish the case of erroneous password usage. This means that an attacker can have further information to drive its brute force attack.

Just for curiosity, differently from other bounty programs, the United Airlines is offering flyer points, remote code execution bugs are awarded with the greatest number of points.

Let’s wait for a comment from the United Airlines.

Pierluigi Paganini

(Security Affairs – United Airlines, hacking)


