
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Cyber Crime

Unrecom phishing campaign hit high-profile entities globally

Security Experts at Fidelis Cyber Security firm have recently discovered a new phishing campaign using the Unrecom RAT (remote access trojan). Fidelis Cyber Security firm has recently issued the Fidelis Threat Advisory #1013 to detail a phishing campaign using the Unrecom RAT (remote access trojan). Experts at Fidelis during the last two weeks have observed an increase […]

Unrecom phishing campaign hit high-profile entities globally

Security Experts at Fidelis Cyber Security firm have recently discovered a new phishing campaign using the Unrecom RAT (remote access trojan).

Fidelis Cyber Security firm has recently issued the Fidelis Threat Advisory #1013 to detail a phishing campaign using the Unrecom RAT (remote access trojan).

Experts at Fidelis during the last two weeks have observed an increase in attack activity, based on this malicious agent, against the US and local government, technology, advisory services, health, and financial. The campaign also hit the financial industry in Saudi Arabia and Russia.

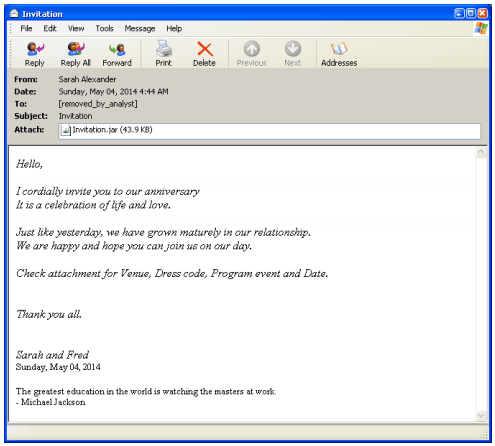
The Unrecom remote access tool was spread as attachments of phishing emails try to trick the users into thinking the emails are legitimate. Following a list of names used for the attachment in the phishing campaign:

  • The  Payment Invoice.jar
  • Payment details.jar
  • POR#94586.zip/POR#94586.jar
  • INV#94586.zip/INV#94586.jar
  • Invitation.jar
  • reports-pdf.jar
  • US$25k.jar,
  • DBC_BANK_IMG_23456_156.jar
  • lremit_Transfer_Error_Page.jar.

The Unrecom is a multi-platform Java-based remote access tool has a low detection rate, it goes undetected by most AntiVirus solutions.  Last version of this RAT is 3.2 and is being sold at “unrecom[.]net” for $500  (Enterprise Version) and $200 (Full Version).

“The evolution of Unrecom RAT dates from its beginnings as a tool known as Frutas RAT, subsequently branded as Adwind RAT, and now Unrecom RAT. In 2013, it was reported that Frutas RAT was used in phishing email campaigns against high profile companies in Europe and Asia in sectors such as finance, mining, telecom, and government.” states the advisory.

Unrecom 2_0 remote access tool

As many other remote access tools also Unrecom RAT provides basic features to gain remote control over the victims:

  • Collection of System Information (e.g. IP, OS version, memory RAM information, Java version, Computer Name, User account compromised, etc.)
  • Upload & Execute additional malware, typically exploiting vulnerabilities derived from collected system information
  • Capture Webcam and Microphone, without user notification
  • Remote Desktop to watch user activity
  • File Manager allowing access to files in the context of the current user
  • Browser Password theft
  • Keylogging to capture passwords otherwise obscured from viewing

The advisory reveals that Command & Control (CnC) servers used by the Unrecom RAT in this campaign were used in the past by variants of the DarkComet and AcromRAT malware which have been observed in large volumes in the Middle East.

Following the list of indicators provided in the advisory … be aware!

Unrecom 2_0 remote access tool Indicators


(Security Affairs –  Unrecom RAT, phishing)


