
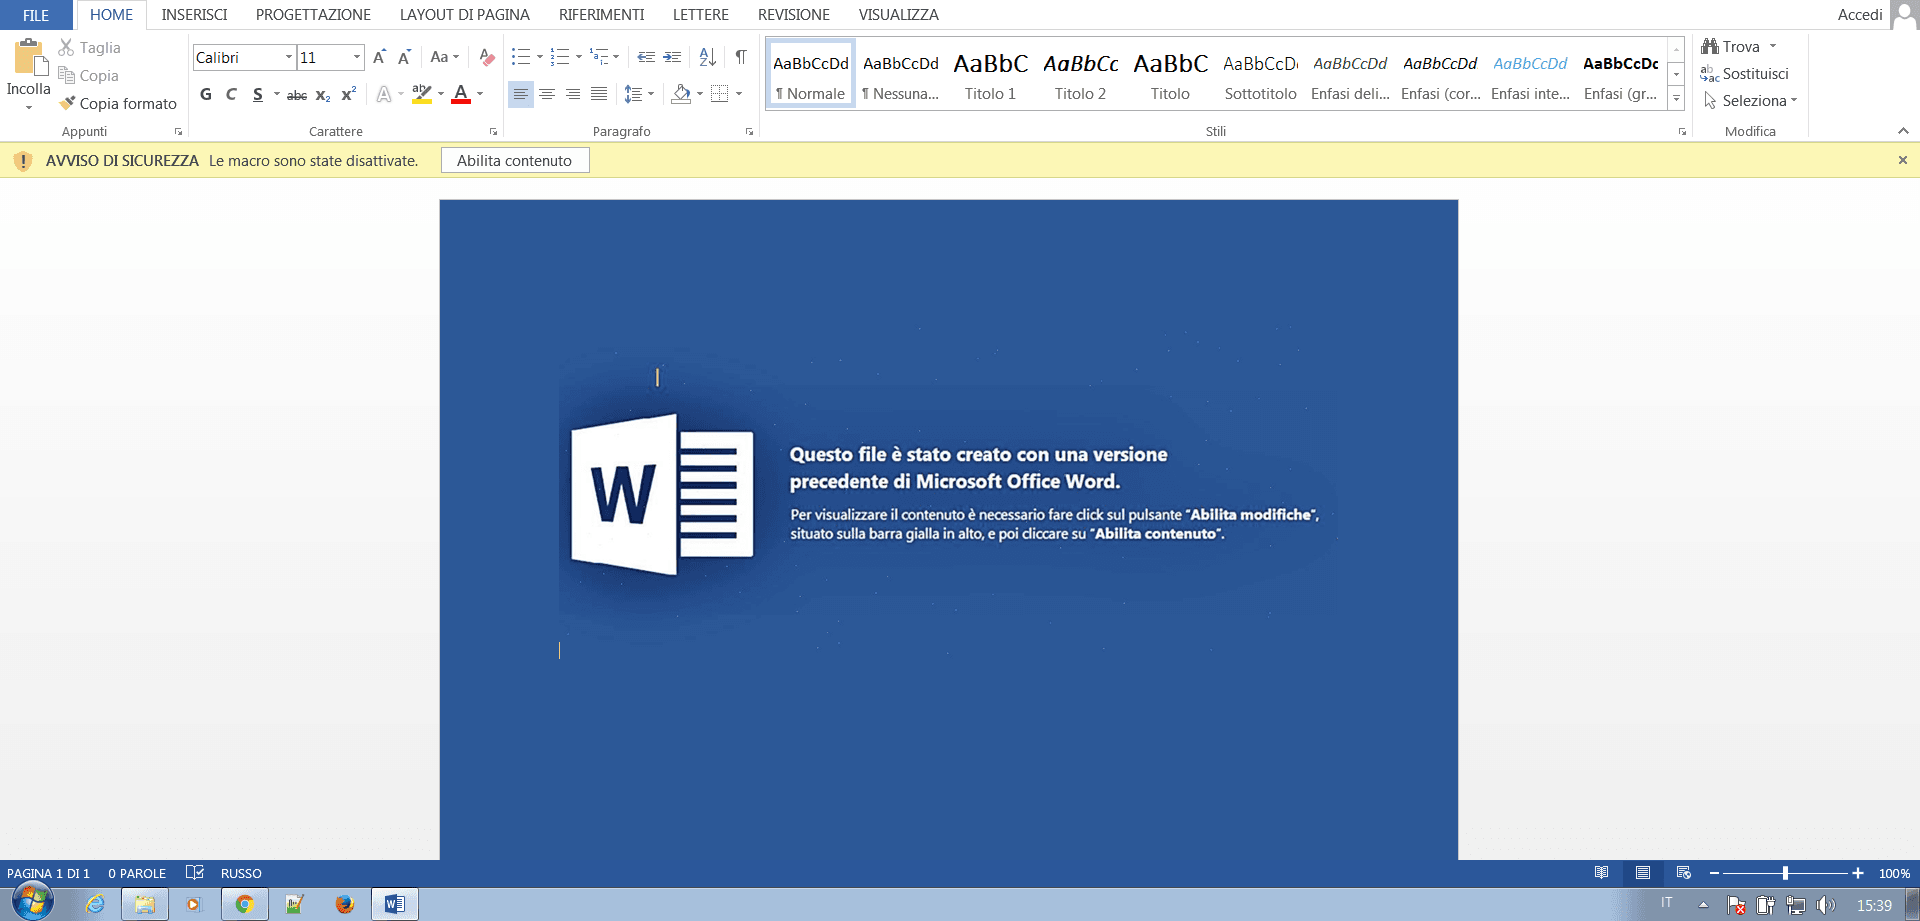
Ursnif phishing Word document screen
Malware researchers from CSE Cybsec ZLab discovered a missed link between the Necurs Botnet and a variant of the Ursnif trojan that recently hit Italy.
Starting from 6th June, a new version of the infamous banking trojan Ursnif hit Italian companies. This malware is well known to the cyber-security community, the Ursnif banking Trojan was the most active malware code in the financial sector in 2016 and the trend continued through 2017 to date.
In previous campaigns, the Ursnif banking Trojan targeted users in Japan, North America, Europe and Australia, later the authors improved their evasion technique to target users worldwide, especially in Japan.
The malware is able to steal users’ credentials, credentials for local webmail, cloud storage, cryptocurrency exchange platforms and e-commerce sites.
The malware has been active since at least 2009, as reported by Microsoft.
The technical information reported by Microsoft refers to an older version of the malware, but the version that is spreading in Italy presents many improvements.
CSE Cybsec ZLab researchers are conducting analysis on the latest version of the malware. The experts started the investigation after the discovery of a suspicious file that was used in a targeted attack against one of its customers.
The attachment used in the campaign that hit Italian companies is a weaponized Microsoft Word document, it uses a social engineering technique to trick users into enabling macros in order to allow the correct view of its content.

Ursnif phishing Word document screen
Moreover, Ursnif once infected a new machine will attempt to spread to any other users in the address book of the compromised email accounts.
In order to trick the victim into opening the malicious email, the message is presented as the reply to an existing conversation conducted by the victim in the past.
While investigating the domains involved in the last phishing campaign against the Italian companies, the researchers discovered many of them were registered by the same email address, “whois-protect[@]hotmail[.]com.”
This email address is directly connected to infamous Necurs Botnet, the malicious architecture that was used in the past months to push many other malware, including Locky, Jaff, GlobeImposter, Dridex , Scarab and the Trickbot.
Further details on the variant of the Ursnif malware that targeted Italian firms, including IoCs and Yara Rules are available in the report published by researchers at ZLAb.
You can download the full ZLAB Malware Analysis Report at the following URL:
http://csecybsec.com/download/zlab/20180621_CSE_Ursnif-Necurs_report.pdf

| [adrotate banner=”9″] | [adrotate banner=”12″] |
(Security Affairs – Ursnif banking trojan, cybercrime)
[adrotate banner=”5″]
[adrotate banner=”13″]


