
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

US teenager pleads guilty to his role in credential stuffing attack on a betting site

US teenager Joseph Garrison pleads guilty to carrying out a credential stuffing attack on a betting website. US teenager Joseph Garrison (19) has pleaded guilty to his involvement in a credential stuffing campaign that targeted user accounts at a fantasy sports and betting website.3 On or about November 18, 2022, the man launched a credential […]

credential stuffing attacks Hot Topic

US teenager Joseph Garrison pleads guilty to carrying out a credential stuffing attack on a betting website.

US teenager Joseph Garrison (19) has pleaded guilty to his involvement in a credential stuffing campaign that targeted user accounts at a fantasy sports and betting website.3

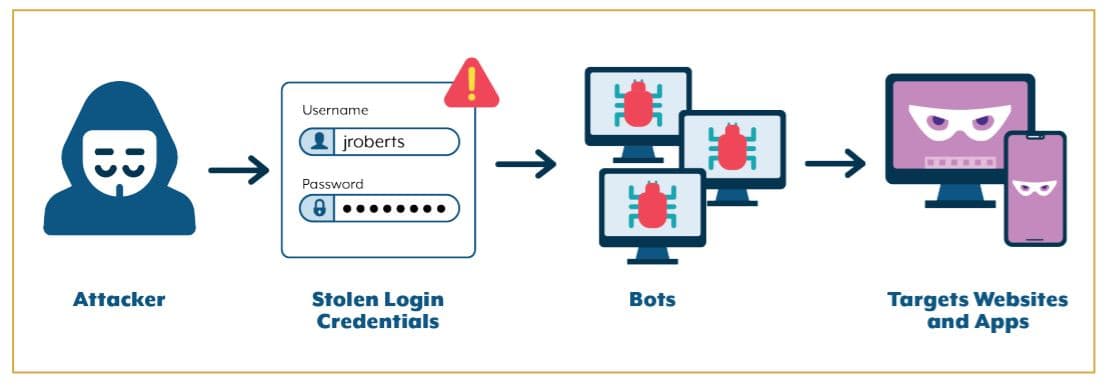
On or about November 18, 2022, the man launched a credential stuffing attack on the Betting Website and gained access to approximately 60,000 accounts. In some cases, the man and his accomplices were able to add a new payment method to the compromised accounts, deposit $5 into that account through the new payment method to verify that method, and then withdraw all the existing funds in the Victim Account through the new payment method. According to court documents, the crooks stole approximately $600,000 from approximately 1,600 compromised accounts.

According to court documents, on November 18, 2022, Garrison launched the attack against the betting site, obtaining access to approximately 60,000 user accounts.

The police discovered on the computer of the man, nearly 40 million credentials that could be used in credentials-stuffing attacks.

“Law enforcement executed a search on GARRISON’s home in February 2023.  In that search, they located programs typically used for credential stuffing attacks.  Those programs require individualized “config” files for a target website to launch credential stuffing attacks, and law enforcement located approximately 700 such config files for dozens of different corporate websites on GARRISON’s computer.” reads the press release published by DoJ. “Law enforcement also located files containing nearly 40 million username and password pairs on GARRISON’s computer, which are also used in credential stuffing attacks.”

The analysis of Garrison’s phone, revealed the conversations between him and his co-conspirators about how to hack the Betting Website and how to steal funds from the victim accounts directly or by selling access to the victim accounts.

According to SecurityWeek, the betting website is DraftKings which in November 2022 announced approximately 68,000 accounts had been compromised in a credential stuffing attack.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, betting)


