
Security Affairs
CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|FBI Blames North Korea for $6 Billion Binance Crypto Theft|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|FBI Blames North Korea for $6 Billion Binance Crypto Theft|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Cybercriminals attack banking customers in EU with V3B phishing kit – PhotoTAN and SmartID supported.

Resecurity uncovered a cybercriminal group that is providing a sophisticated phishing kit, named V3B, to target banking customers in the EU. Resecurity has uncovered a new cybercriminal group providing Phishing-as-a-Service (PhaaS) platform that is equipping fraudsters with sophisticated kit (known as “V3B”) to target banking customers in the EU. “Currently, it is estimated that hundreds […]

V3B phishing kit

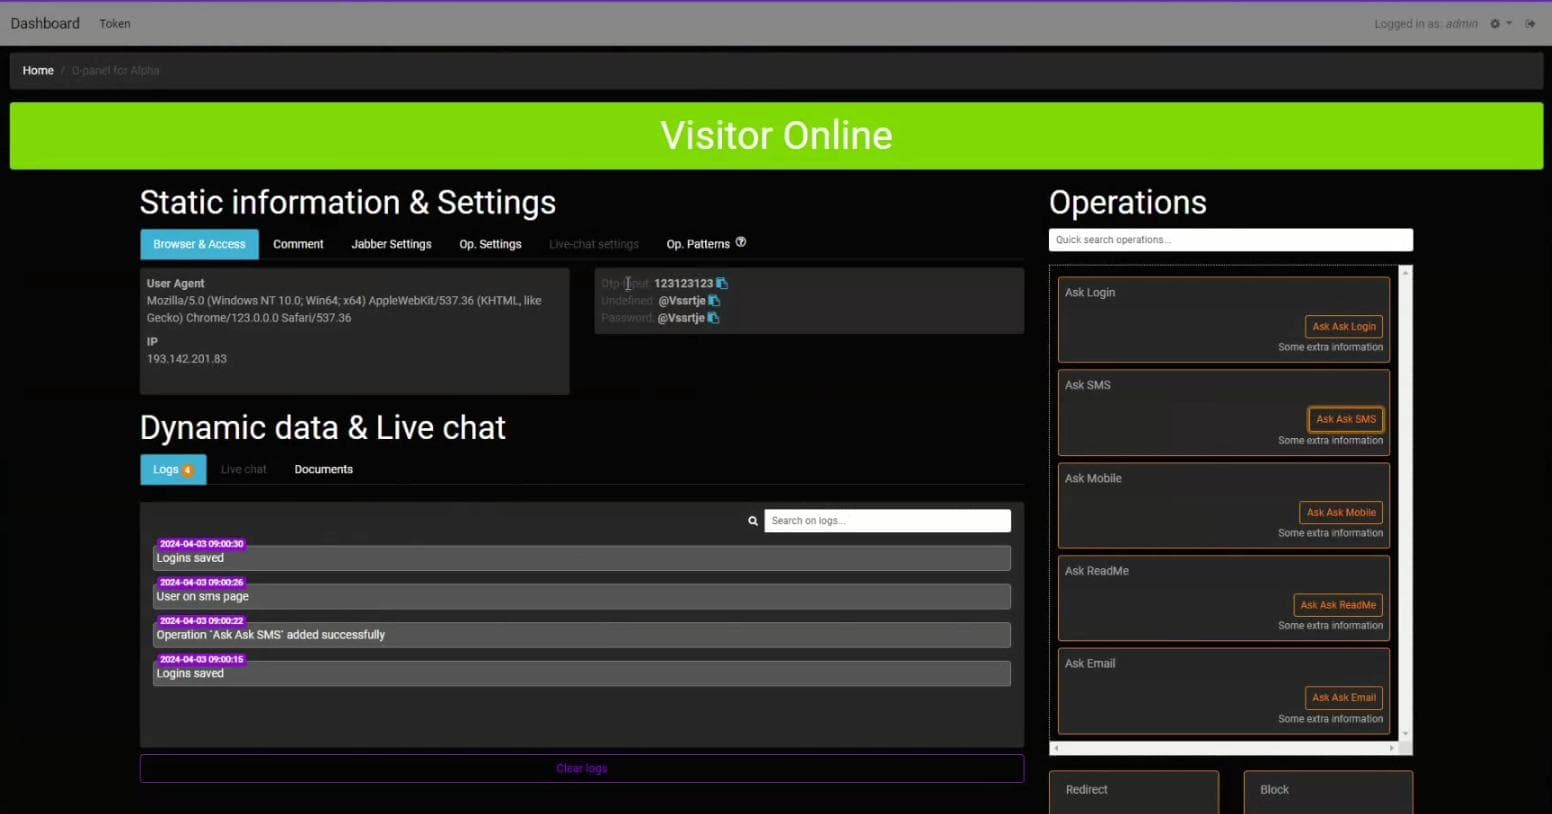
Resecurity uncovered a cybercriminal group that is providing a sophisticated phishing kit, named V3B, to target banking customers in the EU.

Resecurity has uncovered a new cybercriminal group providing Phishing-as-a-Service (PhaaS) platform that is equipping fraudsters with sophisticated kit (known as “V3B”) to target banking customers in the EU.

“Currently, it is estimated that hundreds of cybercriminals are using this kit to commit fraud, leaving victims with empty bank accounts. Their Telegram channel has over 1,255 members, a significant indicator of the scale and scope of the malicious activity being promoted by the group.” reads the report published Resecurity. “The majority of members on this Telegram channel are skilled cybercriminals who specialize in various forms of fraud. These include:

  • Social engineering tactics
  • SIM swapping schemes
  • Banking and credit card fraud”

The attackers use various social engineering and spoofing tactics to trick victims into revealing their sensitive information, which supports real-time interaction to abuse and bypass MFA (Multi-Factor Authentication).

The kit is designed to intercept sensitive information, including banking credentials, credit card and personal information, and OTP/TAN codes. Besides traditional tokens (such as SMS code), the kit supports QR Codes and PhotoTAN method (widely used in Germany and Switzerland), which may indicate that fraudsters are monitoring the latest MFA/2FA technologies implemented by banks and seeking to exploit possible bypass methods to defraud their customers.

V3B phishing kit supports over 54 financial institutions (based in Austria, Belgium, France, Finland, Greece, Germany, Italy, Netherlands, Norway, Poland, Spain), featuring customized and localized templates to mimic authentication and verification processes of major online banking, e-commerce, cryptocurrency providers and payment systems in the EU.

Technical details about the phishing kit are included in the report published by Resecurity: https://www.resecurity.com/blog/article/cybercriminals-attack-banking-customers-in-eu-with-v3b-phishing-kit

Pierluigi Paganini

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

(SecurityAffairs – hacking, V3B)


