
REvil ransomware operators claimed to have breached another healthcare organization, the victim is Valley Health Systems.
During ordinary monitoring activity of data leaks, the Cyble Research Team identified a leak disclosure post published by the REvil ransomware operators claiming to have breached a healthcare organization, the Valley Health Systems.
Healthcare organizations are a privileged target of hackers due to the sensitive data they manage. During this period, due to the ongoing COVID19 pandemic, these structures are under pressure and more exposed to cyber risks.
According to the Cisco/Cybersecurity Ventures Cybersecurity Almanac, the healthcare organizations suffered 2-3 more cyberattacks in 2019 than the average amount for the other industries.
“As the healthcare sector companies continues to improvise their treatment process and patient care with the availability of the new technologies, and on the same side cyber threat actors tends to exploit the vulnerabilities that are made with the technological advancements.” states the post published by Cyble.
“Recently, during the monitoring process of data leaks the Cyble Research Team identified a leak disclosure post in which the REvil ransomware operators claimed to have breached Valley Health Systems.”
The Valley Health Systems has been providing primary and preventative care to approximately 75,000 patients each year in southern West Virginia, southeastern Ohio, and eastern Kentucky. The organization operates over 40 healthcare facilities with over 400 employees working across all their centers.
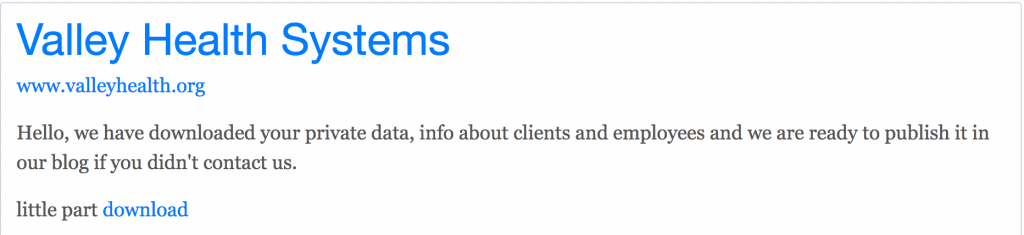
Below is the post published by REvil operators:

The REVil ransomware operators claim to have stolen company sensitive data, including info related to clients, employees, and patients.
Experts shared snapshots folders and also released a small part of a data leak containing the patient’s prescribed prescriptions, patient details (that include full name, date of birth, gender, patient ID), medical scan reports of patients, multiple Digital Imaging and Communications medical files, and much more.

Below a list of tips provided by Cyble to prevent ransomware attacks:
- Never click on unverified/unidentified links
- Do not open untrusted email attachments
- Only download from sites you trust
- Never use unfamiliar USBs
- Use security software and keep it updated
- Backup your data periodically
- Isolate the infected system from the network
- Use mail server content scanning and filtering
- Never pay the ransom.
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, REvil ransomware)
[adrotate banner=”5″]
[adrotate banner=”13″]


