
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Experts discovered a critical bug in Schneider Electric Vehicle Charging Stations

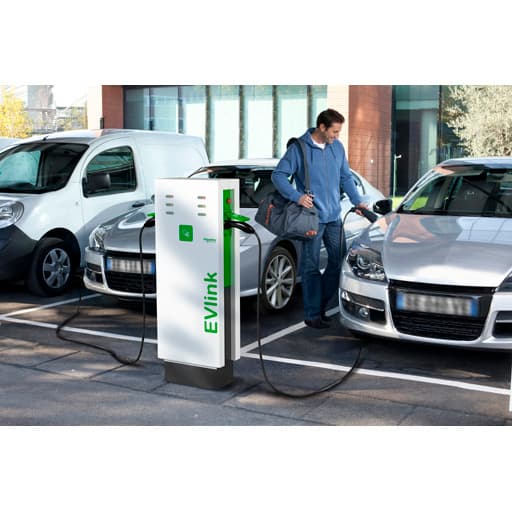
A critical vulnerability affects Schneider Electric electric vehicle charging stations, the EVLink Parking systems. EVlink Parking charging solutions are usually in parking environments, including offices, hotels, supermarkets, fleets, and municipals. According to the company, the issue is tied to a hard-coded credential bug that could be exploited by attackers to gain access to the system. […]

vehicle charging stations

A critical vulnerability affects Schneider Electric electric vehicle charging stations, the EVLink Parking systems.

EVlink Parking charging solutions are usually in parking environments, including offices, hotels, supermarkets, fleets, and municipals.

According to the company, the issue is tied to a hard-coded credential bug that could be exploited by attackers to gain access to the system.

vehicle charging stations

The flaw, tracked as CVE-2018-7800 affects the EVLink Parking floor-standing units, v3.2.0-12_v1 and earlier.

“A Hard-coded Credentials vulnerability exists which could enable an attacker to gain access to the device ” reads the security advisory published by Schneider Electric.

Schneider also addressed a code injection vulnerability tracked as CVE-2018-7801 and SQL injection bug tracked as CVE-2018-7802.

The code injection bug, rated as high severity (CVSS 8.8), could be exploited by an attacker to gain access with maximum privileges to the system when remote code execution is performed,

“A Code Injection vulnerability exists which could enable access with maximum privileges when a remote code execution is performed.” continues the advisory.

The SQL Injection vulnerability, rated as medium severity
(CVSS 6.4) could give access to the web interface with full privileges.

The CVE-2018-7801 flaw was reported by Vladimir Kononovich and Vyacheslav Moskvin from Positive Technologies, while the CVE-2018-7800 and CVE-2018-7802 issue were discovered by Vladimir Kononovich from Positive Technologies.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, Vehicle Charging Stations)

[adrotate banner=”5″] [adrotate banner=”13″]


