
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Chronicle launches VirusTotal Monitor to reduce false positives

Alphabet owned cybersecurity firm Chronicle announced the launch of a new VirusTotal service that promises to reduce false positives.  VirusTotal Monitor service allows developers to upload their application files to a private cloud store where they are scanned every day using anti-malware solutions from antivirus vendors in VirusTotal. Every time the service flags the file as malicious, […]

VirusTotal Monitor

Alphabet owned cybersecurity firm Chronicle announced the launch of a new VirusTotal service that promises to reduce false positives. 

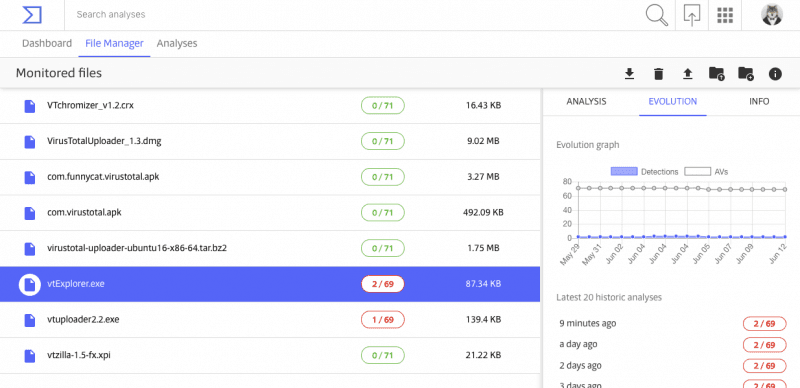
VirusTotal Monitor service allows developers to upload their application files to a private cloud store where they are scanned every day using anti-malware solutions from antivirus vendors in VirusTotal.

Every time the service flags the file as malicious, VirusTotal notifies it to antivirus vendor and to the developer.

Of course, files analyzed by the VirusTotal Monitor service will remain private and are not shared by the company with third-parties.

The service implements a Google-drive like interface to allow developers to upload their files and a dashboard to display the scan results. Both developers and AV companies could access the dashboard, the service also provided APIs to integrate Monitor with their tools implemented by developers and antivirus vendors.

“Enter VirusTotal Monitor. VirusTotal already runs a multi-antivirus service that aggregates the verdicts of over 70 antivirus engines to give users a second opinion about the maliciousness of the files that they check.” reads the announcement published by VirusTotal.

“For antivirus vendors this is a big win, as they can now have context about a file: who is the company behind it? when was it released? in which software suites is it found? What are the main file names with which it is distributed? For software developers it is an equally big win, as they can upload their creations to Monitor at pre-publish stage, to ensure a release without issues.”

VirusTotal Monitor

VirusTotal pointed out that Monitor service is not a free pass to get any file whitelisted.

“Sometimes vendors will indeed decide to keep detections for certain software, however, by having contextual information about the author behind a given file, they can prioritize work and take better decisions, hopefully leading to a world with less false positives,” continues the announcement.

“The idea is to have a collection of known source software, then each antivirus can decide what kind of trust-based relationship they have with each software publisher.”

Are you interested in this service? Now you can request a trial period for VirusTotal Monitor.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(Security Affairs – VirusTotal Monitor, malware)

[adrotate banner=”5″]

[adrotate banner=”13″]


